Levantamento técnico
Mapping of critical applications, access, traffic and dependencies.
Network security, secure access, cloud and security operations. Add Solution helps turn technical requirements into a coherent architecture, with selection, integration and deployment aligned with your environment.
This page presents a selection of models and families. Availability, licenses, versions and composition are confirmed in the proposal.
 SECURE NETWORKINGSECURITY OPERATIONSUNIFIED MANAGEMENT
Use the filters to explore models with official photography available. The technical source retains other models awaiting their exact image for publication.
Sizing starts with applications, links, networks, identities, clouds and continuity requirements.
Mapping of critical applications, access, traffic and dependencies.
Selection of families, interfaces, capacity and controls with an explicit methodology.
Subscriptions, support and optional functions are itemized in the scope.
Change, validation, continuity and responsibilities are planned with operations.
Firewalls, secure access, workload protection and security operations play distinct roles and need to share objectives, policies and telemetry.
The architecture defines where to apply controls, how to connect environments and which responsibilities belong to the platform, deployment and operations.
The choice combines architecture, model, version, licenses, interfaces and capacity with enabled controls.
The project organizes requirements, architecture, sizing, licensing, deployment and support within a verifiable scope.
Expansion, refresh and segmentation require assessing the current configuration, compatibility, lifecycle and the effect of change on services.
Software and service capabilities are assessed by edition, license, integration, region and operational responsibility. They do not represent physical appliances.
Policy enforcement follows the virtual architecture. The choice considers the hypervisor or cloud, vCPU, performance with inspection, licensing and network integration mechanisms.
Deployment must follow cluster topology, the data path, supported network plugins and resource consumption. It is not simply a copy of the physical firewall in containers.
Validate the provider, region, integrations, billing and operational responsibilities. The vendor's managed service does not eliminate the need to define policies and traffic paths.
Capacidades de software e serviços são avaliadas por edição, licença, integração, região e responsabilidade operacional. Não representam appliances físicos.
Centralizes configuration and visibility for compatible NGFW and Prisma Access. Features depend on edition, licenses and associated services; logging, retention and data residency requirements must be included in the project.
The architecture must separate management, log collection, capacity, high availability and compatible versions. Assess continuity for existing environments and the management strategy before proposing a migration.
Advanced Threat Prevention, Advanced WildFire, Advanced URL Filtering, Advanced DNS Security and Enterprise DLP serve distinct objectives. Availability and requirements vary by platform, license and version; do not assume they are all included with the hardware.
Capacidades de software e serviços são avaliadas por edição, licença, integração, região e responsabilidade operacional. Não representam appliances físicos.
The design starts with identity, applications, connectivity and policies. Check regions, connectors, bandwidth, user experience and the purchased license.
Size links, topology, ION equipment or compatible instances, policies and integration dependencies. Prisma SD-WAN and PAN-OS SD-WAN are different offerings; selection must not treat their licenses as interchangeable.
It can complement application access according to the architecture adopted. Validate application, device and identity compatibility and required controls before expanding use.
Capacidades de software e serviços são avaliadas por edição, licença, integração, região e responsabilidade operacional. Não representam appliances físicos.
Connect relevant sources and define investigation, responsibilities and response. Coverage depends on edition, agents and integrations; installing a license does not constitute a SOC operation.
Adoption requires planning for ingestion, use cases, retention, integrations and response processes. The platform's technical capability and the human operational service are distinct project components.
Combines posture, application and runtime capabilities. Scope must follow relevant accounts, workloads and pipelines; existing Prisma Cloud environments require their own edition and transition assessment, without assuming automatic contract conversion.
Compartilhe o contexto da operação, quantidade de usuários, localidades e objetivos do projeto. A equipe Add Solution direcionará a conversa para especialistas em arquitetura, dimensionamento, licenciamento e implantação Palo Alto Networks.
Share applications, sites, access and continuity requirements for a technical selection aligned with the project.
Selecione um produto para consultar especificações, contexto de aplicação e documentos oficiais.
Valores publicados pelo fabricante. O dimensionamento final considera arquitetura, tráfego, serviços ativos, redundância e crescimento.
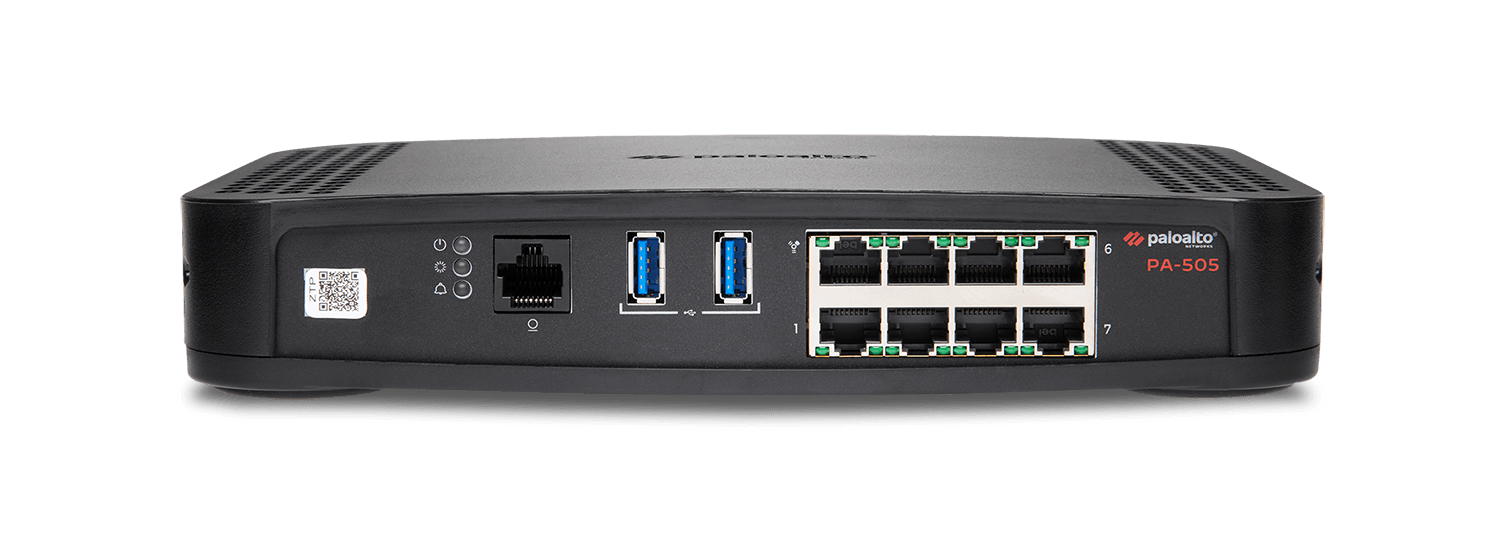
PA-505: Compact alternative with greater session capacity than the PA-501.
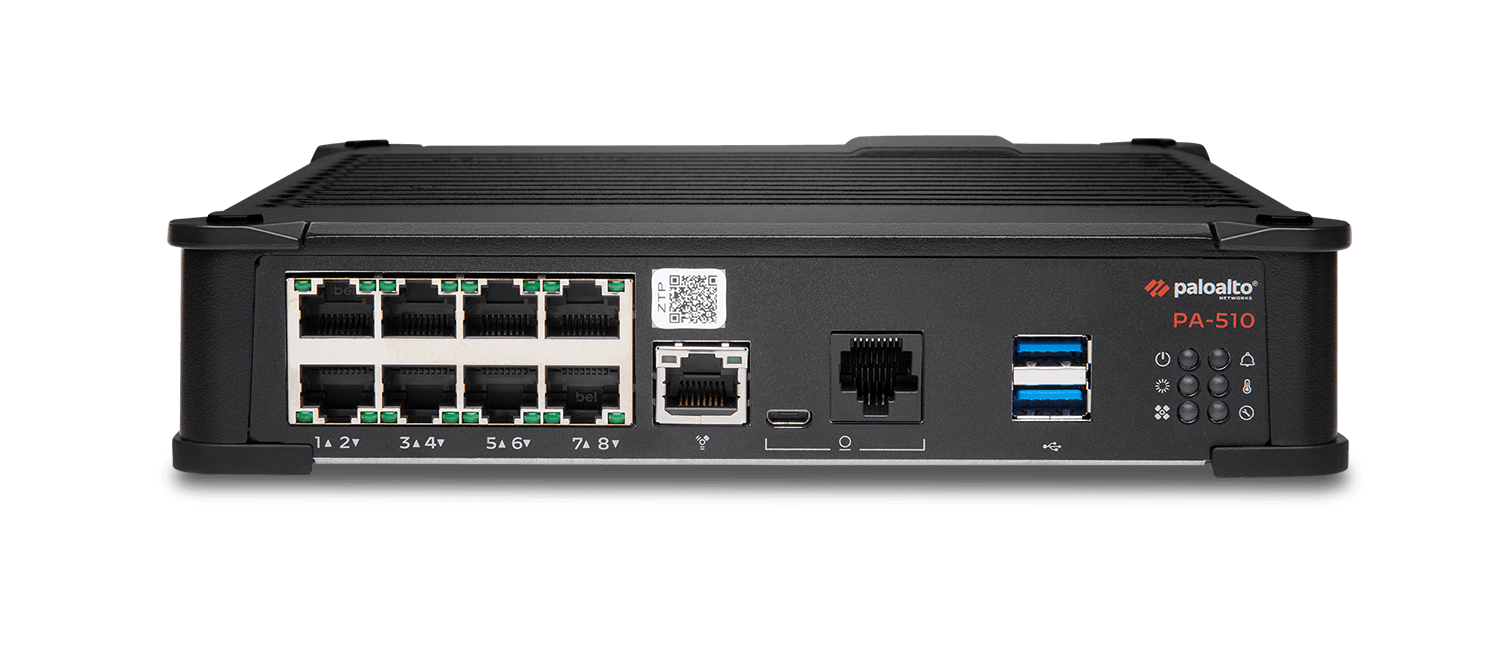
PA-510: One additional data port and greater capacity than the 501/505 models.
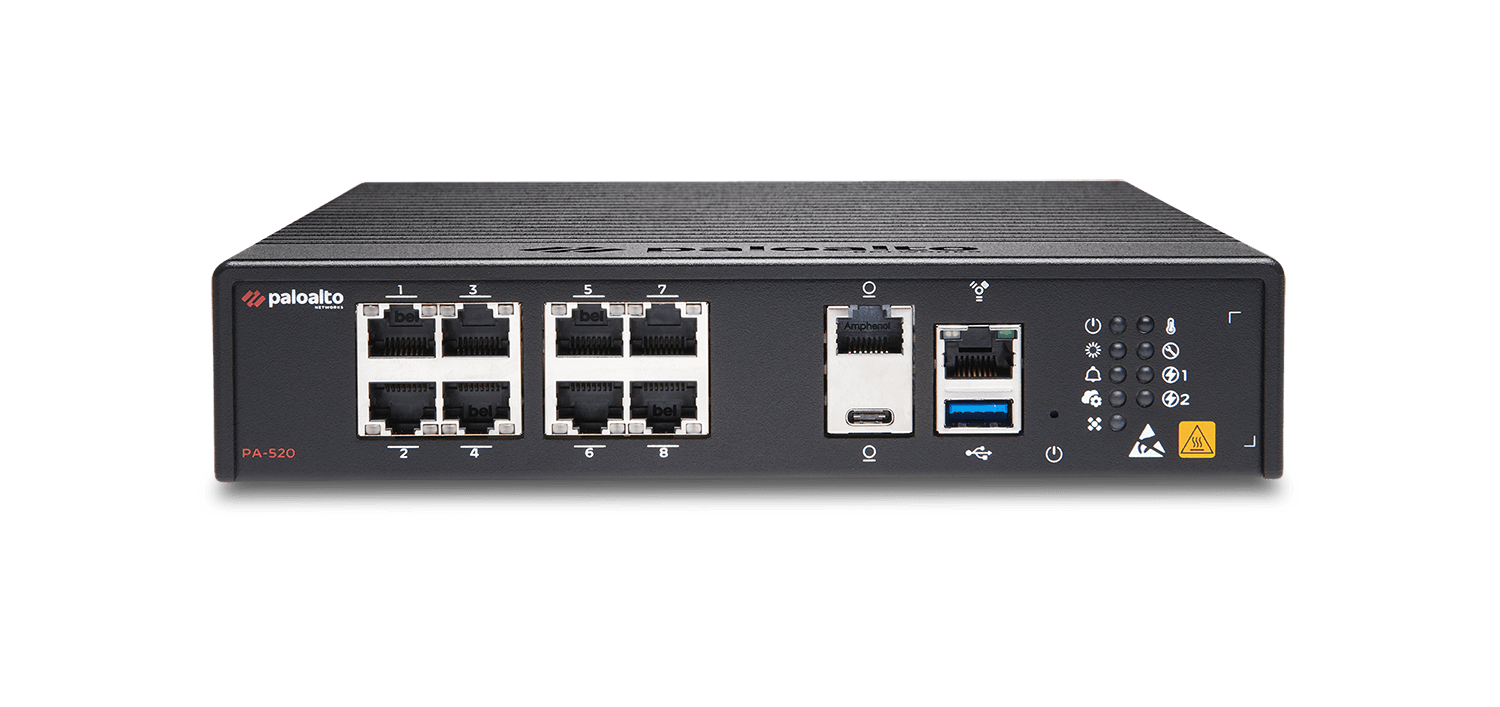
PA-520: Wired branches that need more capacity without fibre uplinks.
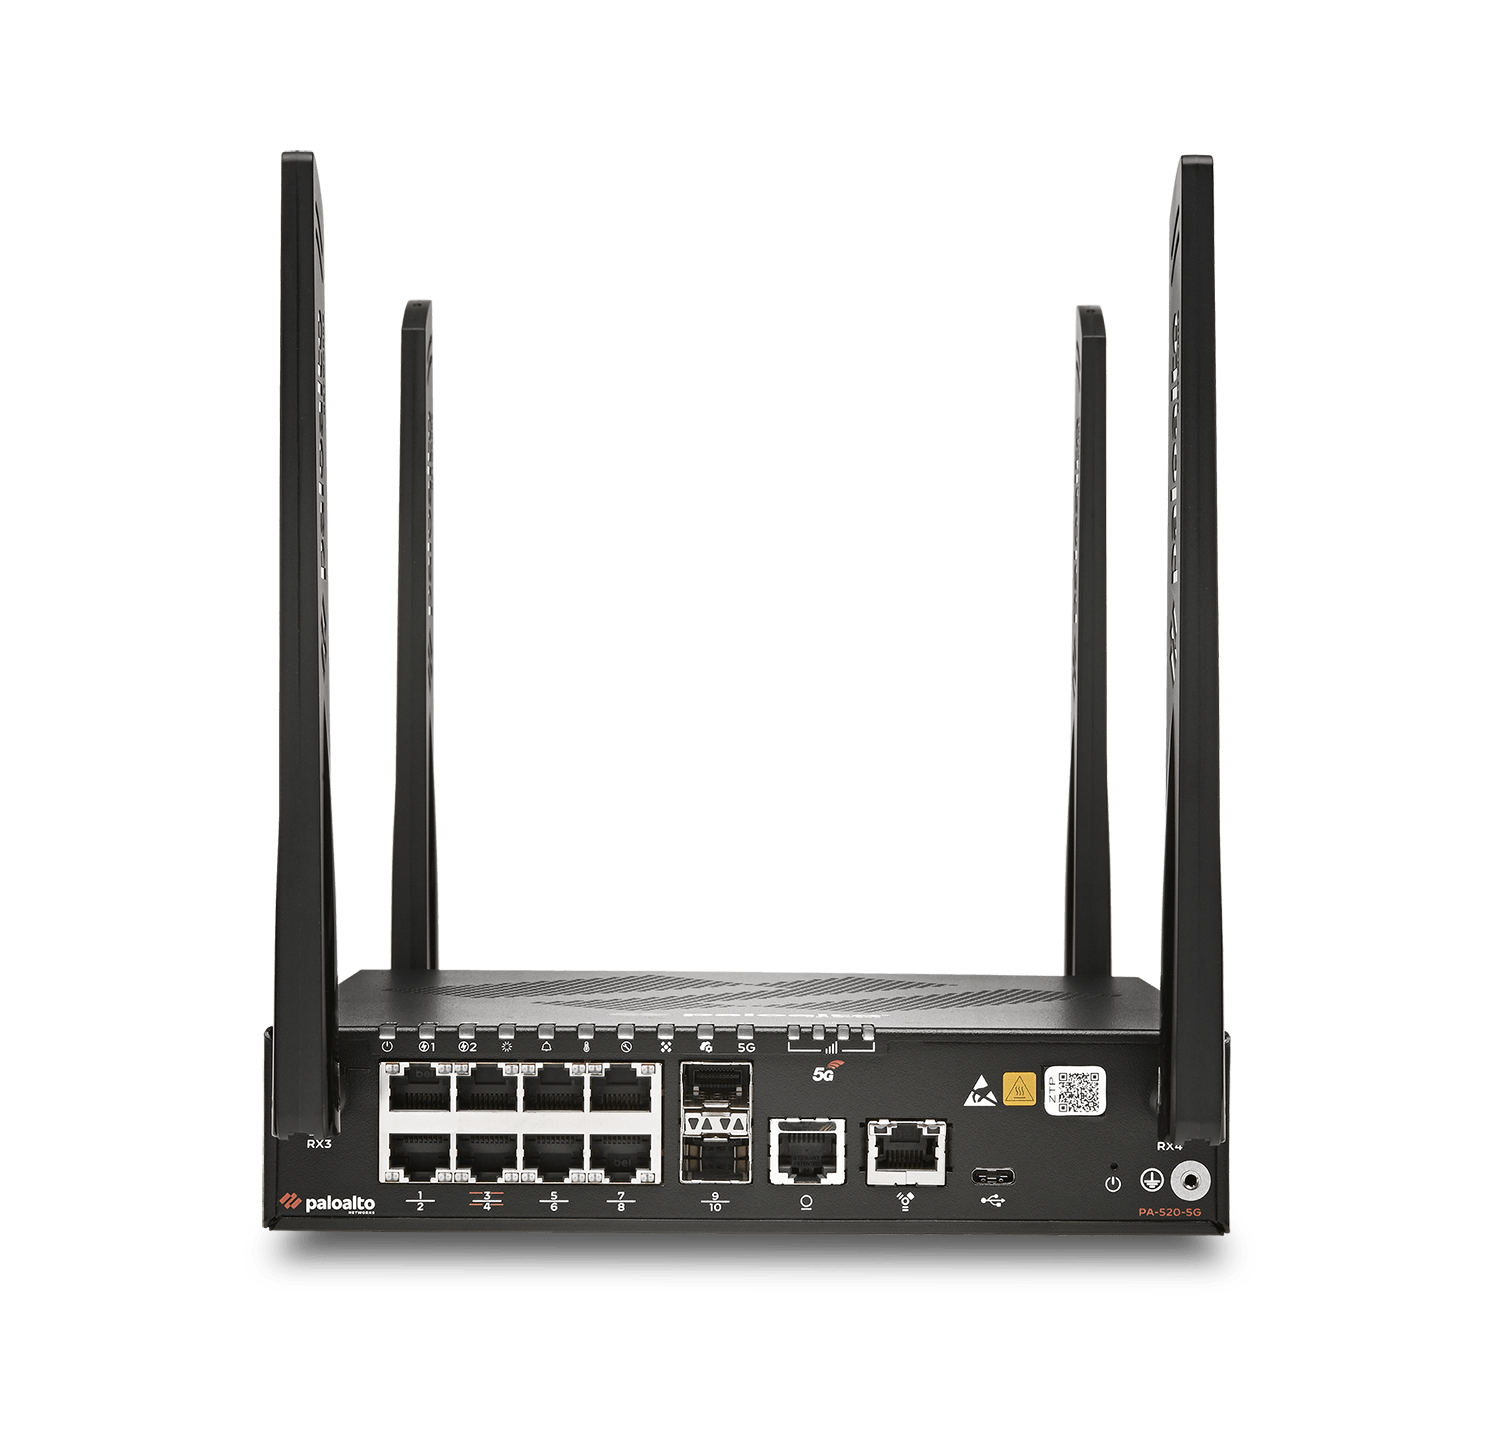
PA-520-5G: Cellular and Gigabit fibre connectivity for branches with specific WAN requirements.
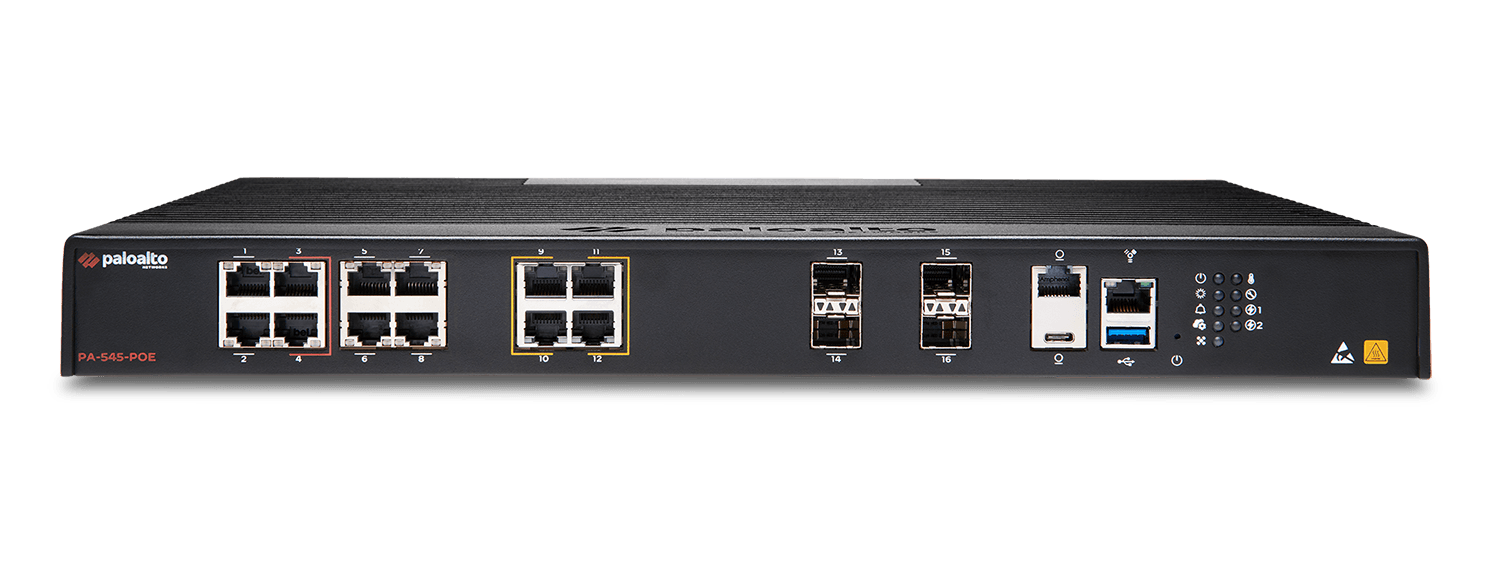
PA-545-POE: PoE power on 4 multigigabit ports for edge devices.
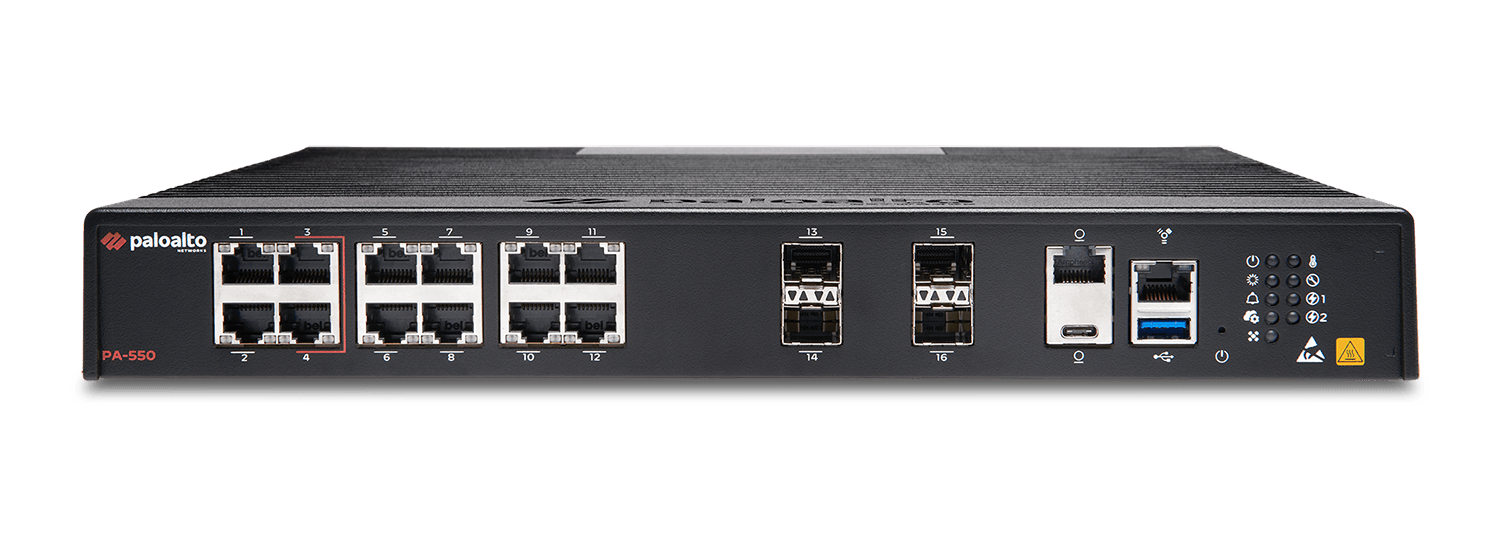
PA-550: 10 GbE uplinks and higher wired-port density, without integrated PoE.
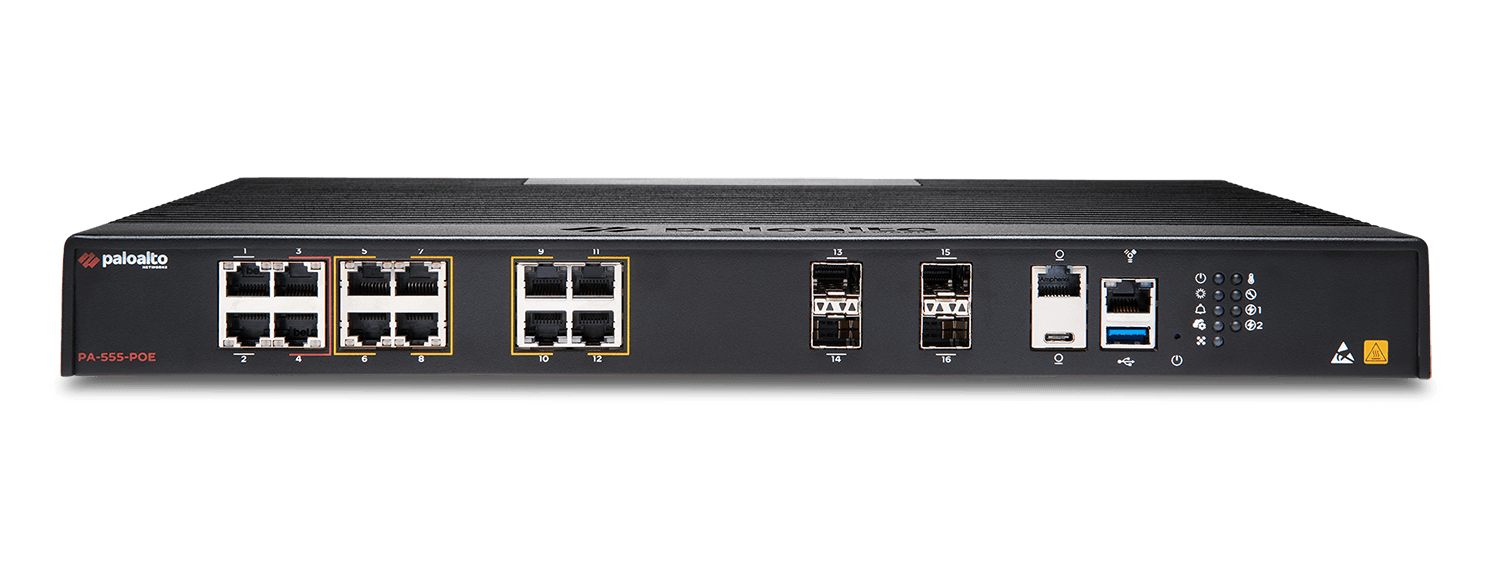
PA-555-POE: Eight PoE ports and 10 GbE uplinks to aggregate branch connectivity.
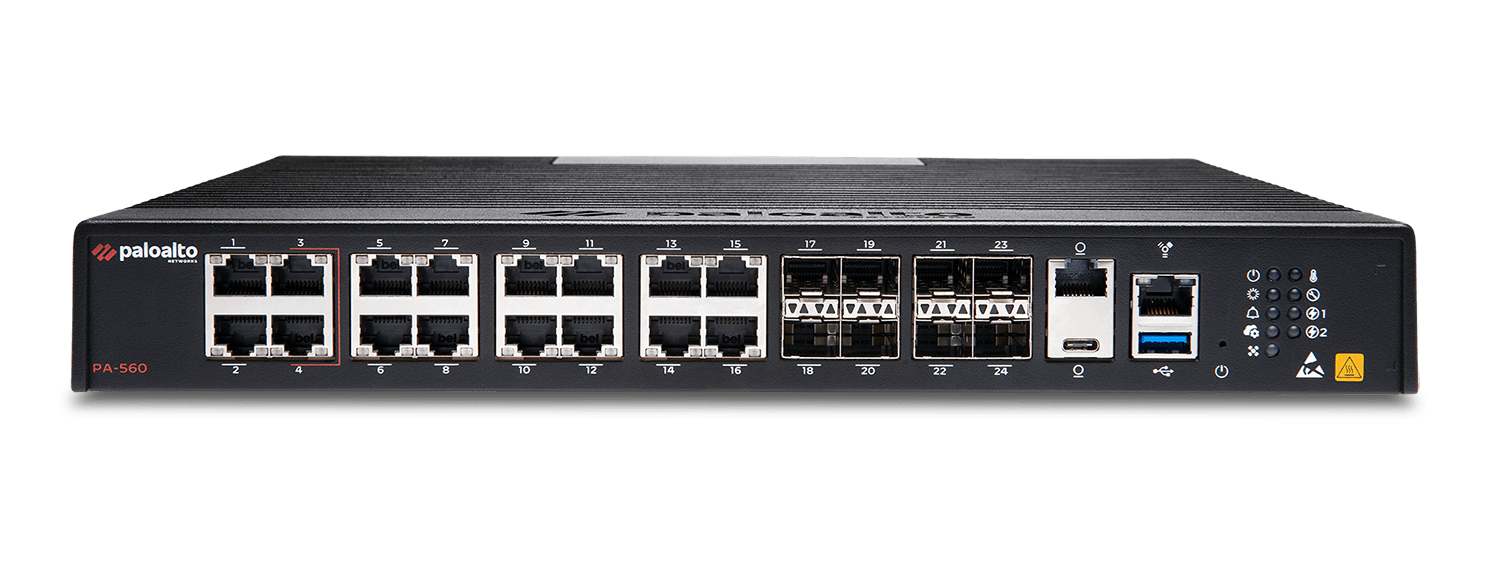
PA-560: Highest density in the wired family, with 4 × 10 GbE uplinks and 24 data ports.
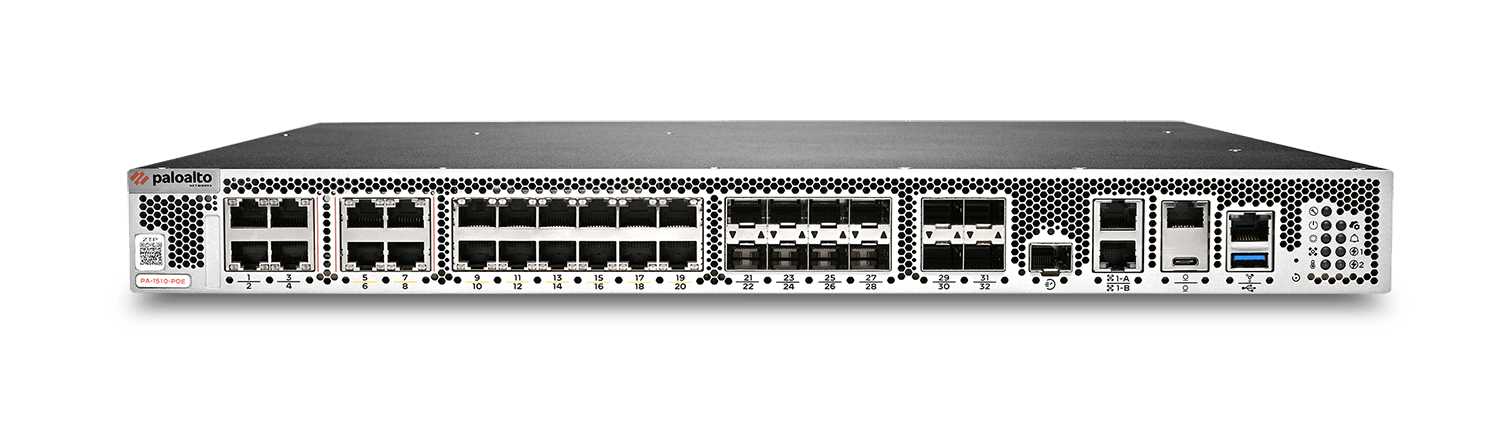
1U firewall with 9 Gbps of threat prevention in appmix, 20 copper ports and a 485 W PoE budget.
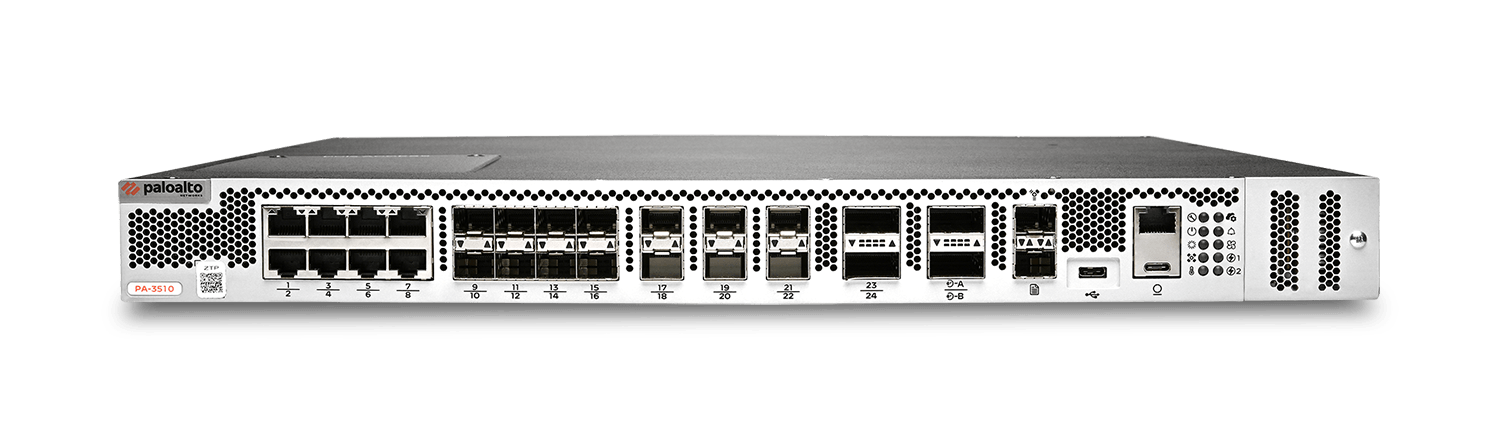
1U firewall with 15 Gbps of threat prevention in appmix and two 100 GbE interfaces.
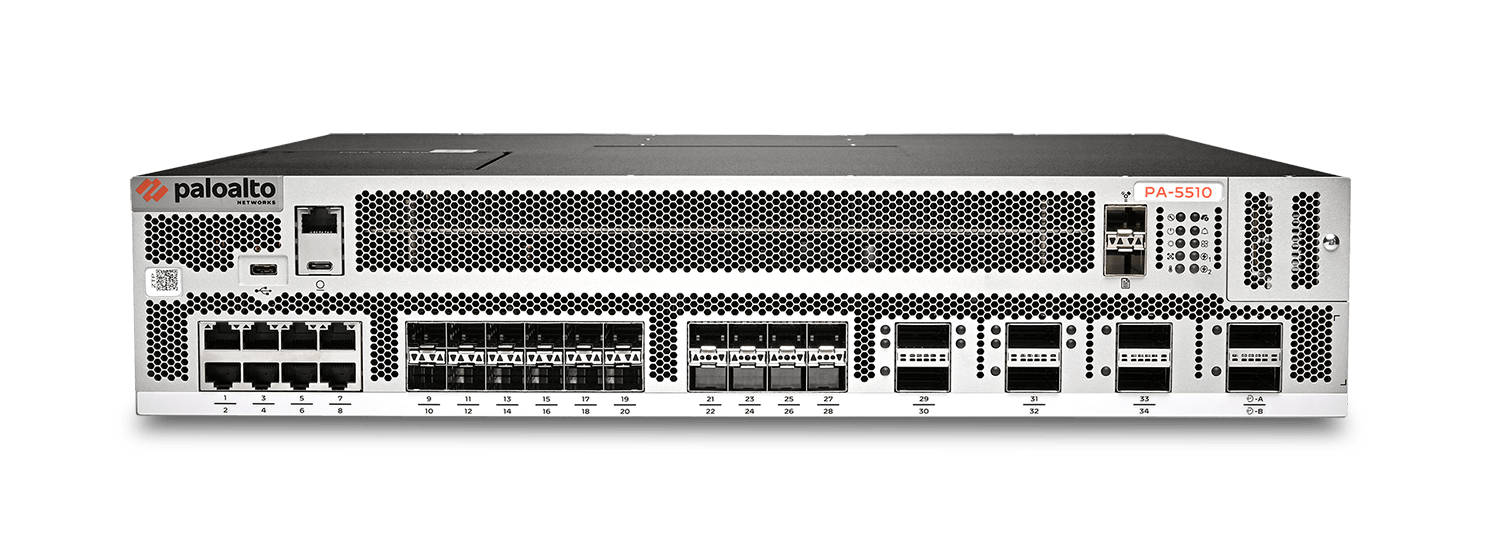
2U firewall with 45 Gbps of threat prevention in appmix, six 100 GbE ports and RAID 1 storage.
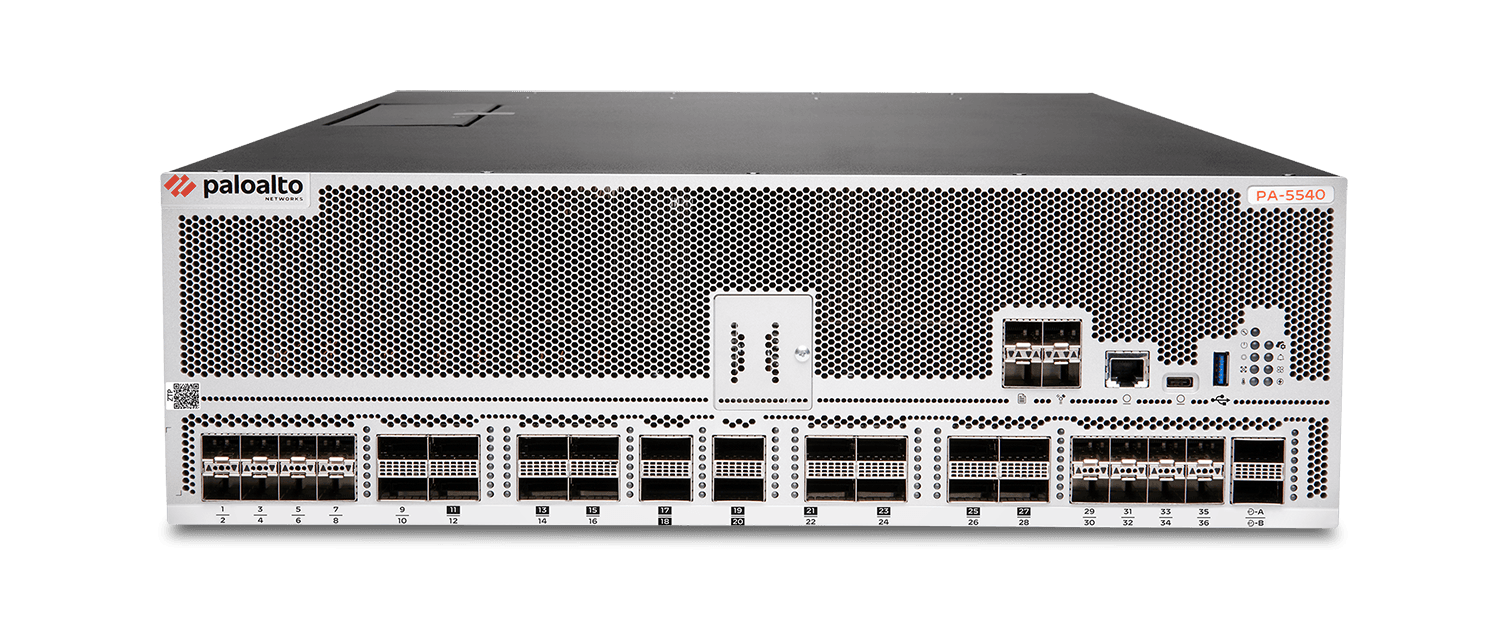
PA-5540: Traffic aggregation with 4 × 400 GbE interfaces and 90 Gb/s Threat Prevention appmix.
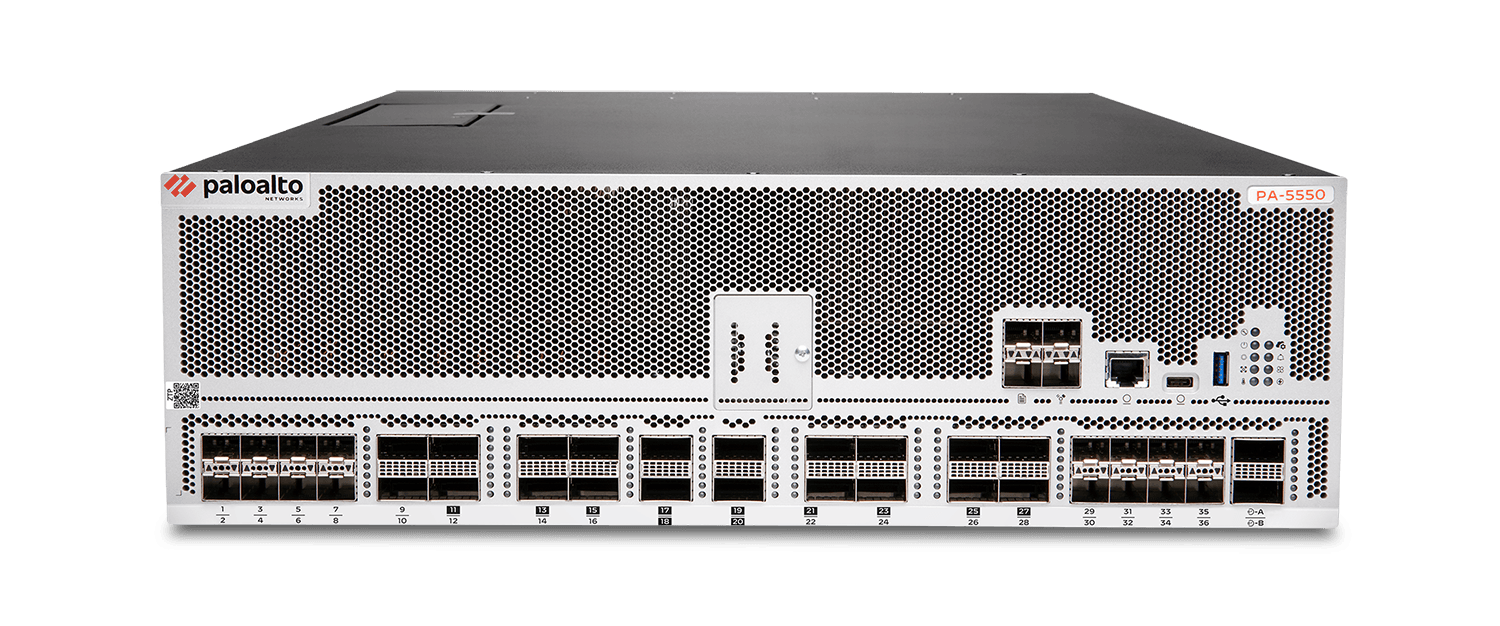
PA-5550: Traffic aggregation with 4 × 400 GbE interfaces and 120 Gb/s Threat Prevention appmix.
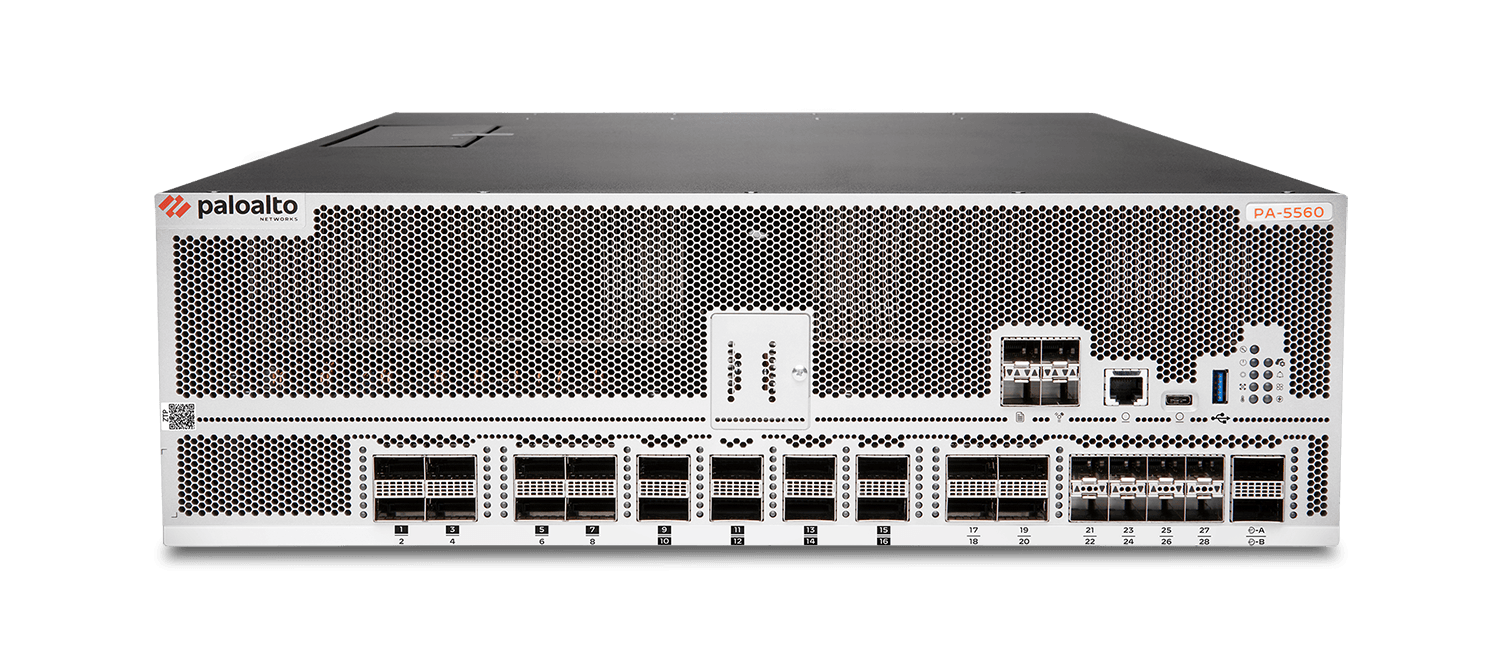
PA-5560: Traffic aggregation with 8 × 400 GbE interfaces and 180 Gb/s Threat Prevention appmix.
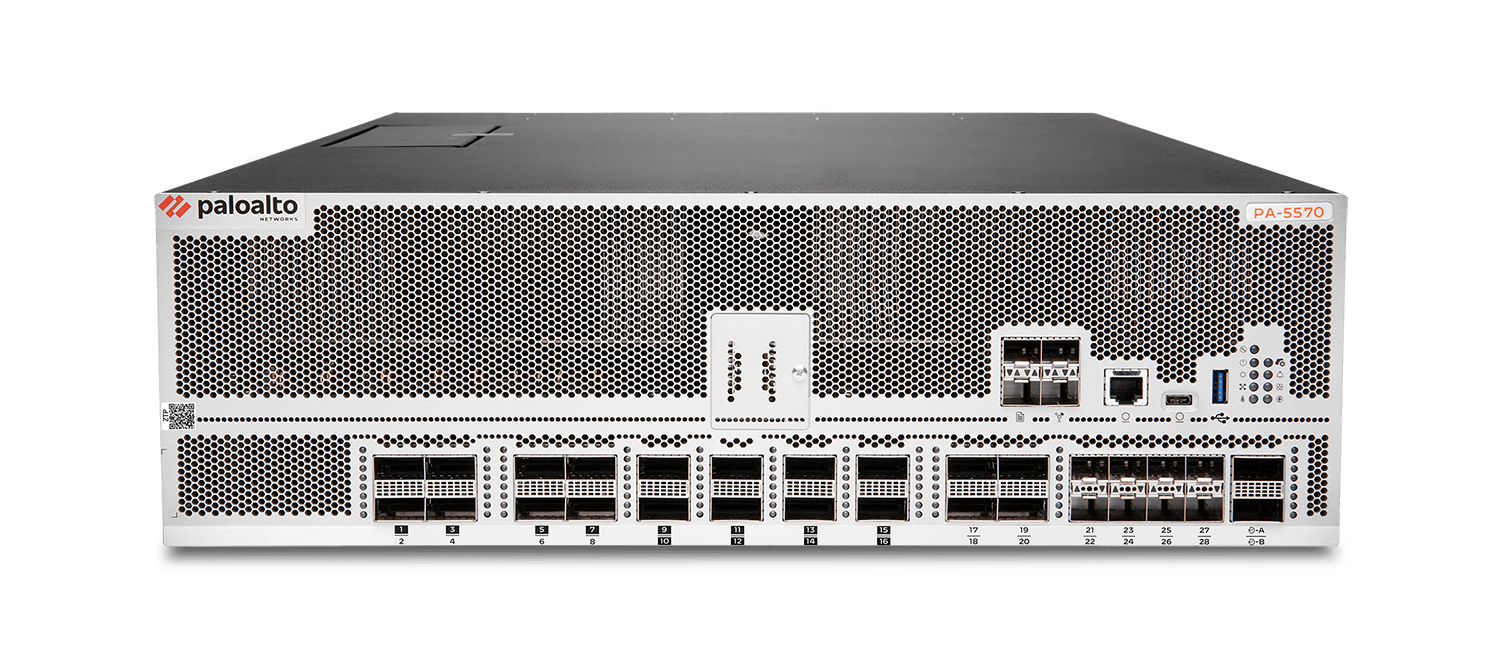
PA-5570: Traffic aggregation with 8 × 400 GbE interfaces and 240 Gb/s Threat Prevention appmix.
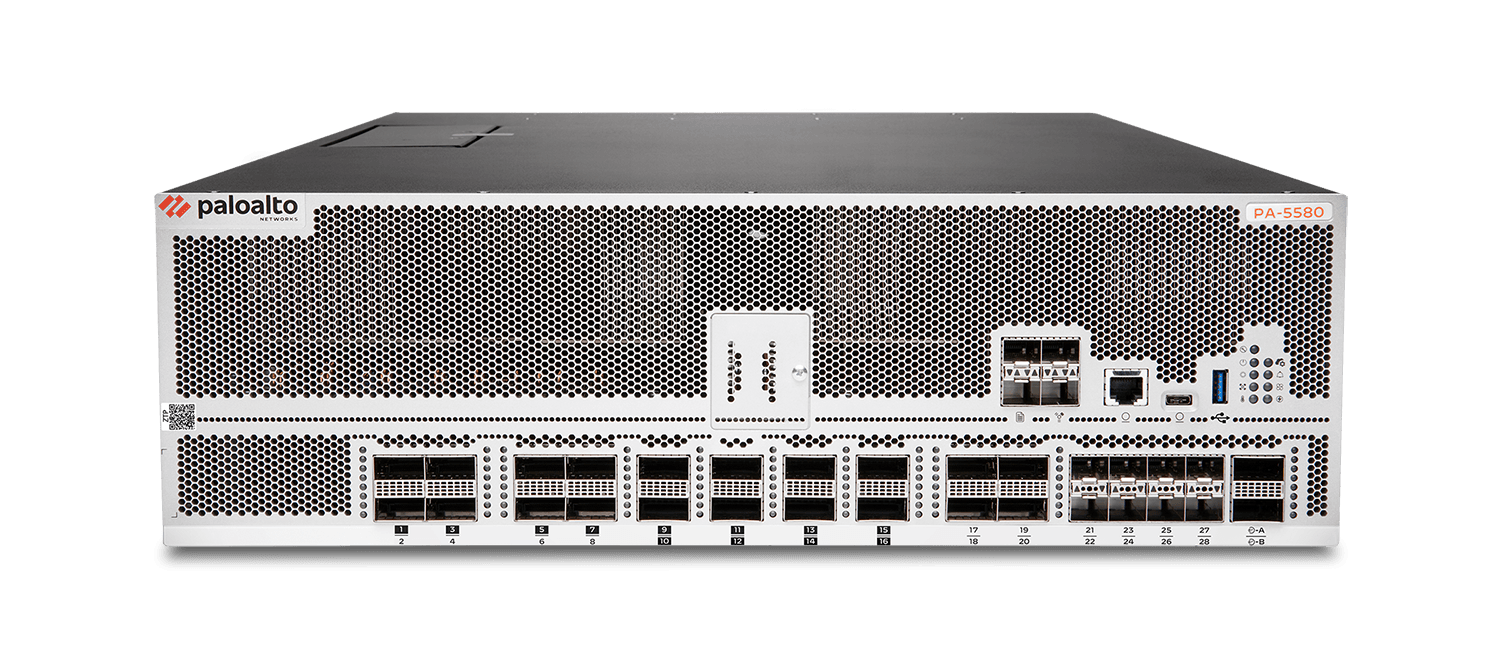
PA-5580: Traffic aggregation with 8 × 400 GbE interfaces and 300 Gb/s Threat Prevention appmix.
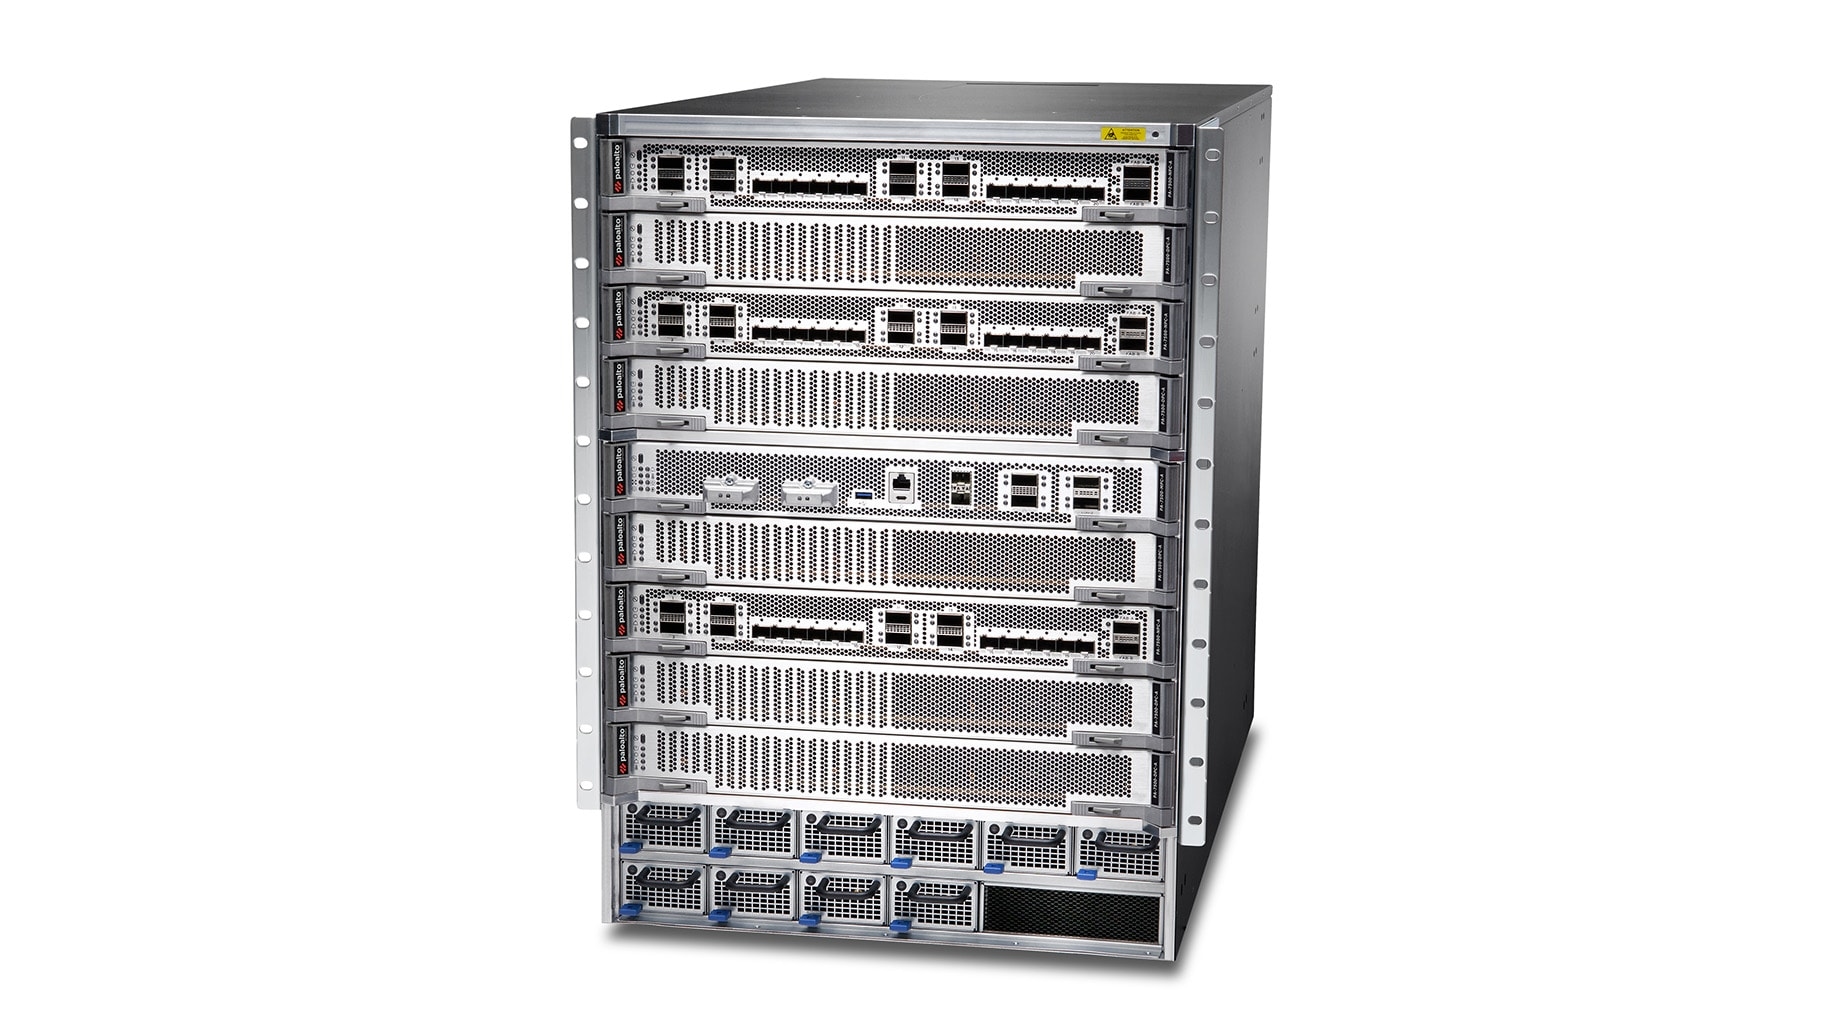
PA-7500: Modular platform whose capacity depends on the number and combination of cards.
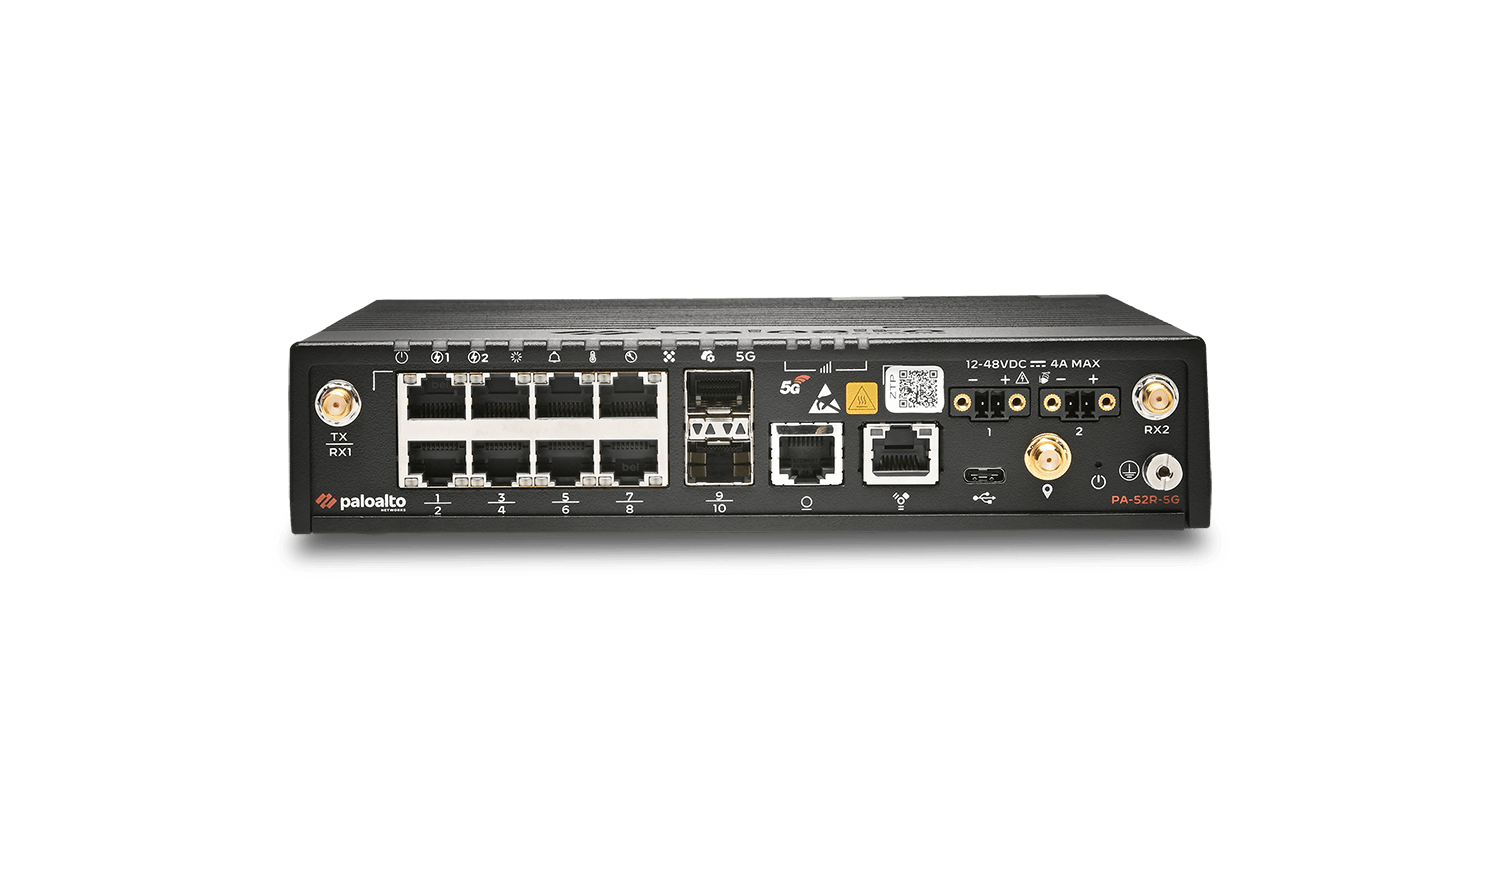
Compact industrial firewall with 5G RedCap, eight Gigabit ports and two DC inputs.
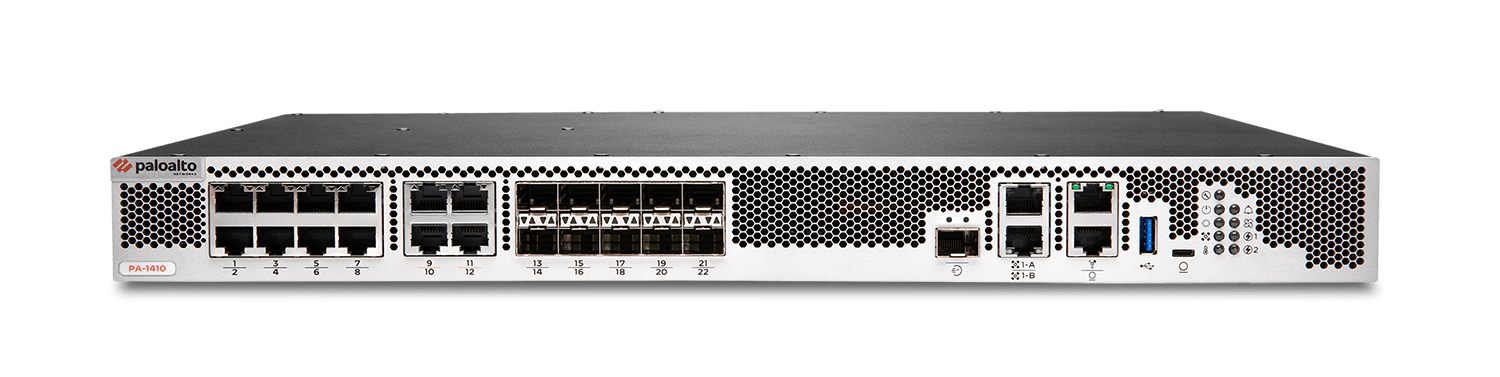
PA-1410: 1U rack integration with 4 × 10 GbE uplinks and PoE for the enterprise edge.
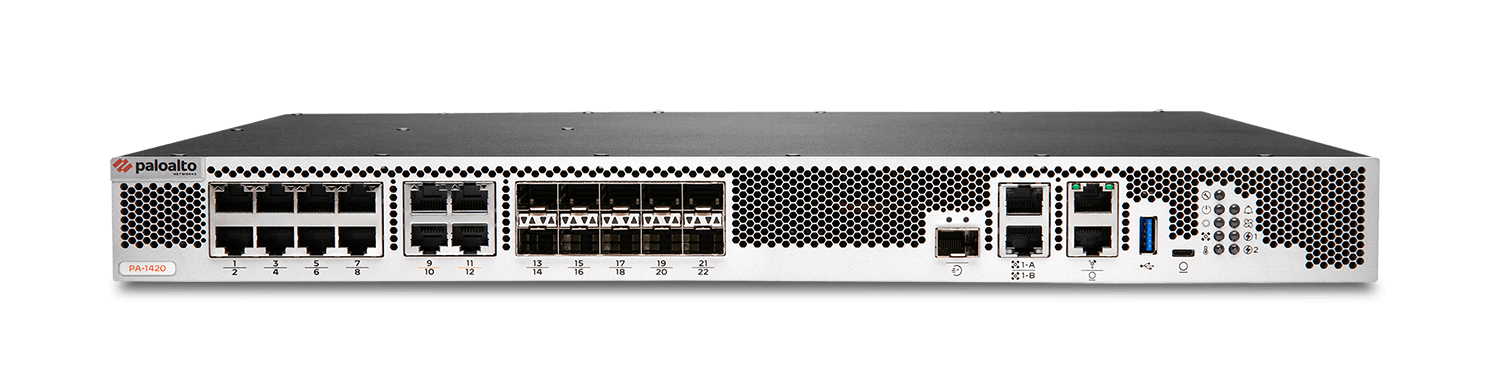
PA-1420: 1U rack integration with 8 × 10 GbE uplinks and PoE for the enterprise edge.
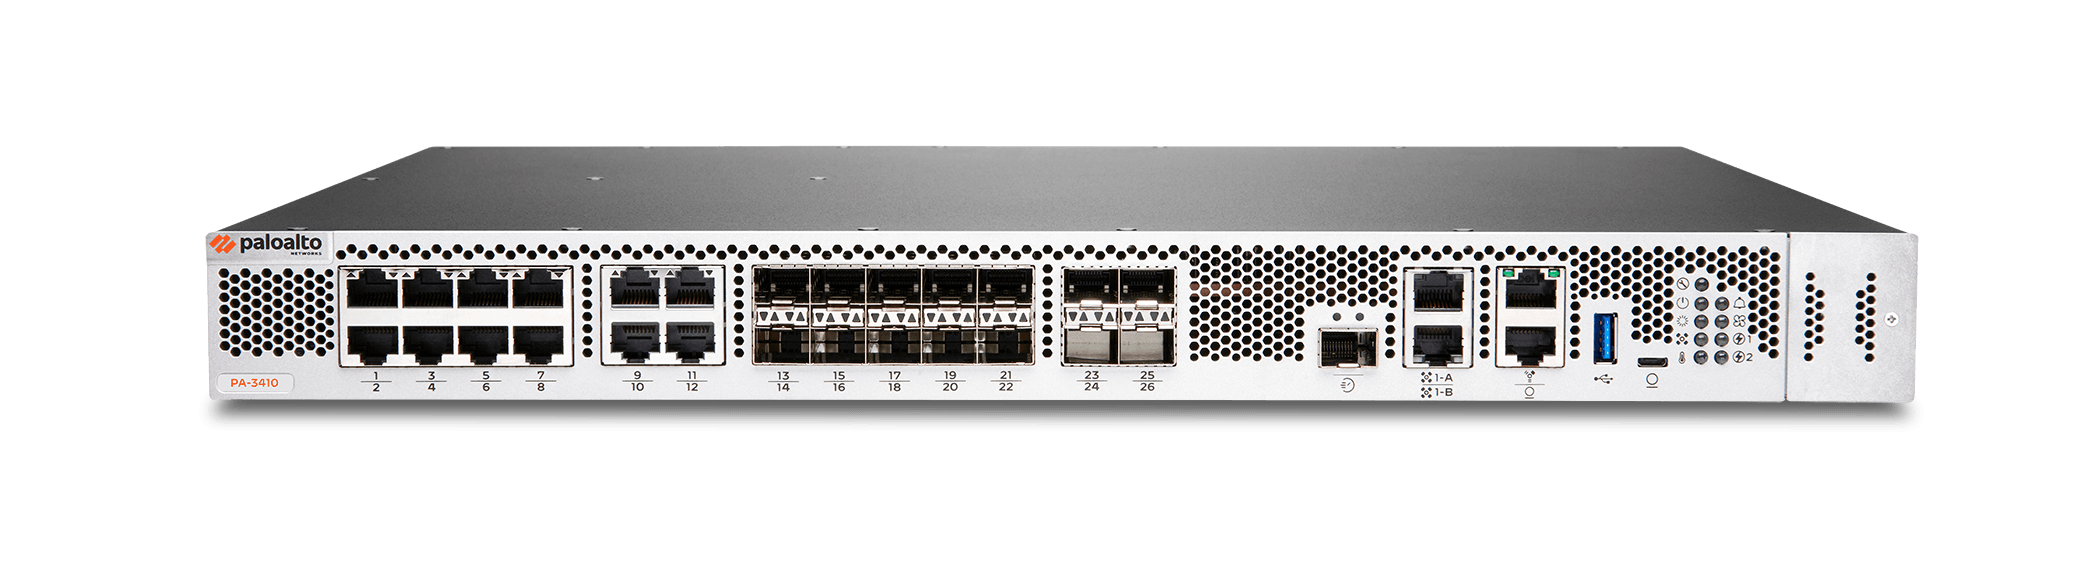
PA-3410: Enterprise edge in 1U with 25 GbE uplinks and 7.5 Gb/s Threat Prevention appmix capacity.
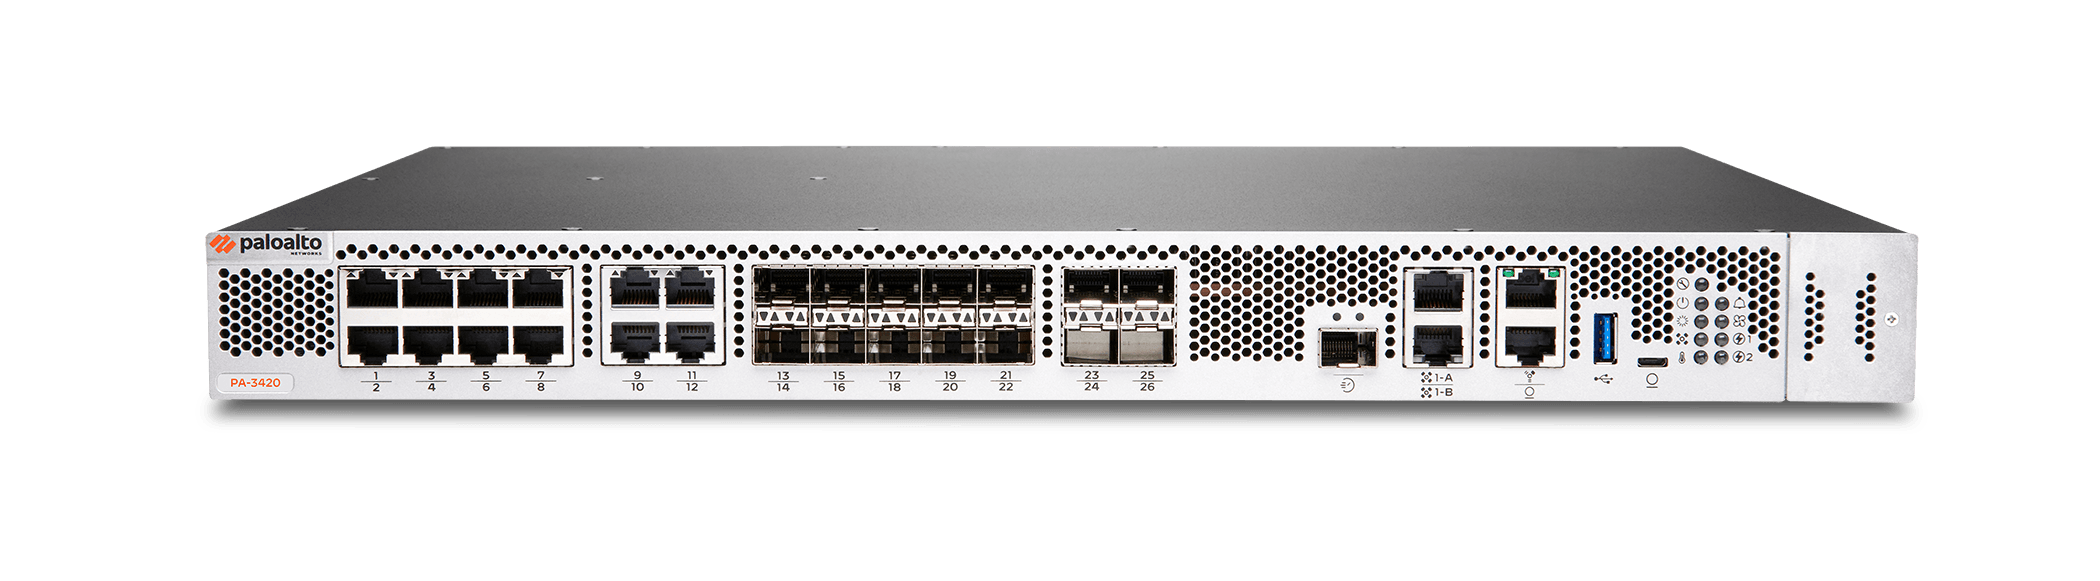
PA-3420: Enterprise edge in 1U with 25 GbE uplinks and 10 Gb/s Threat Prevention appmix capacity.
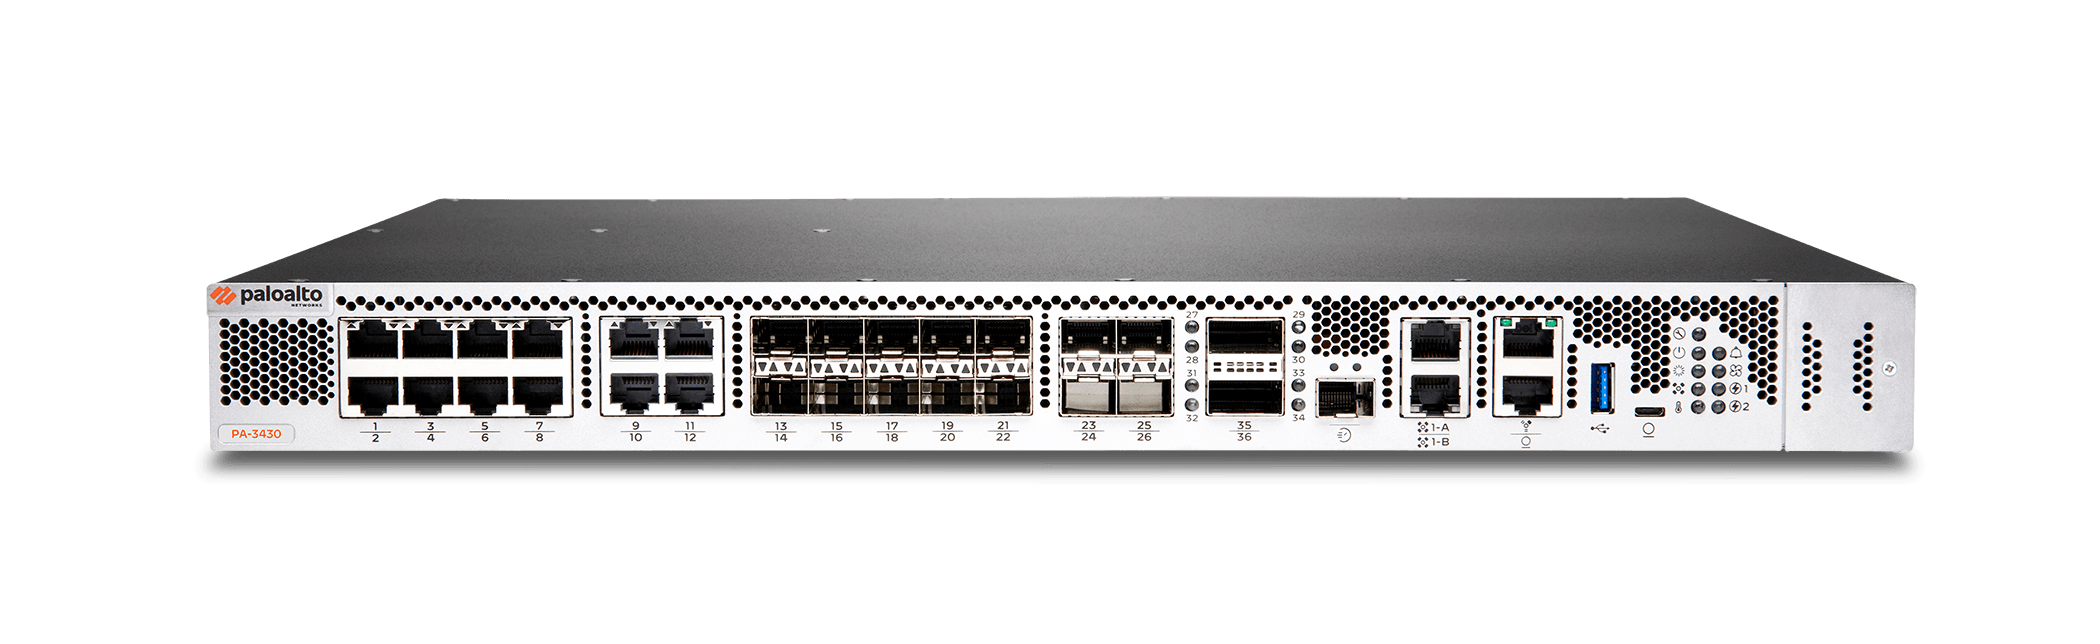
PA-3430: 100 GbE connectivity in a 1U rack form factor with 15 Gb/s Threat Prevention appmix capacity.
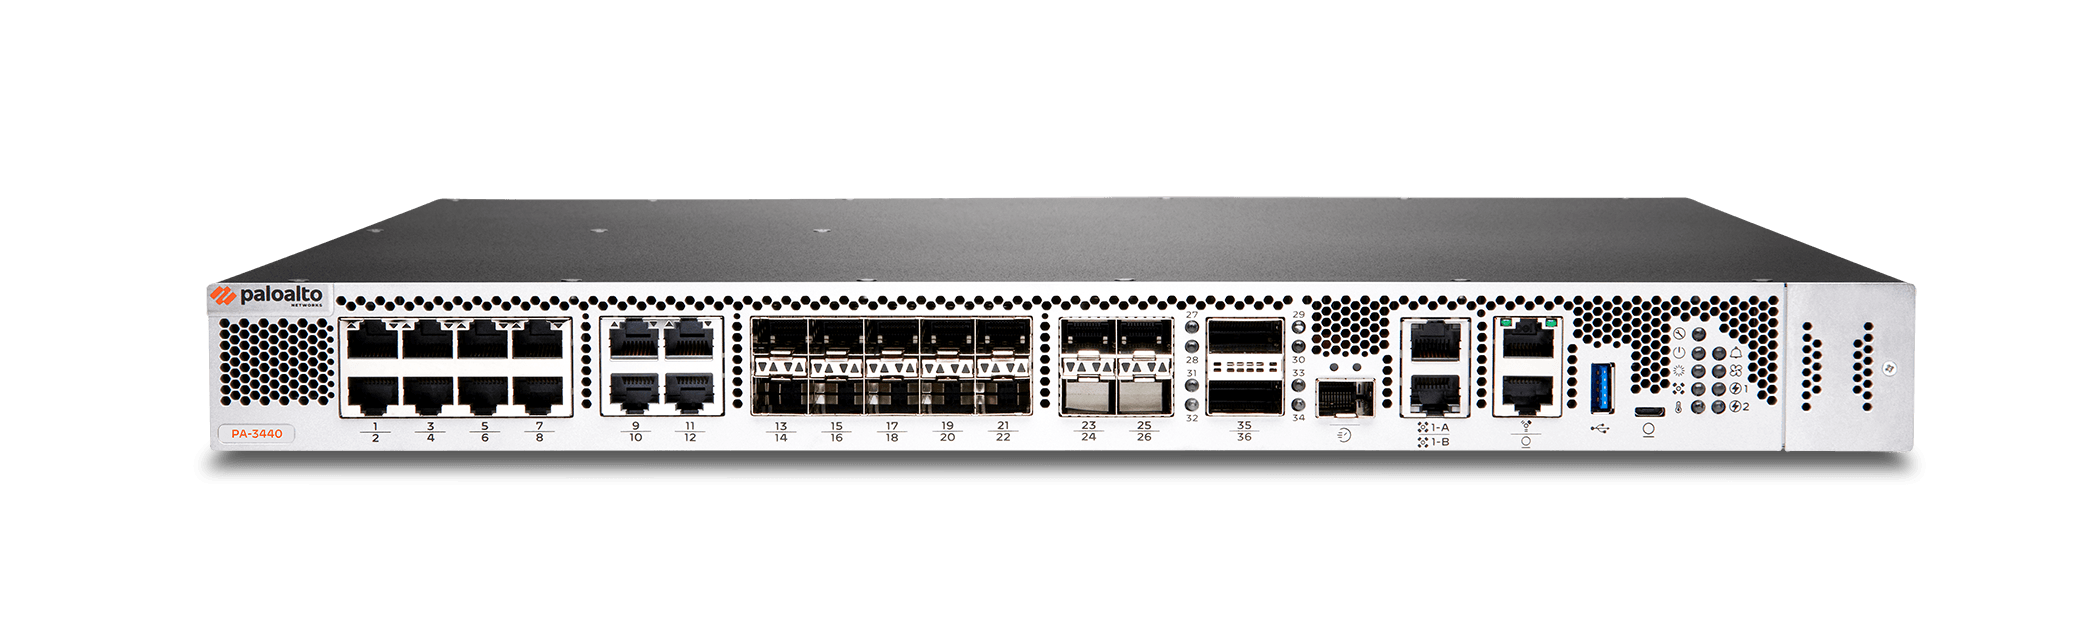
PA-3440: 100 GbE connectivity in a 1U rack form factor with 20 Gb/s Threat Prevention appmix capacity.
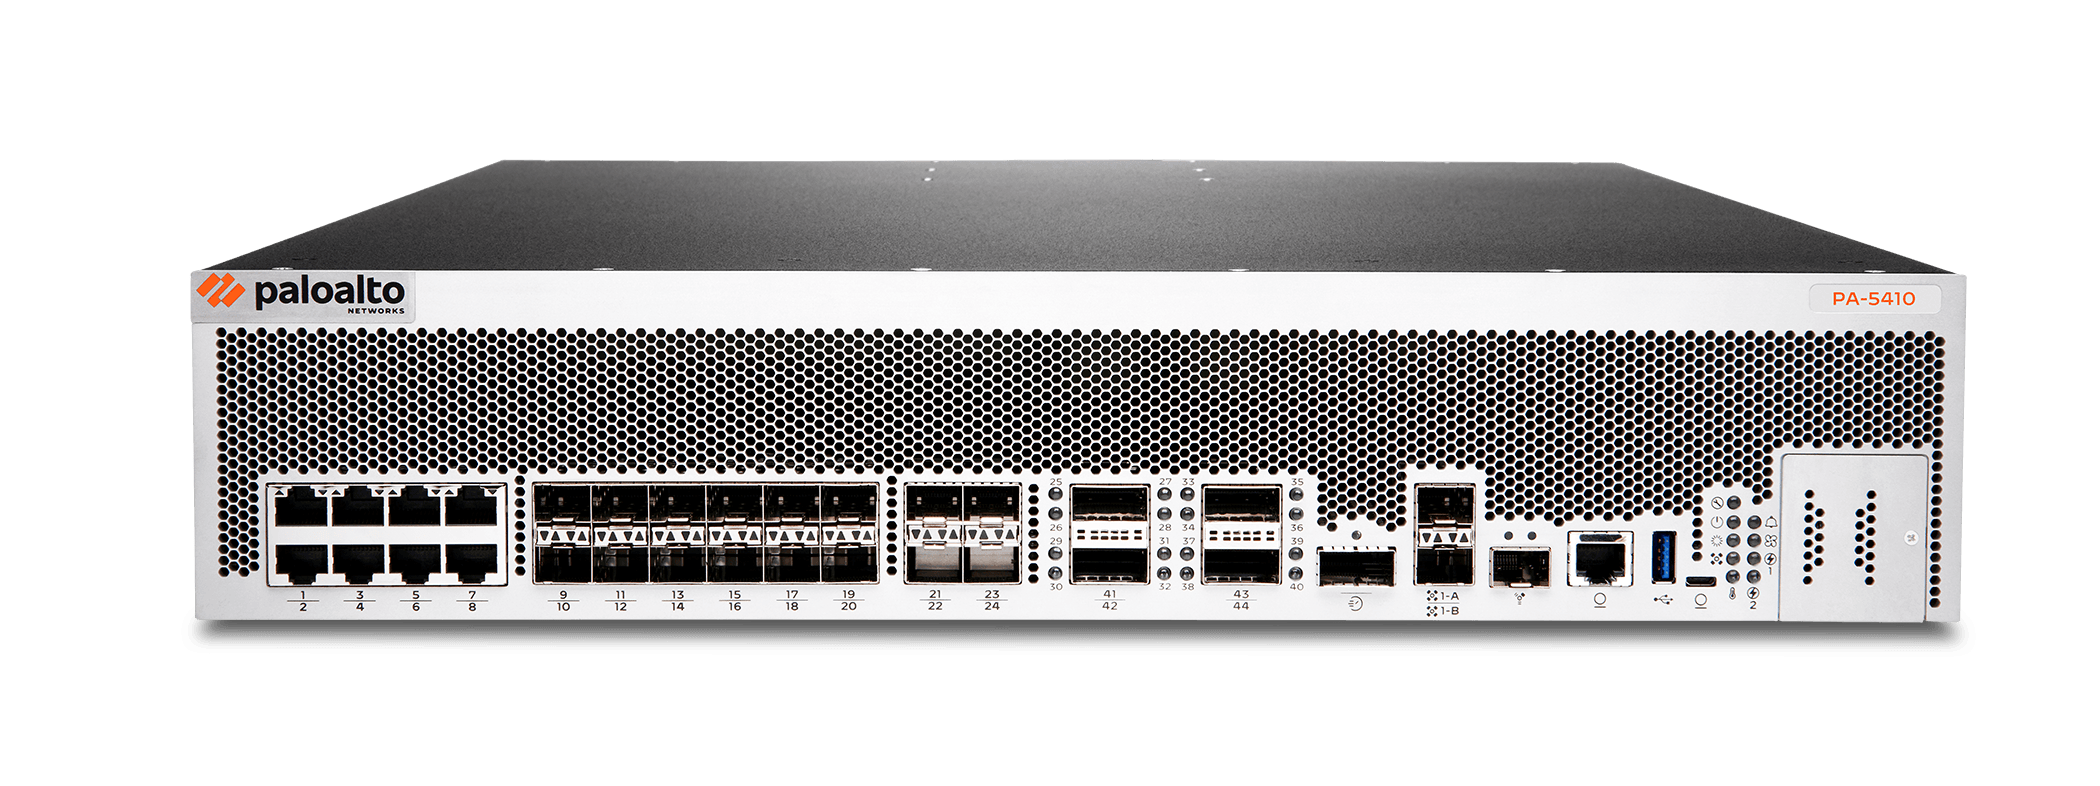
PA-5410: Fixed 2U form factor with up to 5 million sessions and 10 virtual systems in the base configuration.
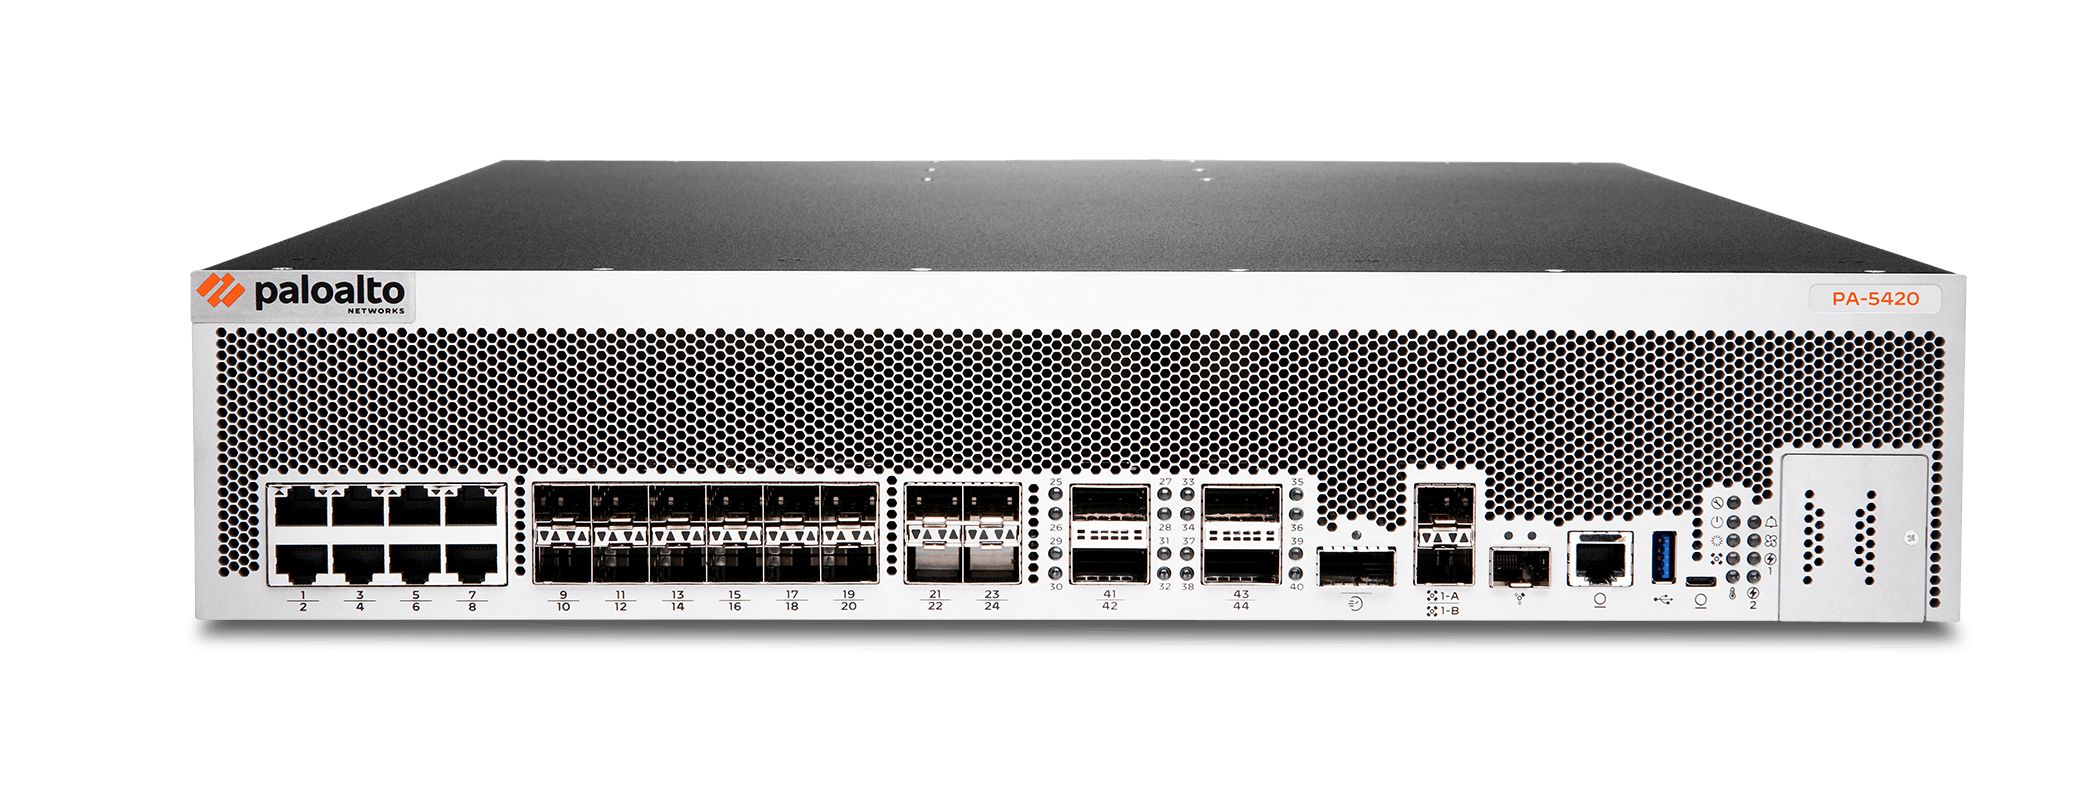
PA-5420: Fixed 2U form factor with up to 7 million sessions and 15 virtual systems in the base configuration.
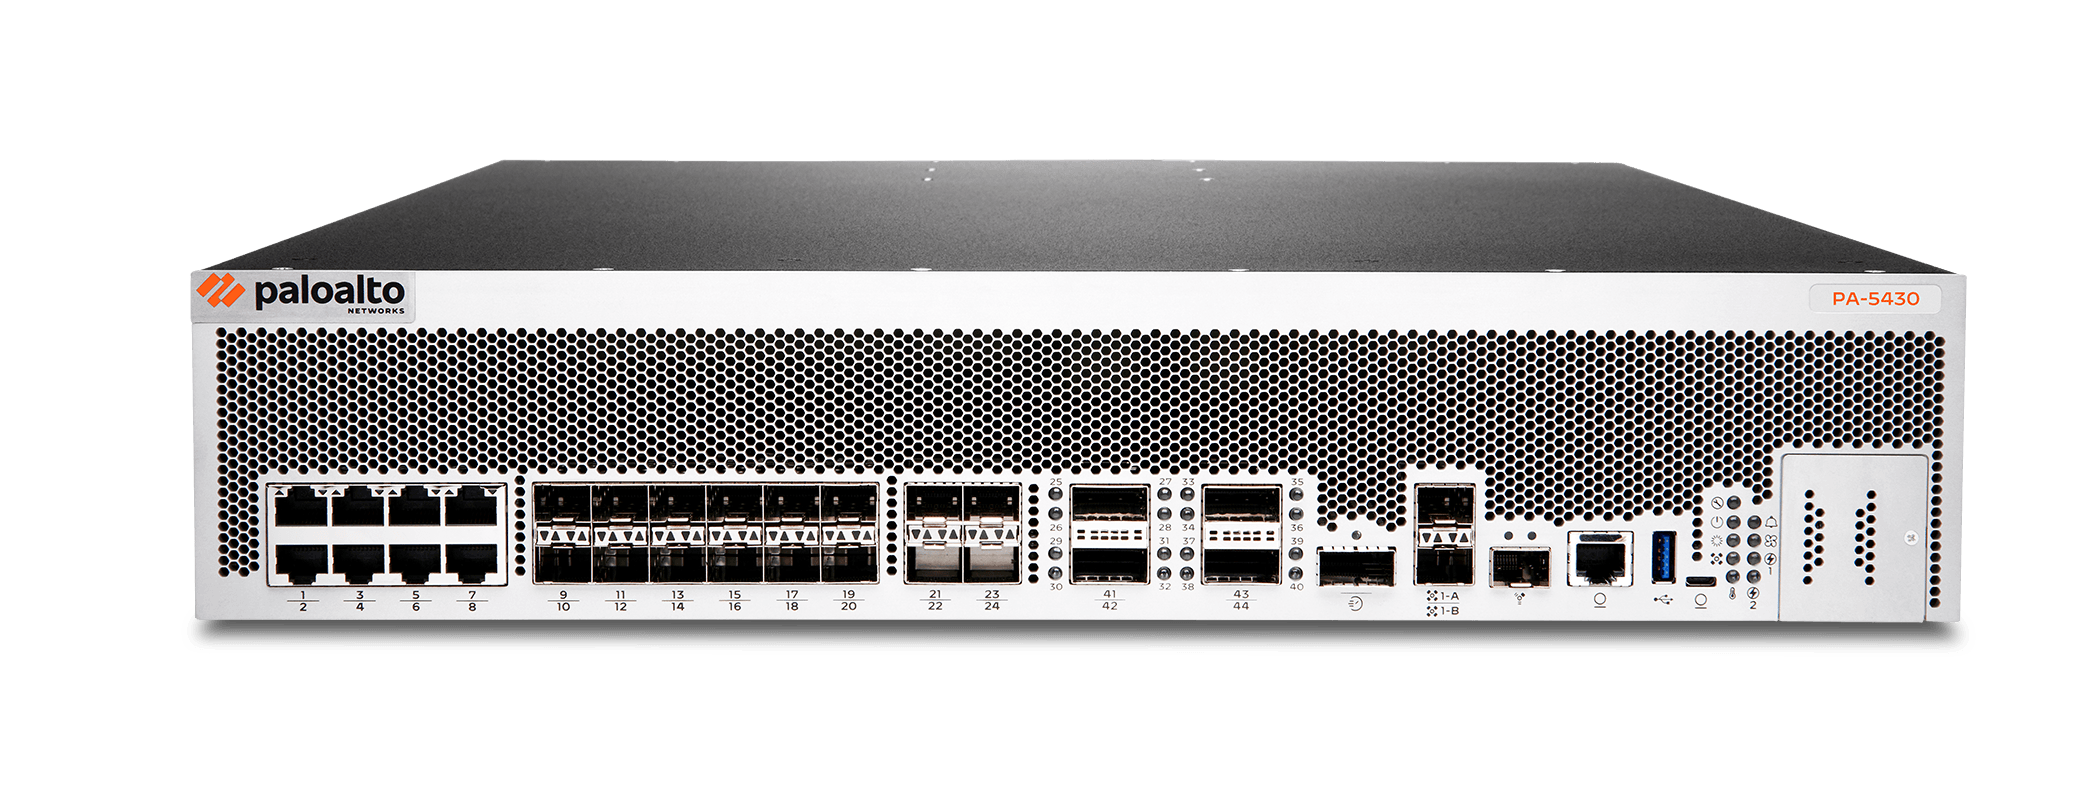
PA-5430: Fixed 2U form factor with up to 9 million sessions and 25 virtual systems in the base configuration.
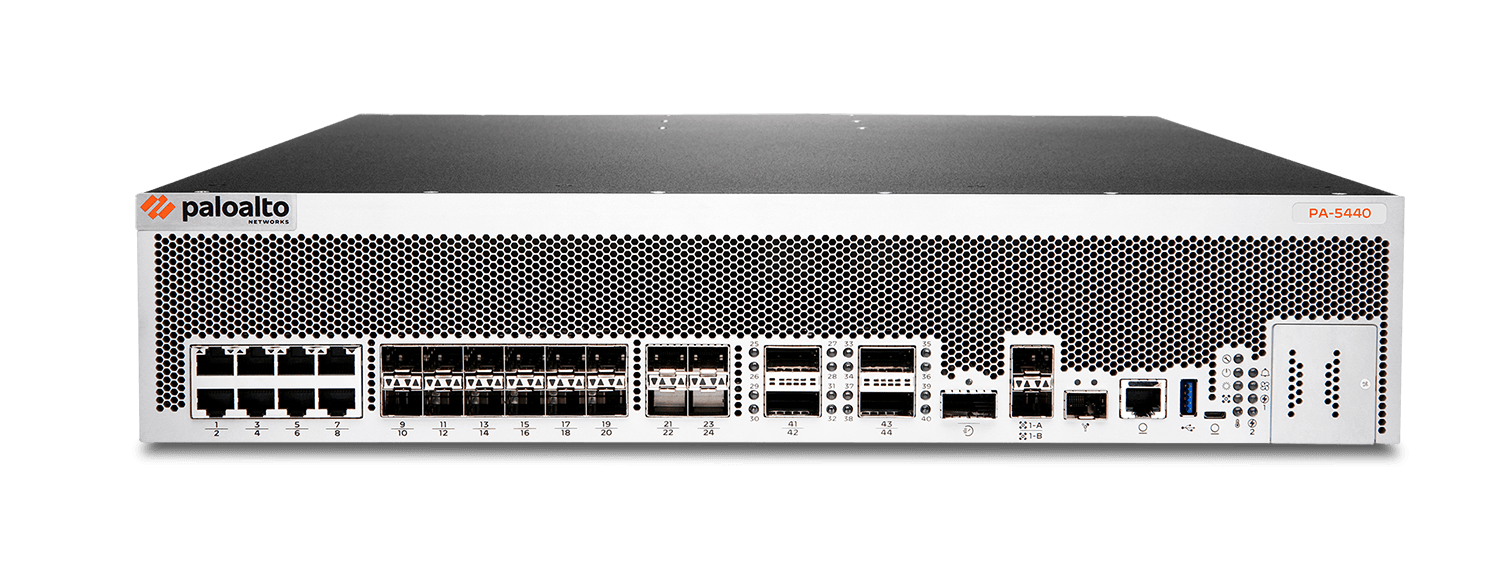
PA-5440: Fixed 2U form factor with up to 20 million sessions and 25 virtual systems in the base configuration.
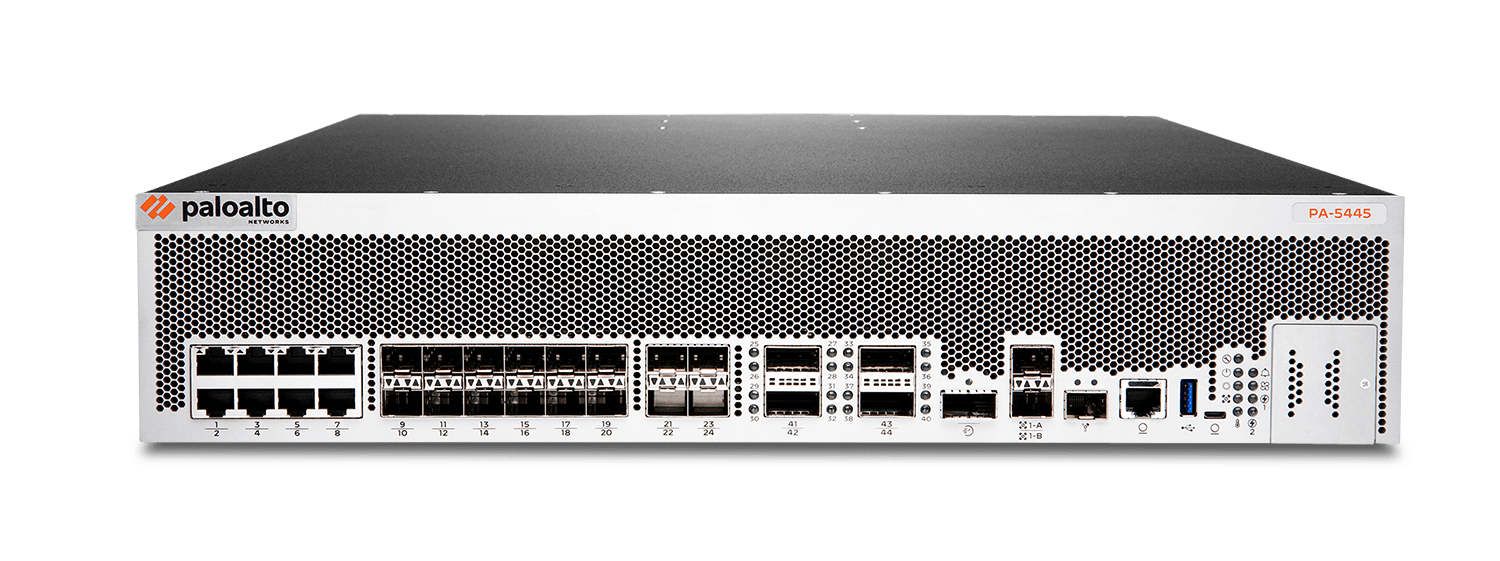
PA-5445: Fixed 2U form factor with up to 48 million sessions and 25 virtual systems in the base configuration.
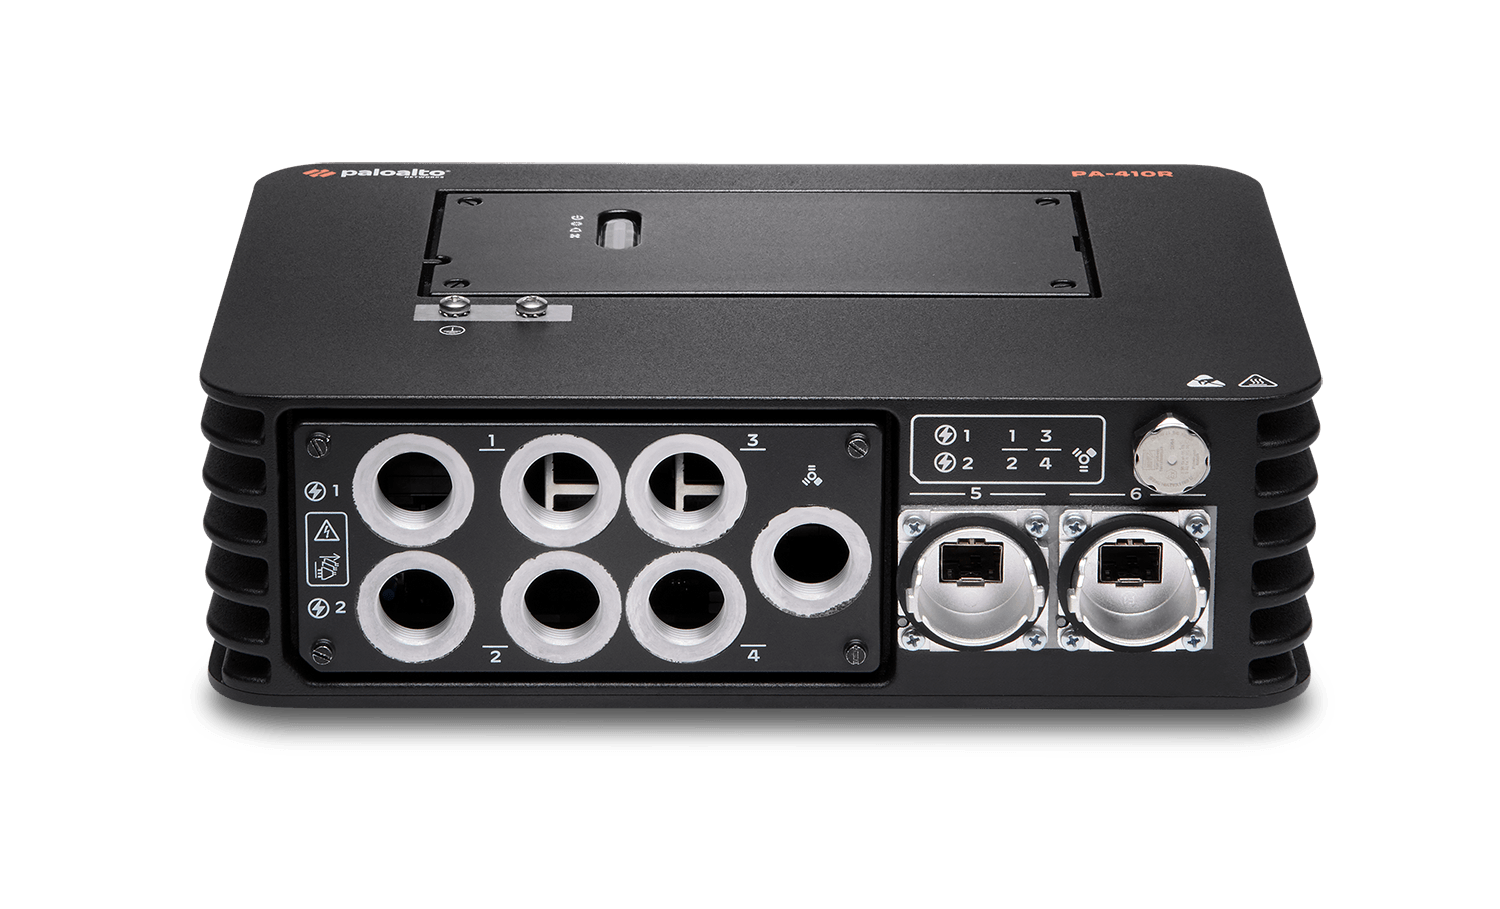
PA-410R: Industrial installations with DC power and wired connectivity.
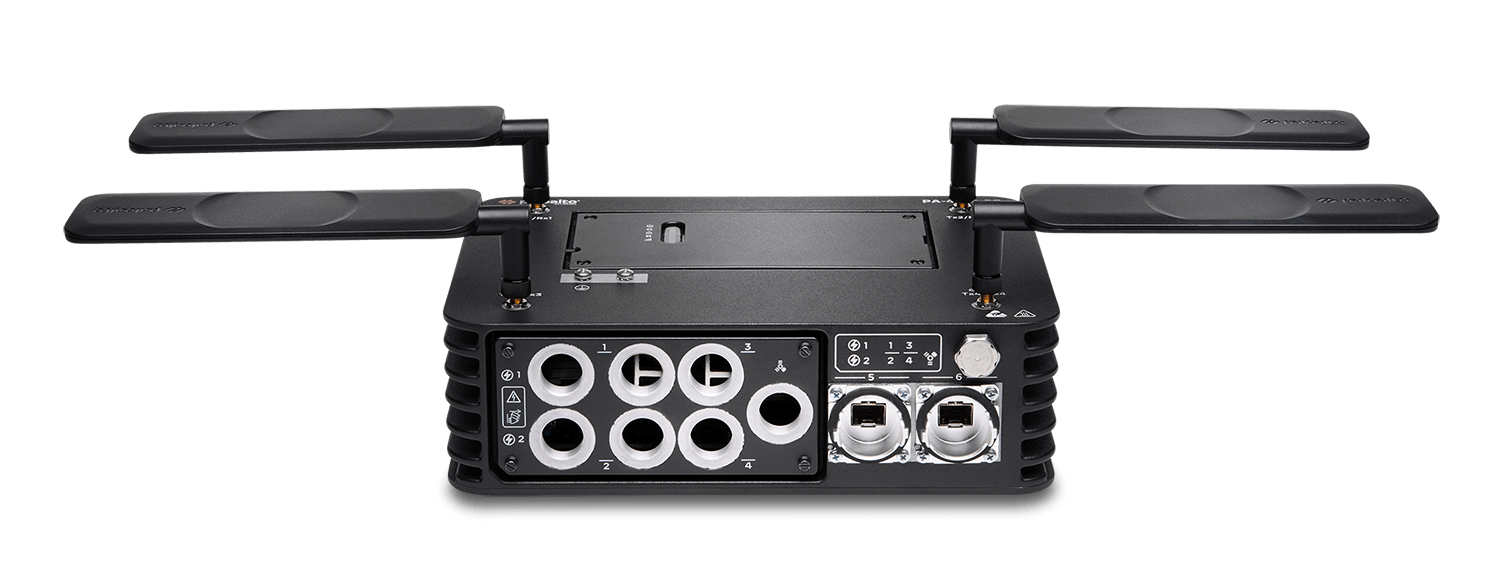
PA-410R-5G: Industrial variant with 5G and IP 65 protection for field connectivity.
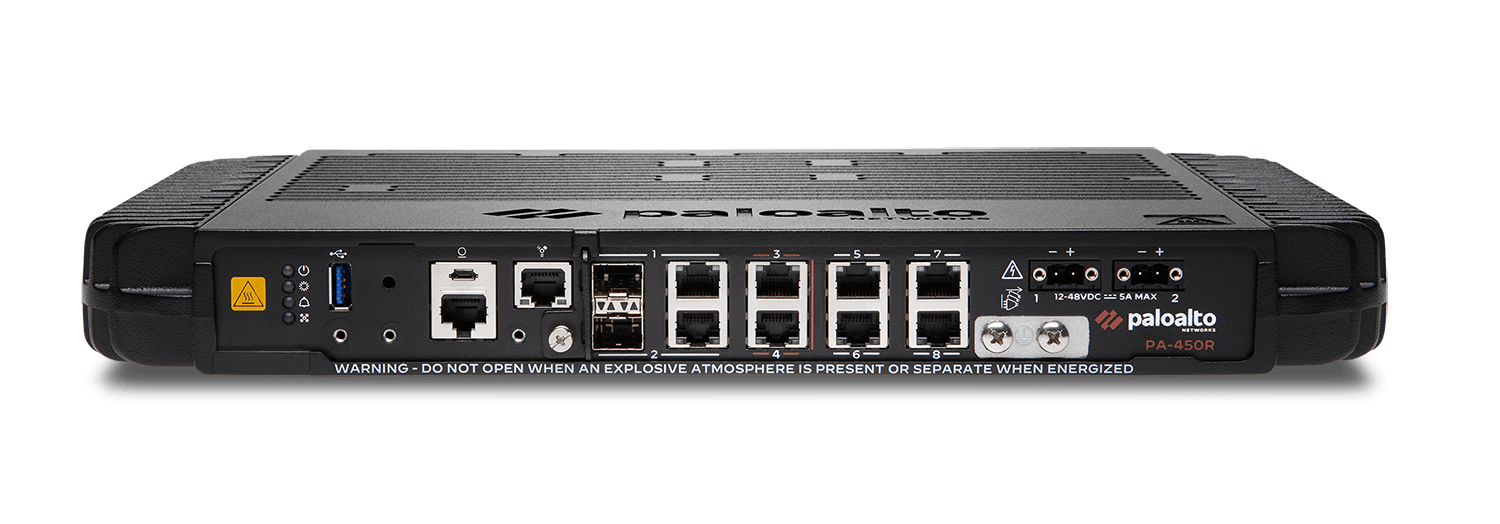
PA-450R: Wired industrial networks with more ports and DC power.
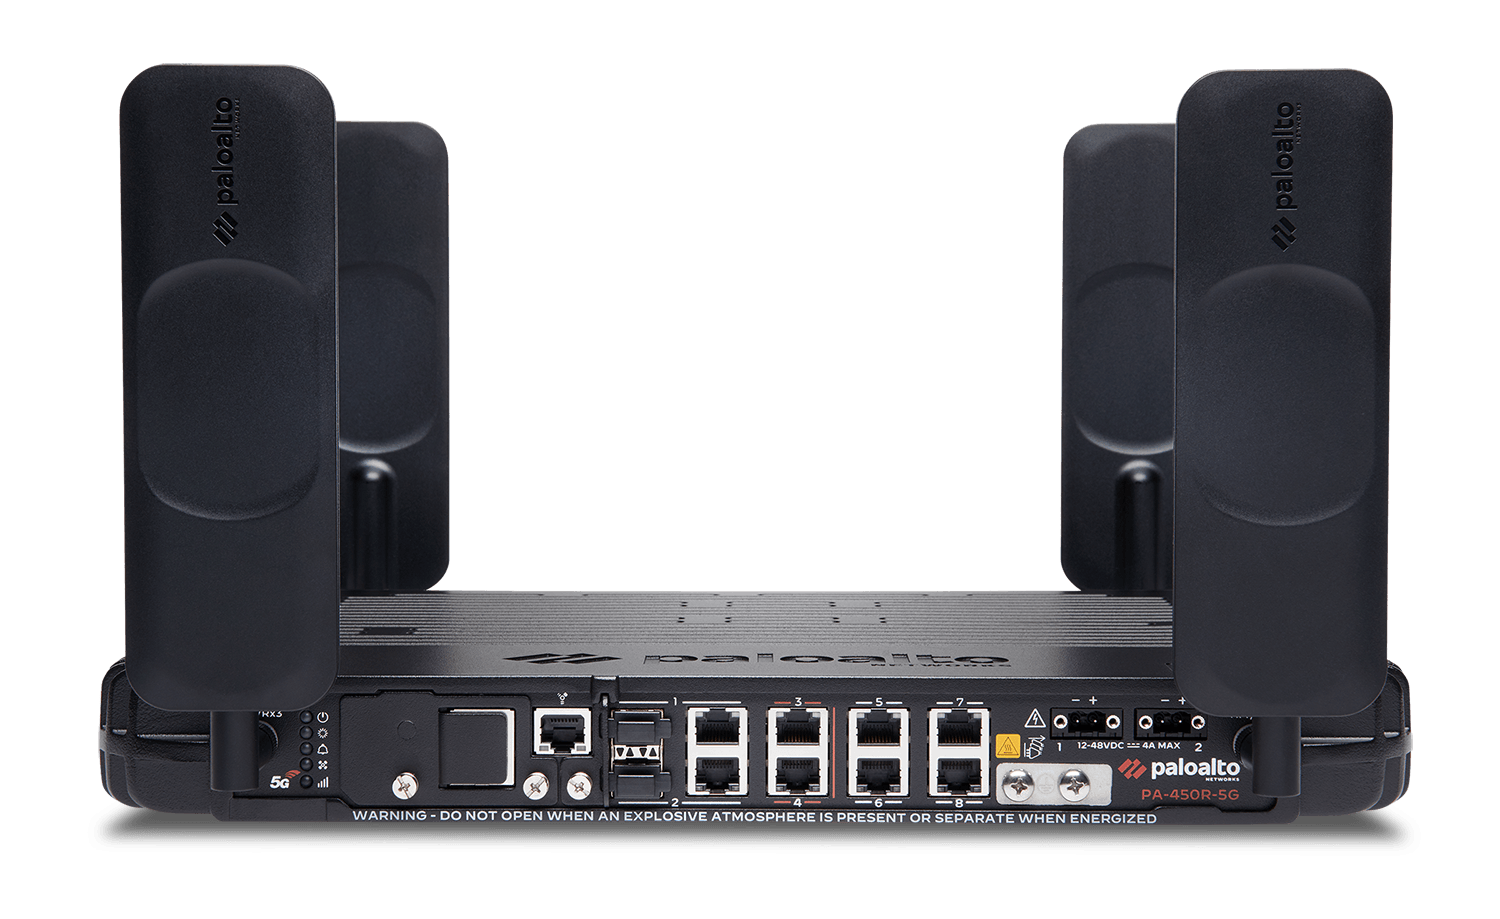
PA-450R-5G: 5G variant for installations where IP 40 protection is suitable.
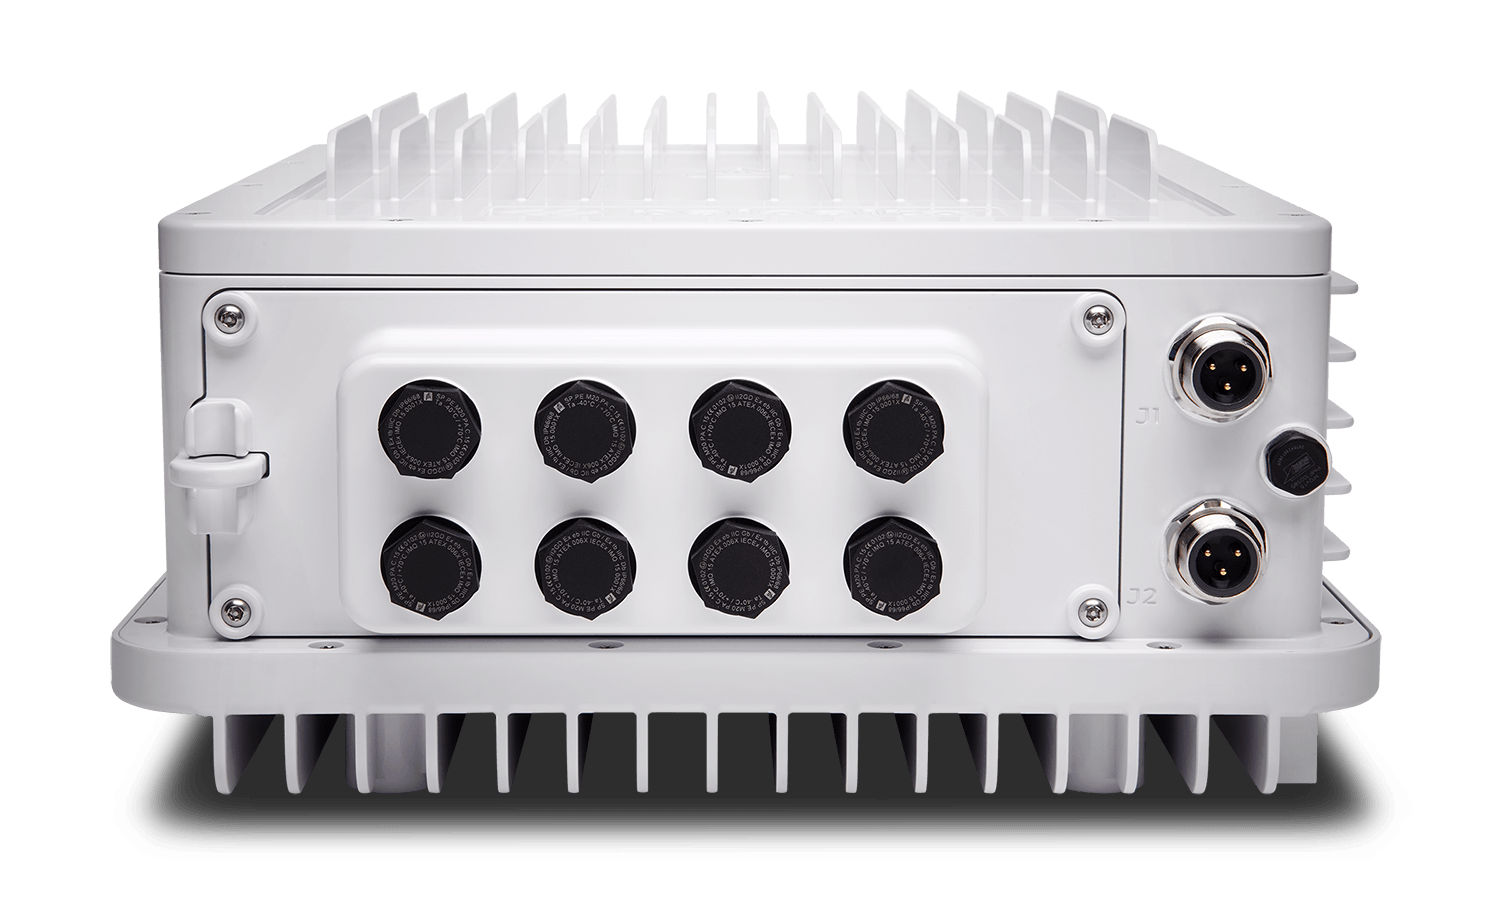
PA-455R-5G: Combines 5G, PoE and AC power for industrial environments with IP 65 protection.
Uma especificação isolada não dimensiona um projeto. Topologia, tráfego real, inspeção criptografada, serviços, VPN, redundância e expansão precisam ser avaliados em conjunto.