Understanding the environment
Critical applications, links, sites, remote access and existing policies form the basis of the choice.
Firewalls, connectivity and security management for branches, enterprise environments and hybrid infrastructure. Add Solution supports selection, configuration and deployment according to operational needs.
Features and integrations vary by product, version, subscription and configuration. Sizing considers the actual environment and enabled controls.
Use the filters to browse by category, family and size. The final selection considers enabled inspection, interfaces, availability and required security services.
The technical discussion starts with applications, links, networks and access that must remain restricted. These requirements guide the family, capacity and deployment plan.
Critical applications, links, sites, remote access and existing policies form the basis of the choice.
Family, model, licensing, interfaces and expected growth are part of the technical assessment.
Execution is planned with the team responsible for the network and depends on access and connectivity conditions.
Responsibilities, hours and service terms are defined in a proposal for each project.
Internet access, site-to-site communication, internal applications and cloud resources require clear policies and adequate capacity to apply the defined controls.
Physical and virtual firewalls, threat prevention and management form the core; switches, Wi-Fi and secure access complement the architecture according to the scenario.
The choice combines model, security services, licensing and operating model — not just maximum firewall throughput.
The project organizes requirements, selection, licensing, configuration, deployment and support within a clear scope.
Expansion, refresh, segmentation or control-review projects require planning around the current configuration and the effects of change on services in use.
Network Security Manager centralizes SonicWall firewall management. SaaS or on-premises options, retention, reporting and other functions vary by version and license.
Configuration, orchestration, analytics and reporting for firewalls, according to the purchased edition.
Access point and switch management and SonicWall Unified Management have their own roles; the architecture defines consoles and integrations.
Subscriptions complement the firewall according to the package. Capture ATP analyzes files in a sandbox and uses RTDMI; availability depends on licensing and compatibility.
Access design considers identity, device, application and policy, as well as licensing and connector architecture.
SSE platform with Secure Private Access for private applications and Secure Internet Access for browsing; features vary by edition and license.
Dedicated 6210 and 7210 gateways and the virtual 8200v option. The choice considers concurrent users, authentication, posture, availability and updates.
TZ is a starting point for smaller sites; NSa serves enterprise networks with greater demands; NSsp serves large environments and data centers; NSv serves virtual infrastructure and compatible clouds. The choice depends on traffic, inspection and architecture.
It is only one data point. Applications, concurrency, encrypted traffic, sessions, VPNs and active services also influence capacity.
Not necessarily. Subscriptions, management, support and additional features must be itemized in the proposed composition.
The assessment considers model, software, service validity and lifecycle to discuss upgrades, renewal or replacement.
Add Solution offers remote installation and preconfiguration for SonicWall firewalls, according to connectivity and access conditions.
Yes. The composition checks ports, PoE, coverage, management, compatibility and availability for the project.
Compartilhe o contexto da operação, quantidade de usuários, localidades e objetivos do projeto. A equipe Add Solution direcionará a conversa para especialistas em arquitetura, dimensionamento, licenciamento e implantação SonicWall.
Tell us which sites, applications and access paths need protection. Add Solution helps assess the architecture and the mix of products and services.
Selecione um produto para consultar especificações, contexto de aplicação e documentos oficiais.
Valores publicados pelo fabricante. O dimensionamento final considera arquitetura, tráfego, serviços ativos, redundância e crescimento.
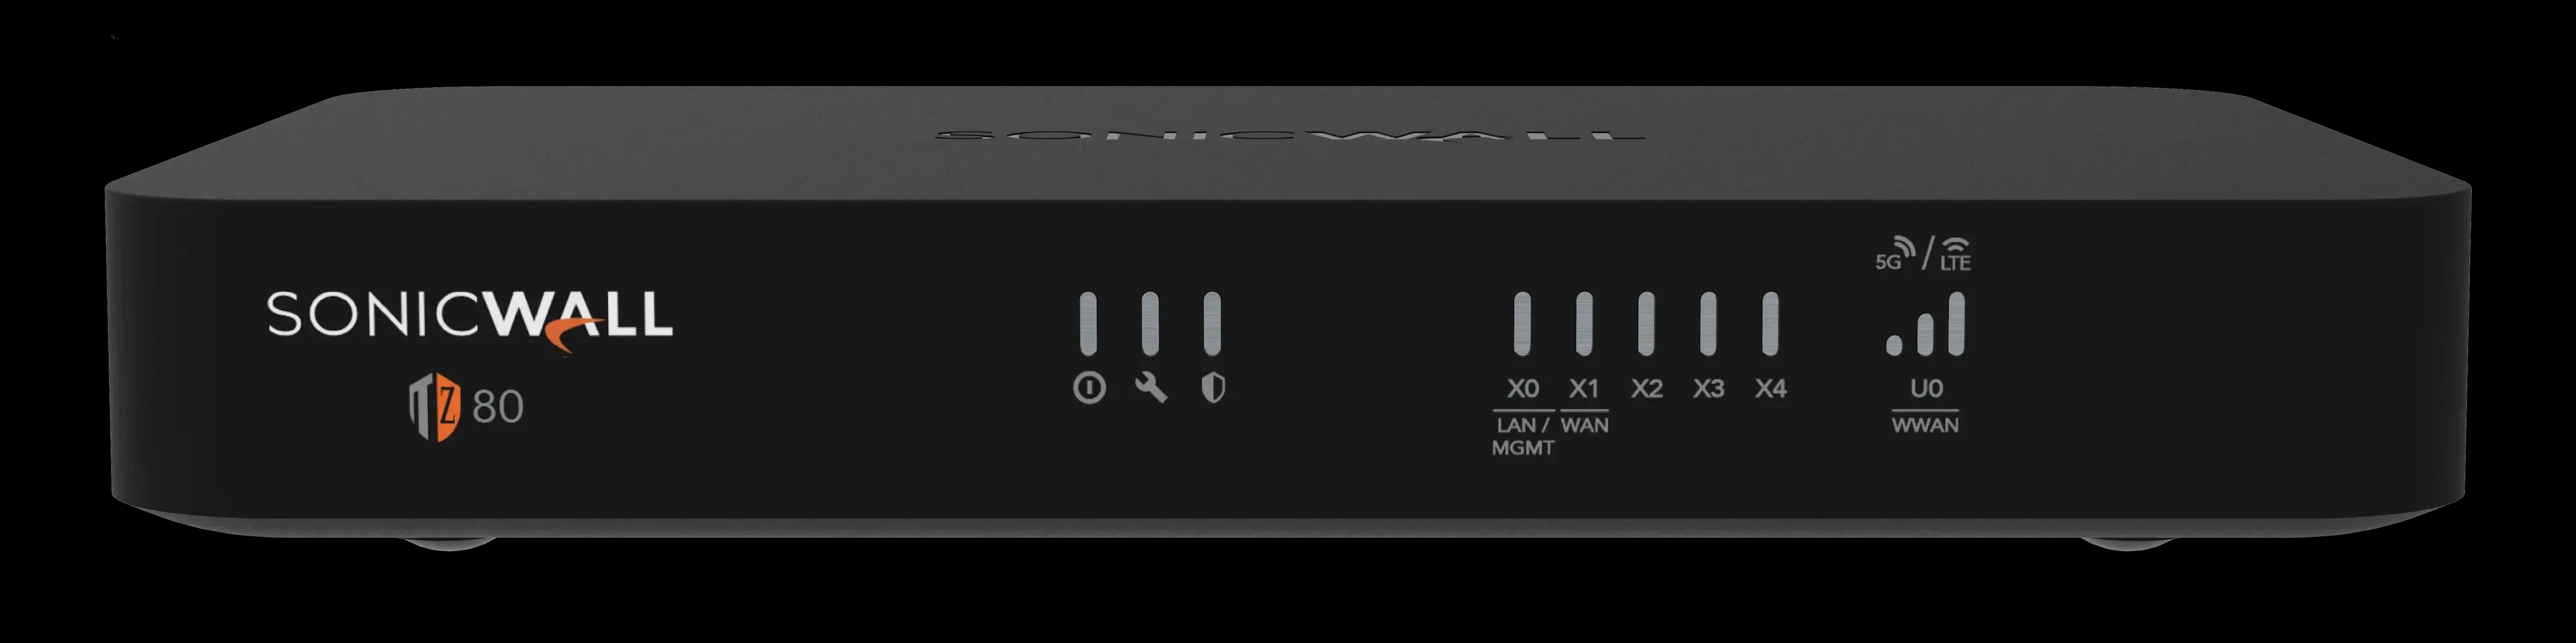
Compact subscription-based firewall for small offices, remote access and IoT, with four Gigabit ports and a 1 Gb/s SFP uplink.
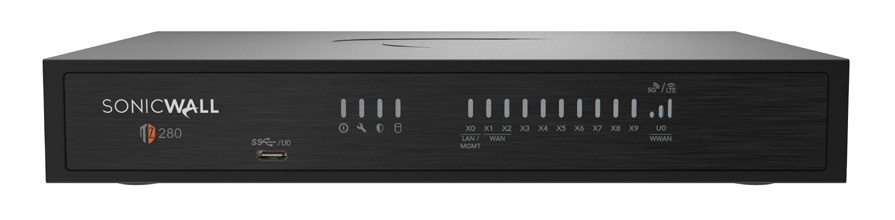
Desktop firewall for small offices and branches, with eight Gigabit connections and two 1 Gb/s optical uplinks.
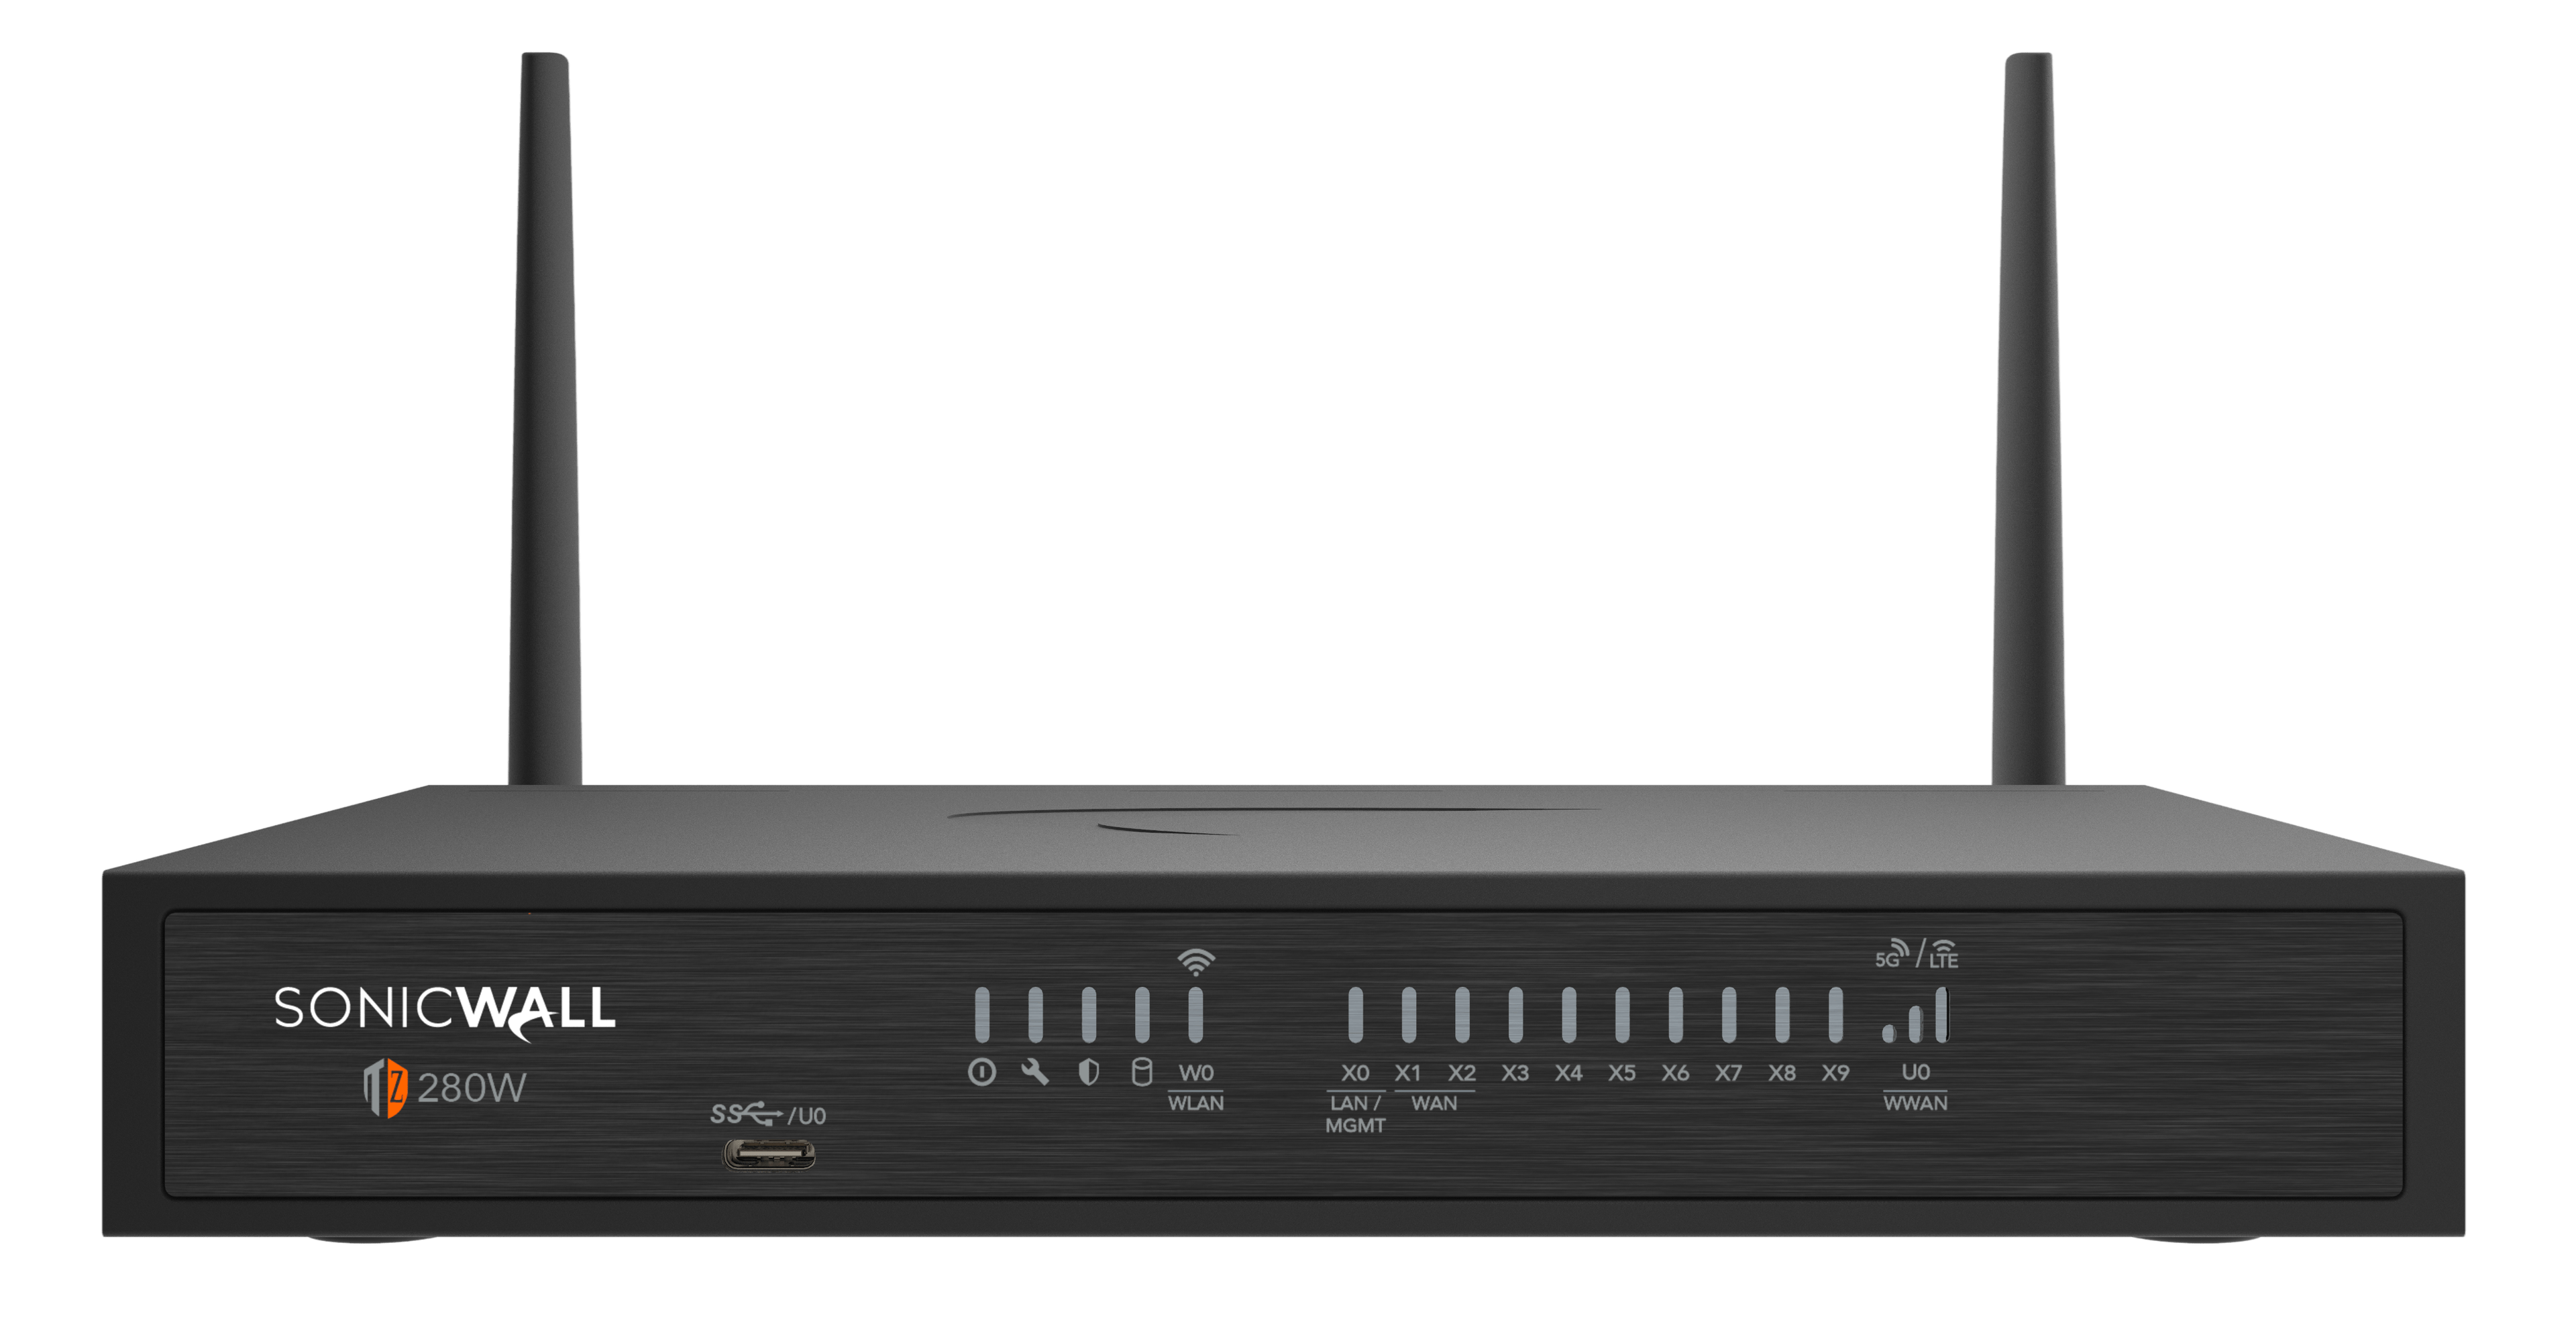
Desktop firewall with integrated Wi-Fi 6 2×2, eight Gigabit ports and two 1 Gb/s SFP uplinks for small offices.
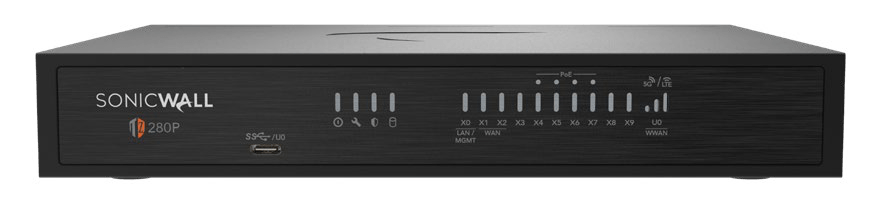
Desktop firewall with four PoE+ ports to power compatible devices, combining security and connectivity in small offices.
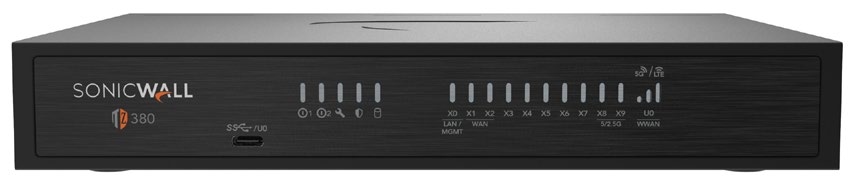
Desktop firewall for branches with multigigabit optical uplinks up to 5 Gb/s and an optional second power supply.
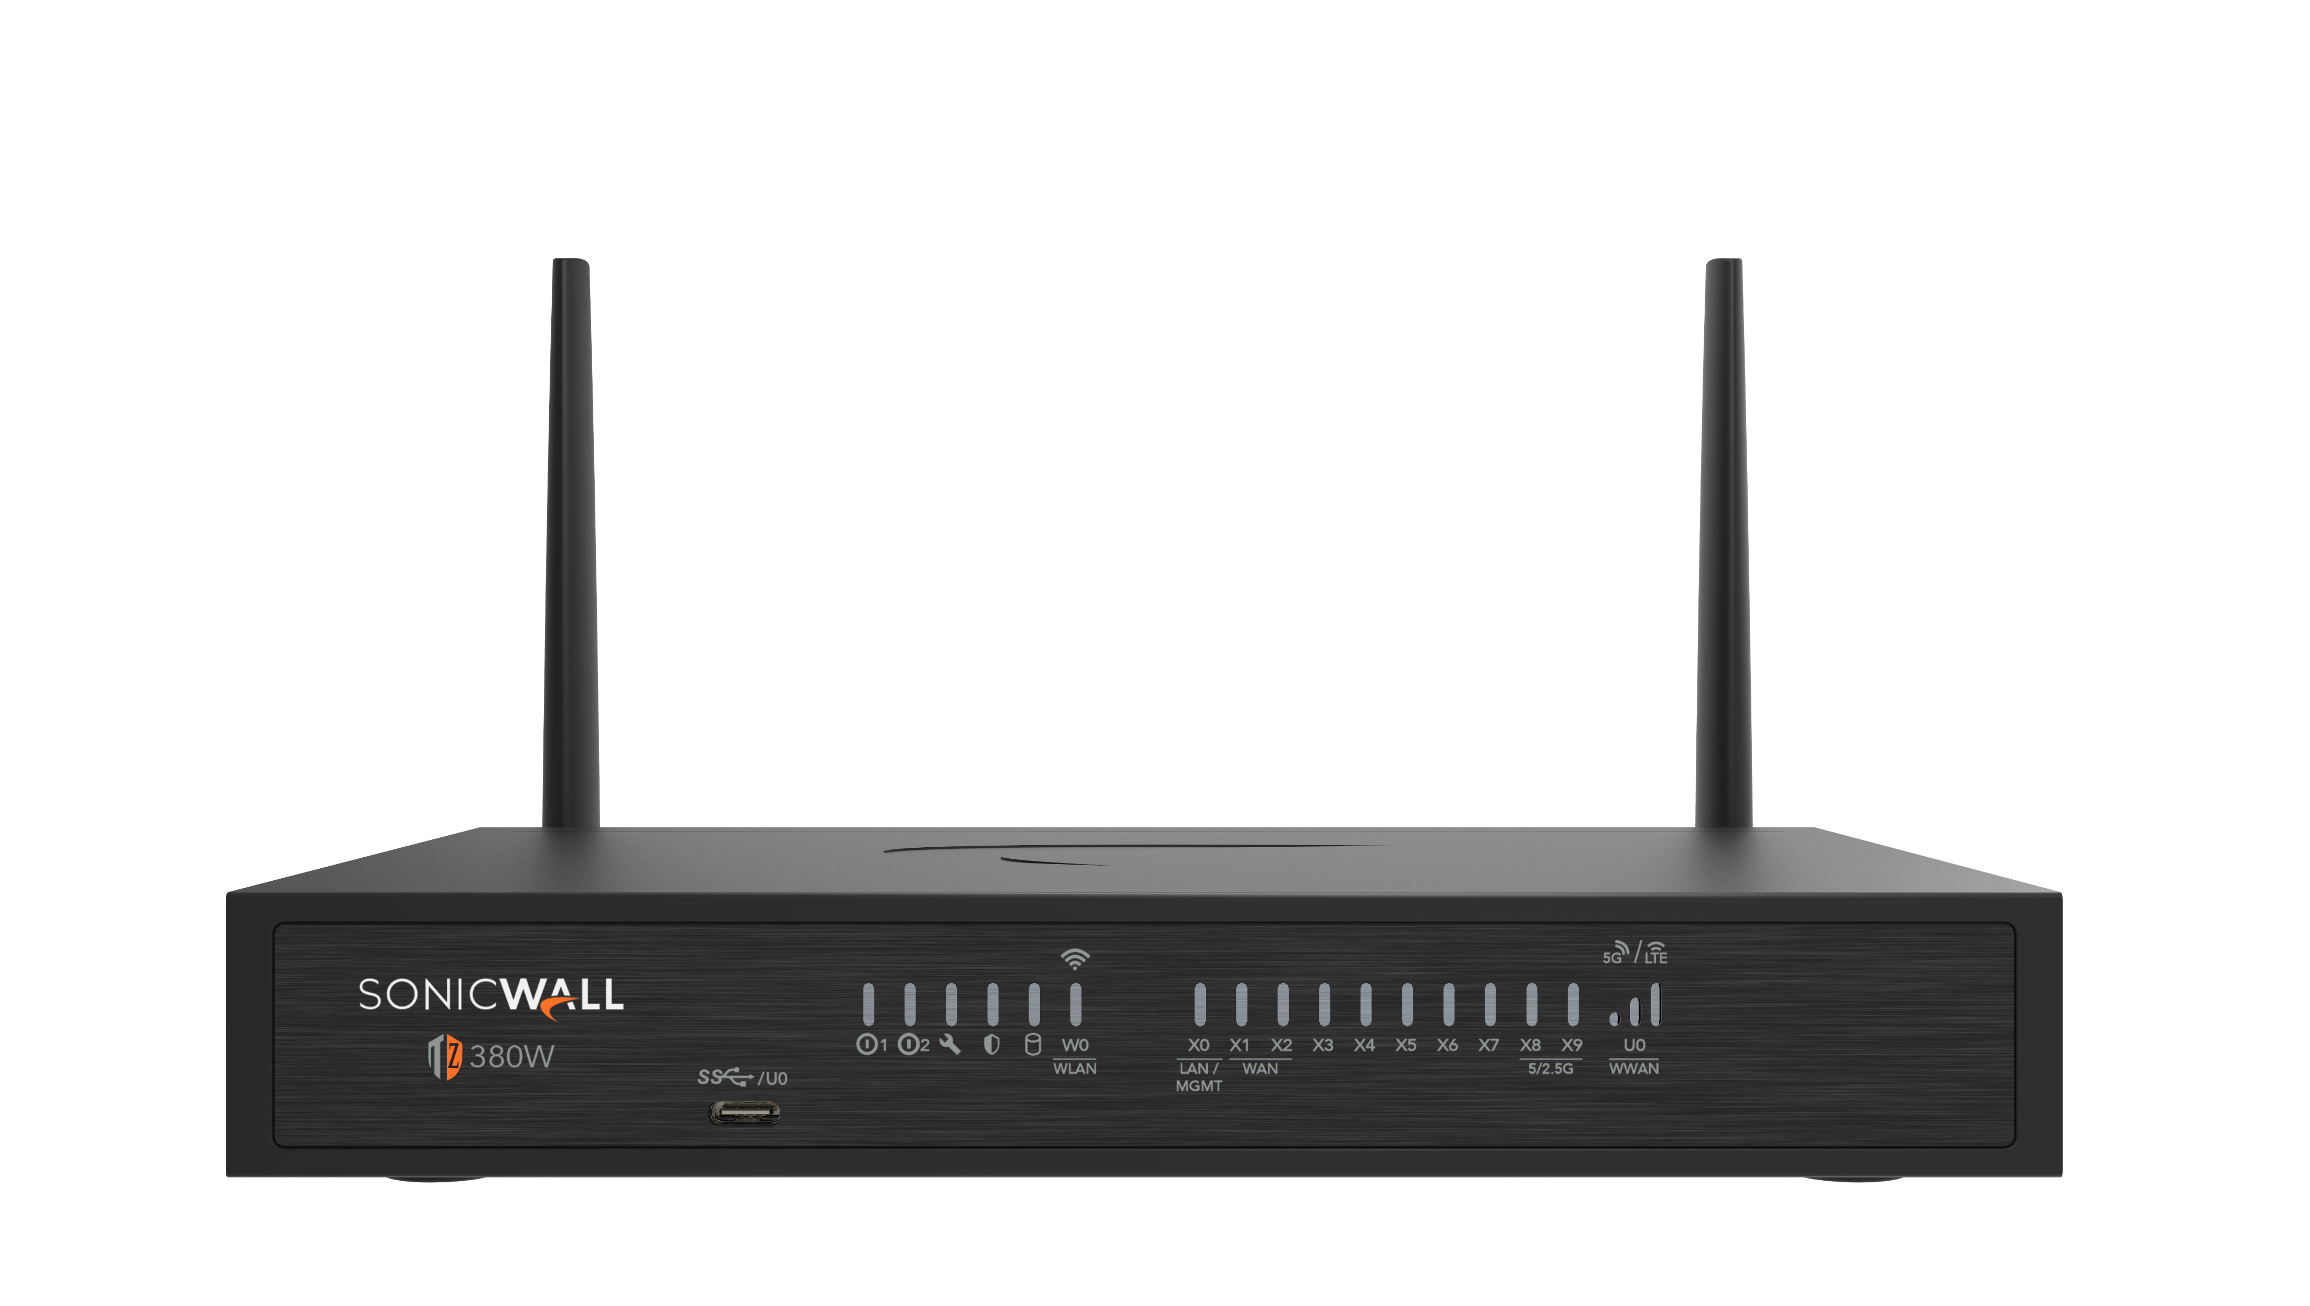
Firewall and Wi-Fi 6 2×2 in the same appliance for branches, with multigigabit optical uplinks and an optional second power supply.
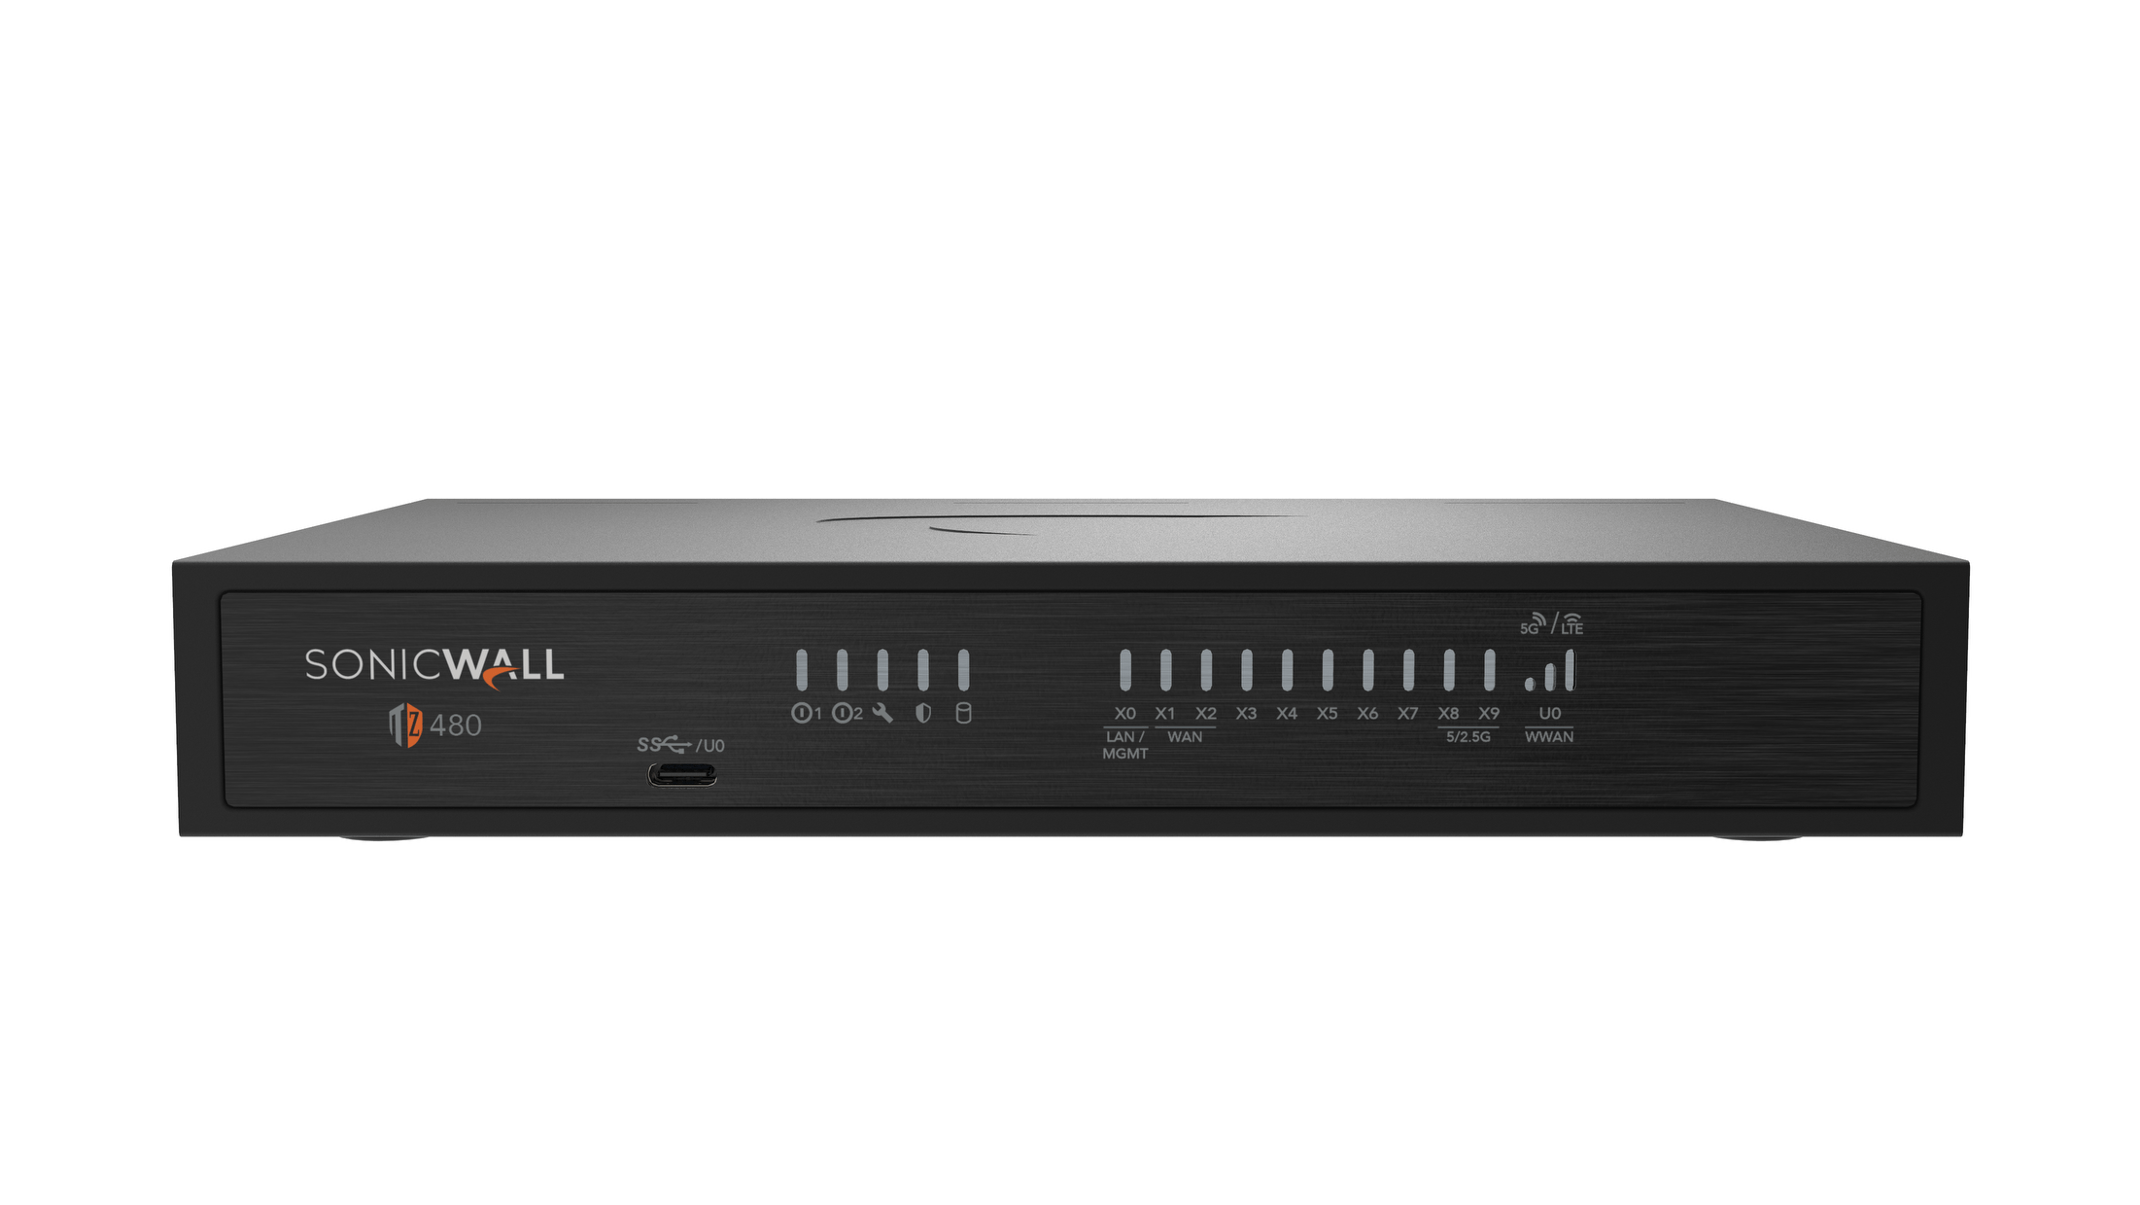
SD-Branch firewall with a maximum of 350 thousand DPI connections and SSL VPN expansion up to 150 licences.
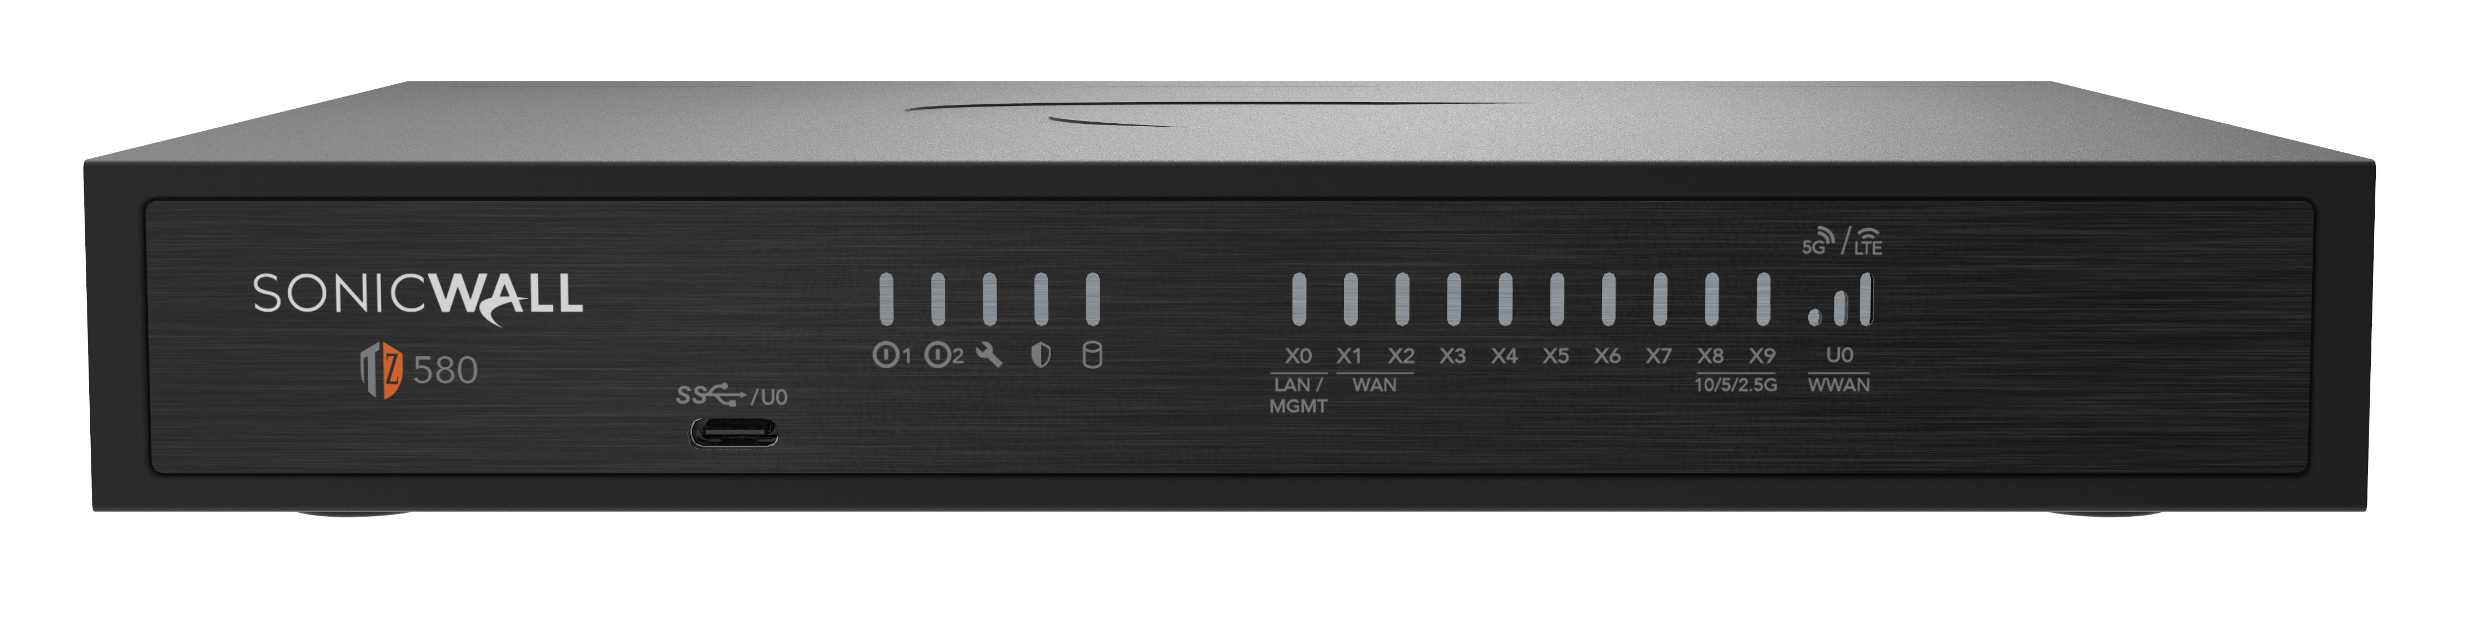
Compact firewall with uplinks up to 10 Gb/s, 256 logical interfaces and VPN expansion for growing branches.
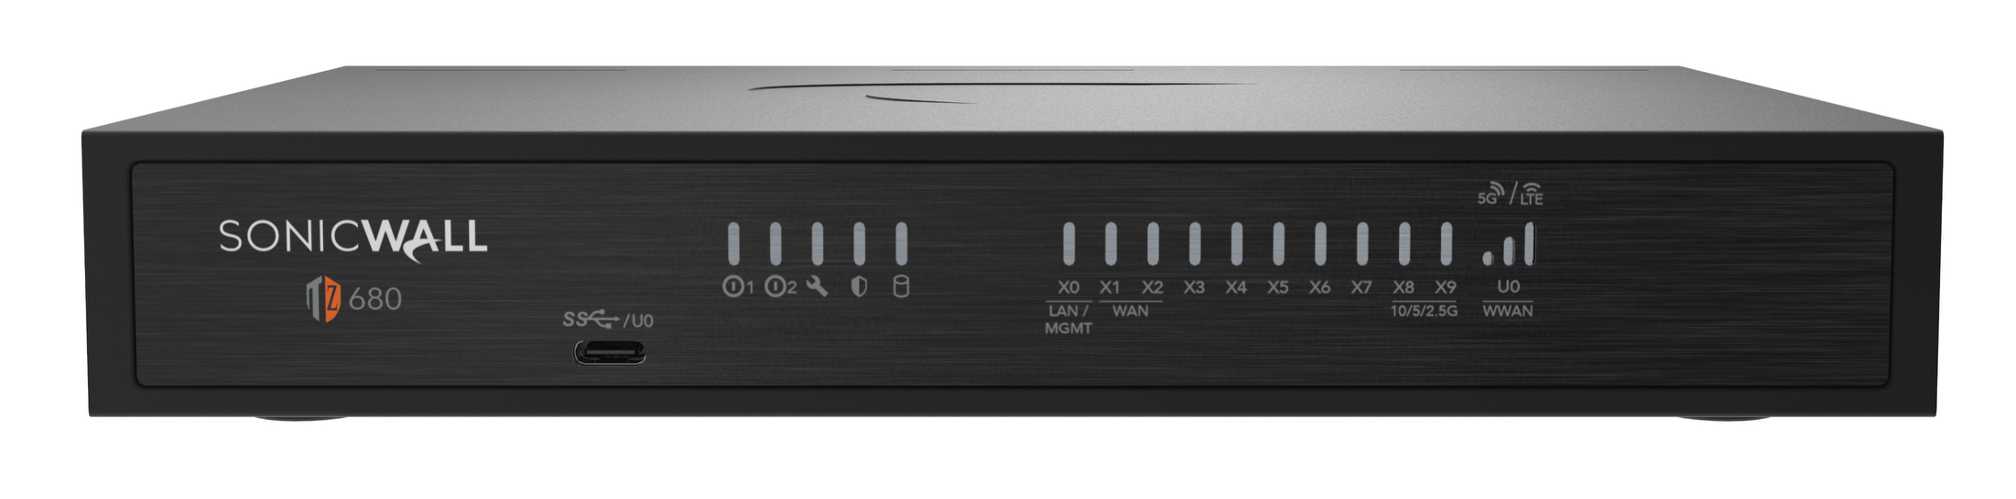
The highest-capacity model in the TZ Gen 8 series, with 10 Gb/s uplinks and up to 600 thousand DPI connections.
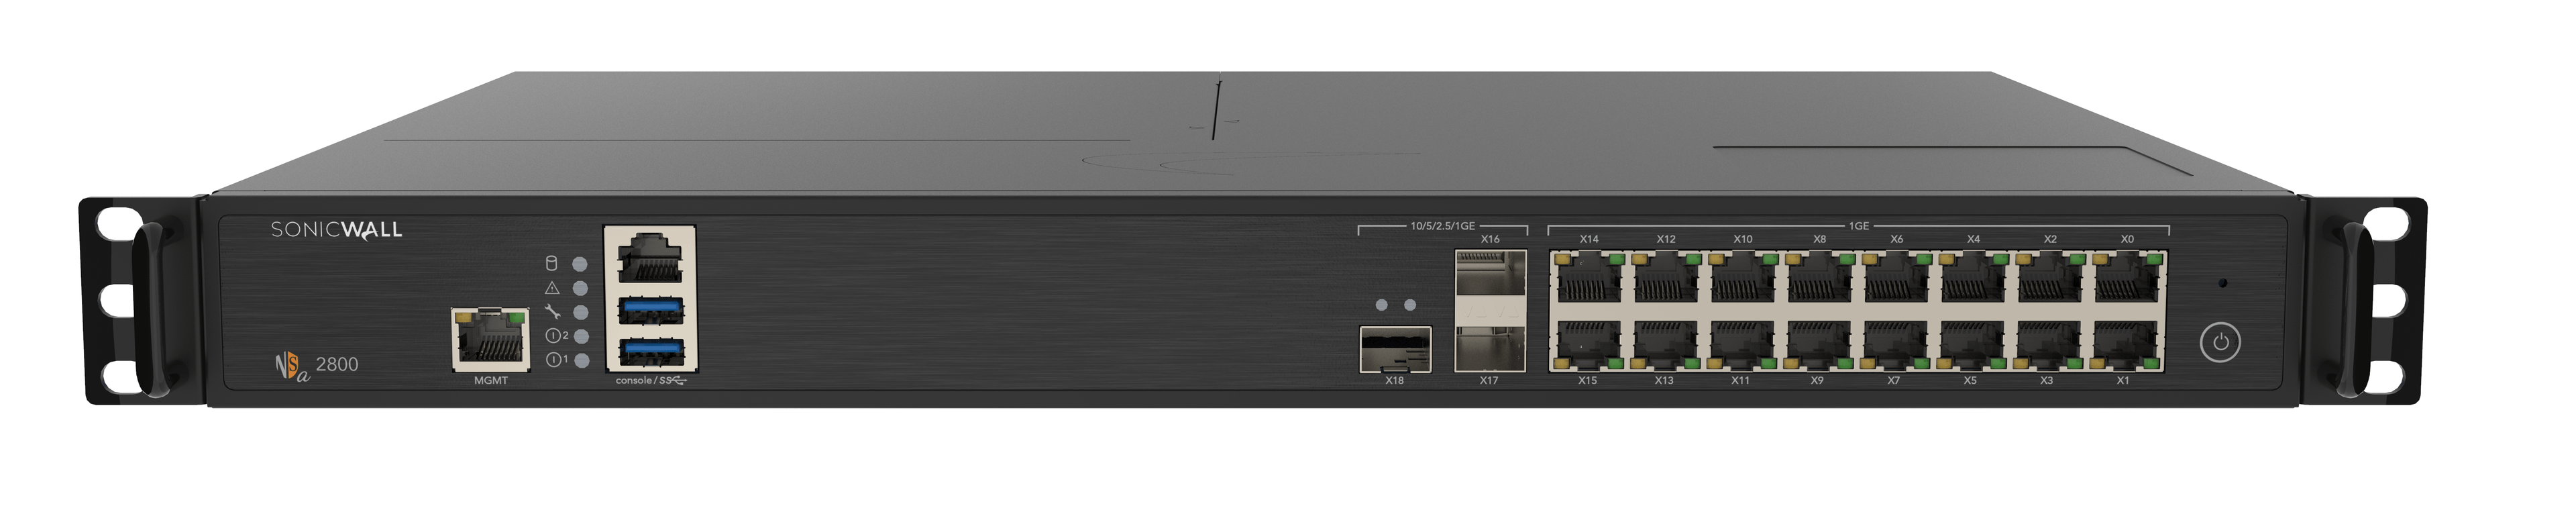
1U enterprise firewall with 16 Gigabit ports and three multigigabit optical interfaces for network segmentation and branch connectivity.
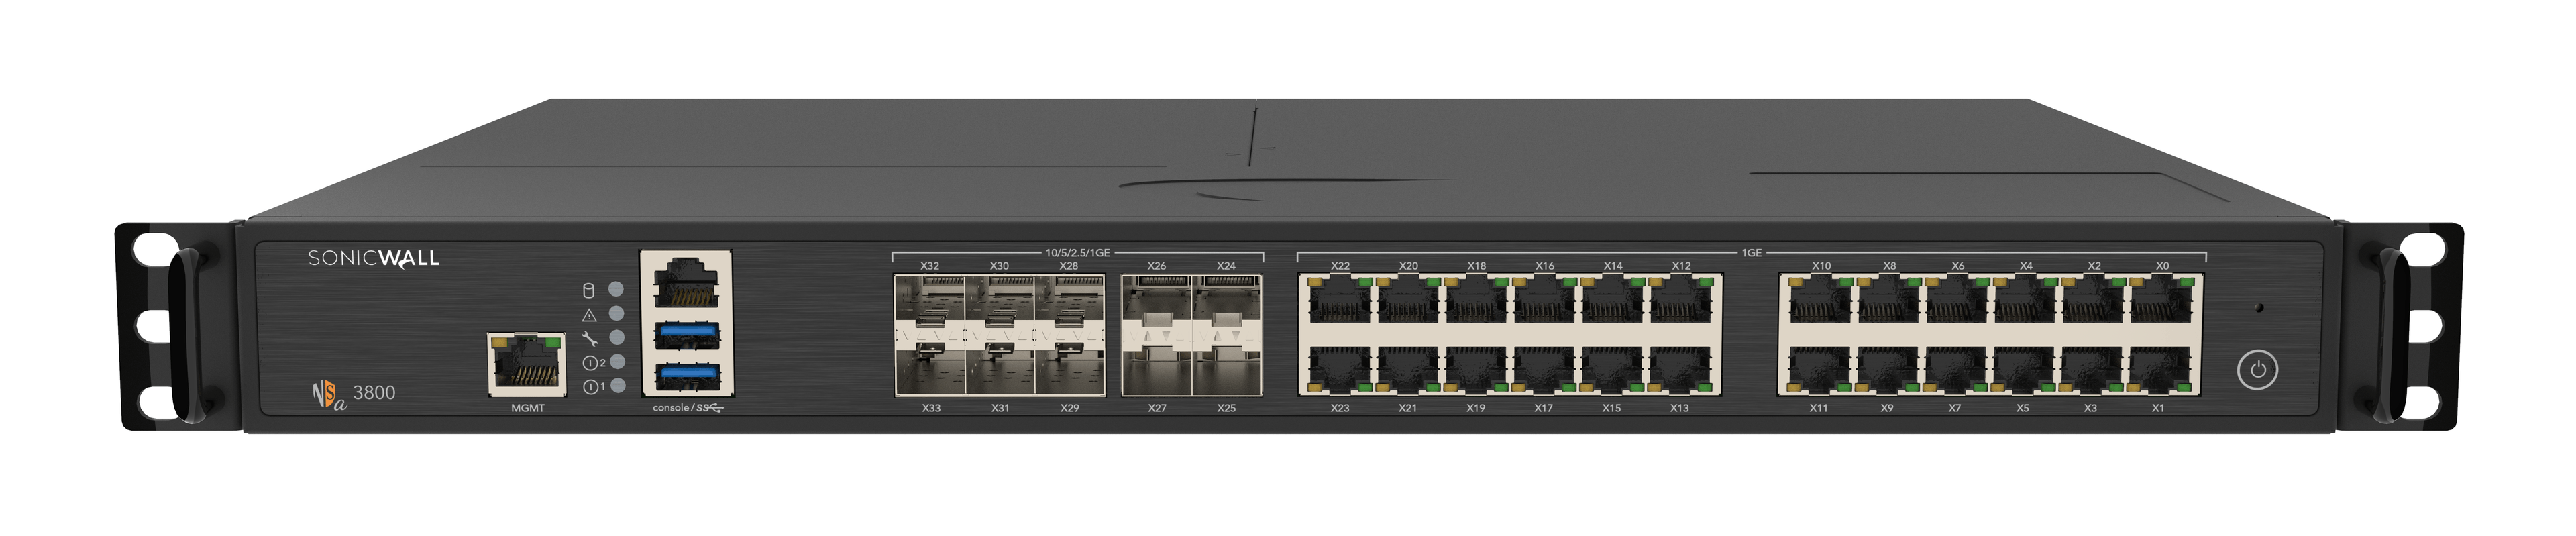
1U firewall combining 24 Gigabit ports with ten multigigabit SFP/SFP+ interfaces, useful for environments requiring many optical connections.
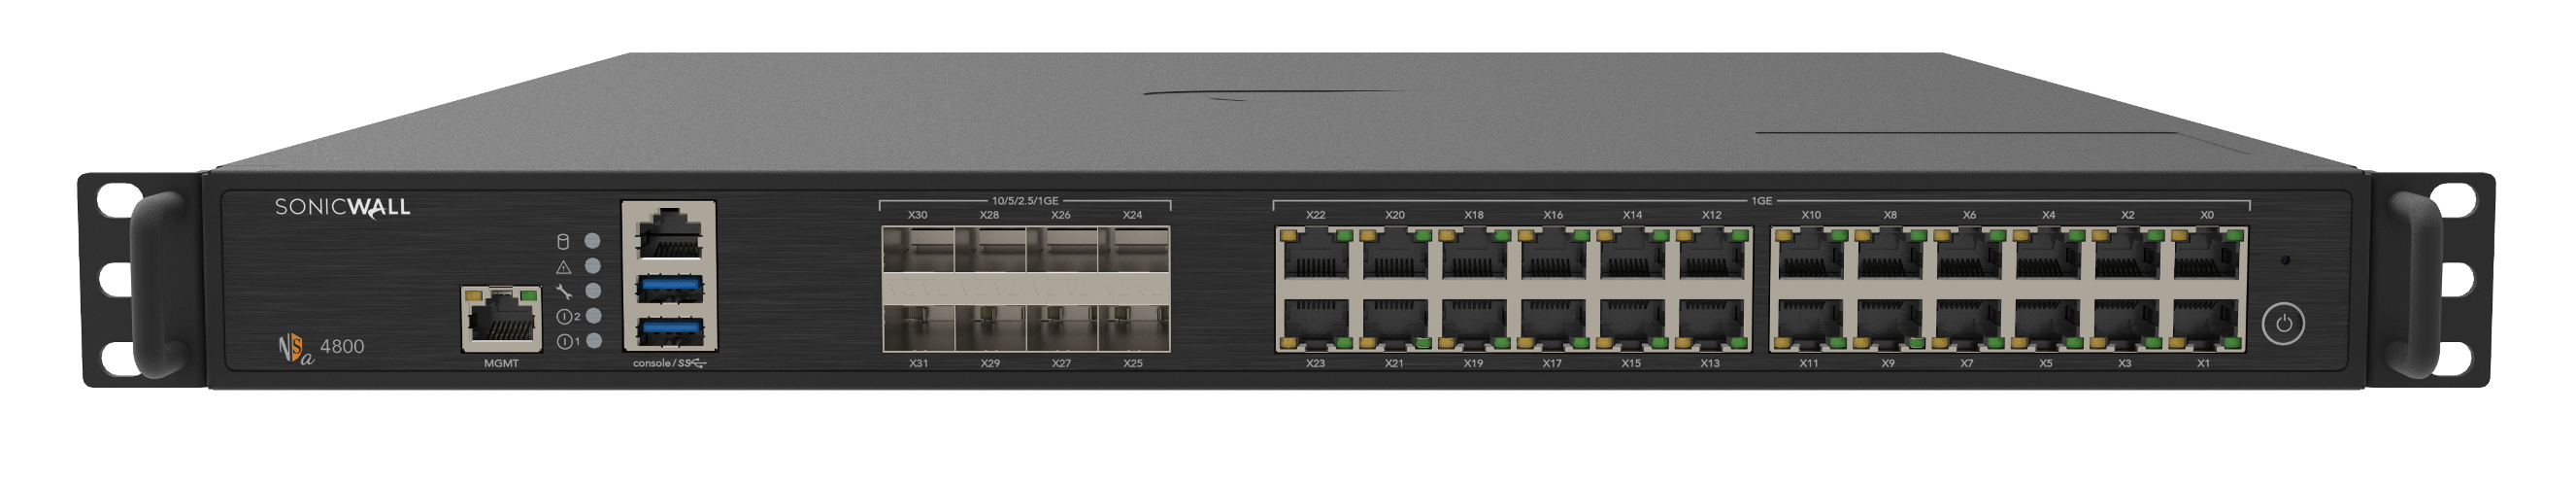
1U firewall with 24 Gigabit ports, eight SFP/SFP+ interfaces and storage expansion, for corporate networks with multiple segments.
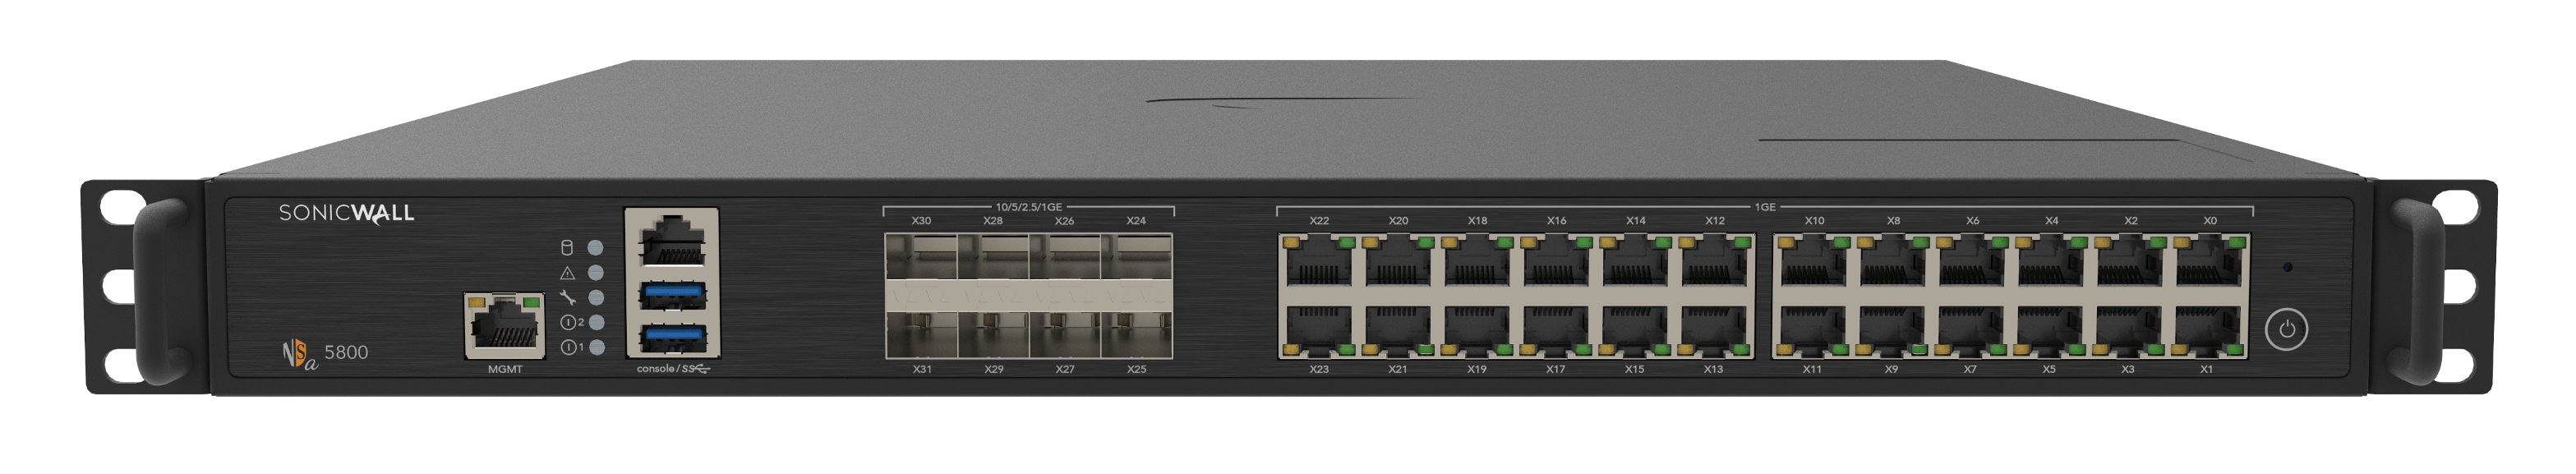
1U firewall for higher traffic concentration, with 24 Gigabit ports, eight SFP/SFP+ interfaces and higher session capacity within the series.
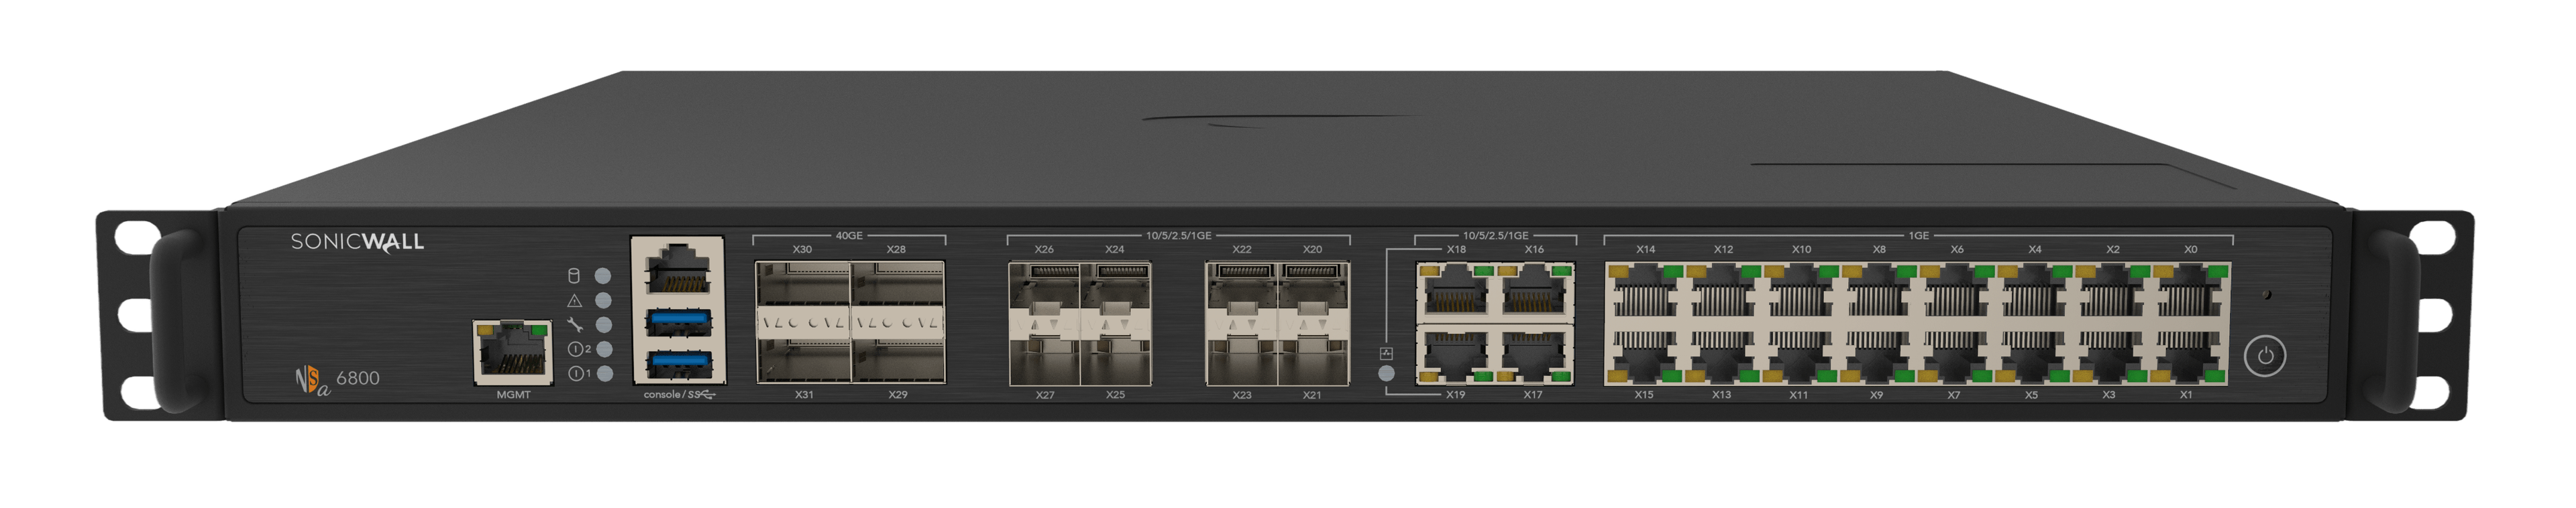
Gen 8 enterprise firewall in a 1U rack-mount form factor, with four 40G QSFP ports, eight multigigabit SFP/SFP+ interfaces and copper interfaces, for networks with high traffic concentration.
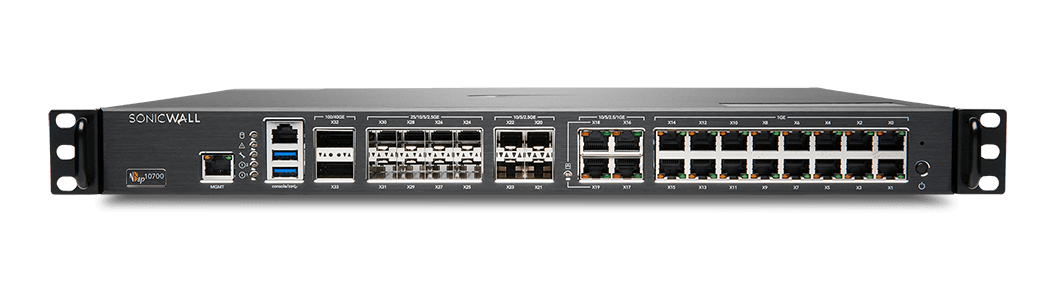
Gen 7 firewall in a 1U rack-mount form factor, with 100/40G and 25G ports to consolidate segments of large corporate networks.
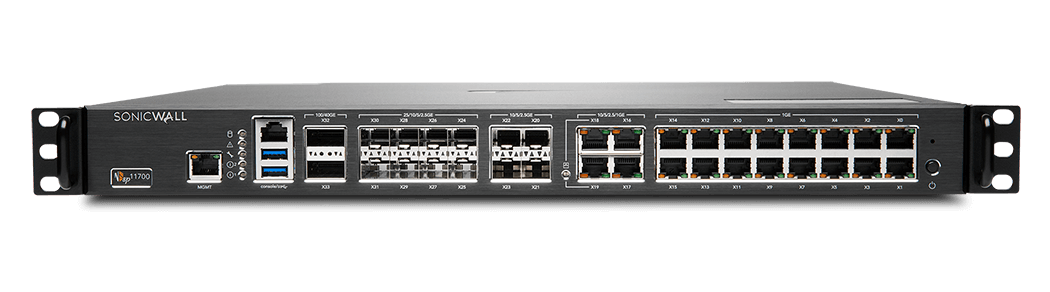
Gen 7 firewall in a 1U rack-mount form factor, with 100/40G, 25G and multigigabit connectivity to increase session and VPN capacity between sites.
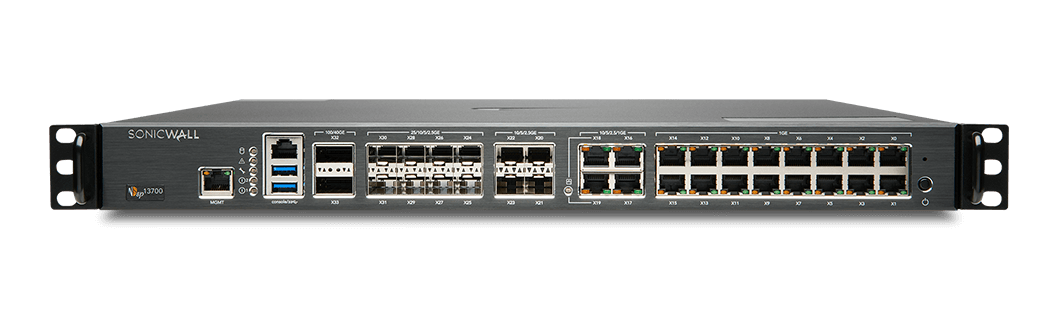
Gen 7 firewall in a 1U rack-mount form factor for large networks and data centres, with 100/40G and 25G interfaces and high connection capacity.
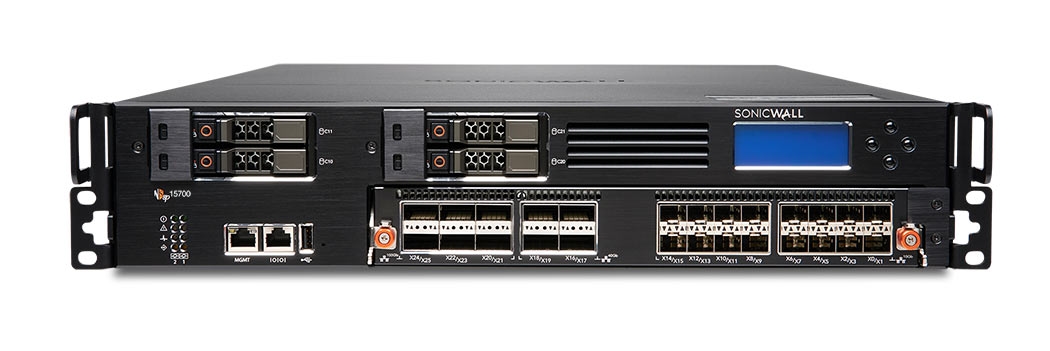
Gen 7 firewall in a 2U rack-mount form factor with six 100G ports and a multi-instance architecture for up to 12 tenants, intended for data centres and operations with isolated environments.
Single-core virtual firewall for small environments, branches and lightweight workloads; requires an active subscription and connectivity for licensing.
Two-core virtual firewall for branches and growing environments, running on compatible hypervisors and public clouds.
Four-core virtual firewall for segmentation and workload protection in hybrid environments with higher processing demands.
Eight-core virtual firewall for virtualised environments and distributed operations that require greater resource and interface scale.
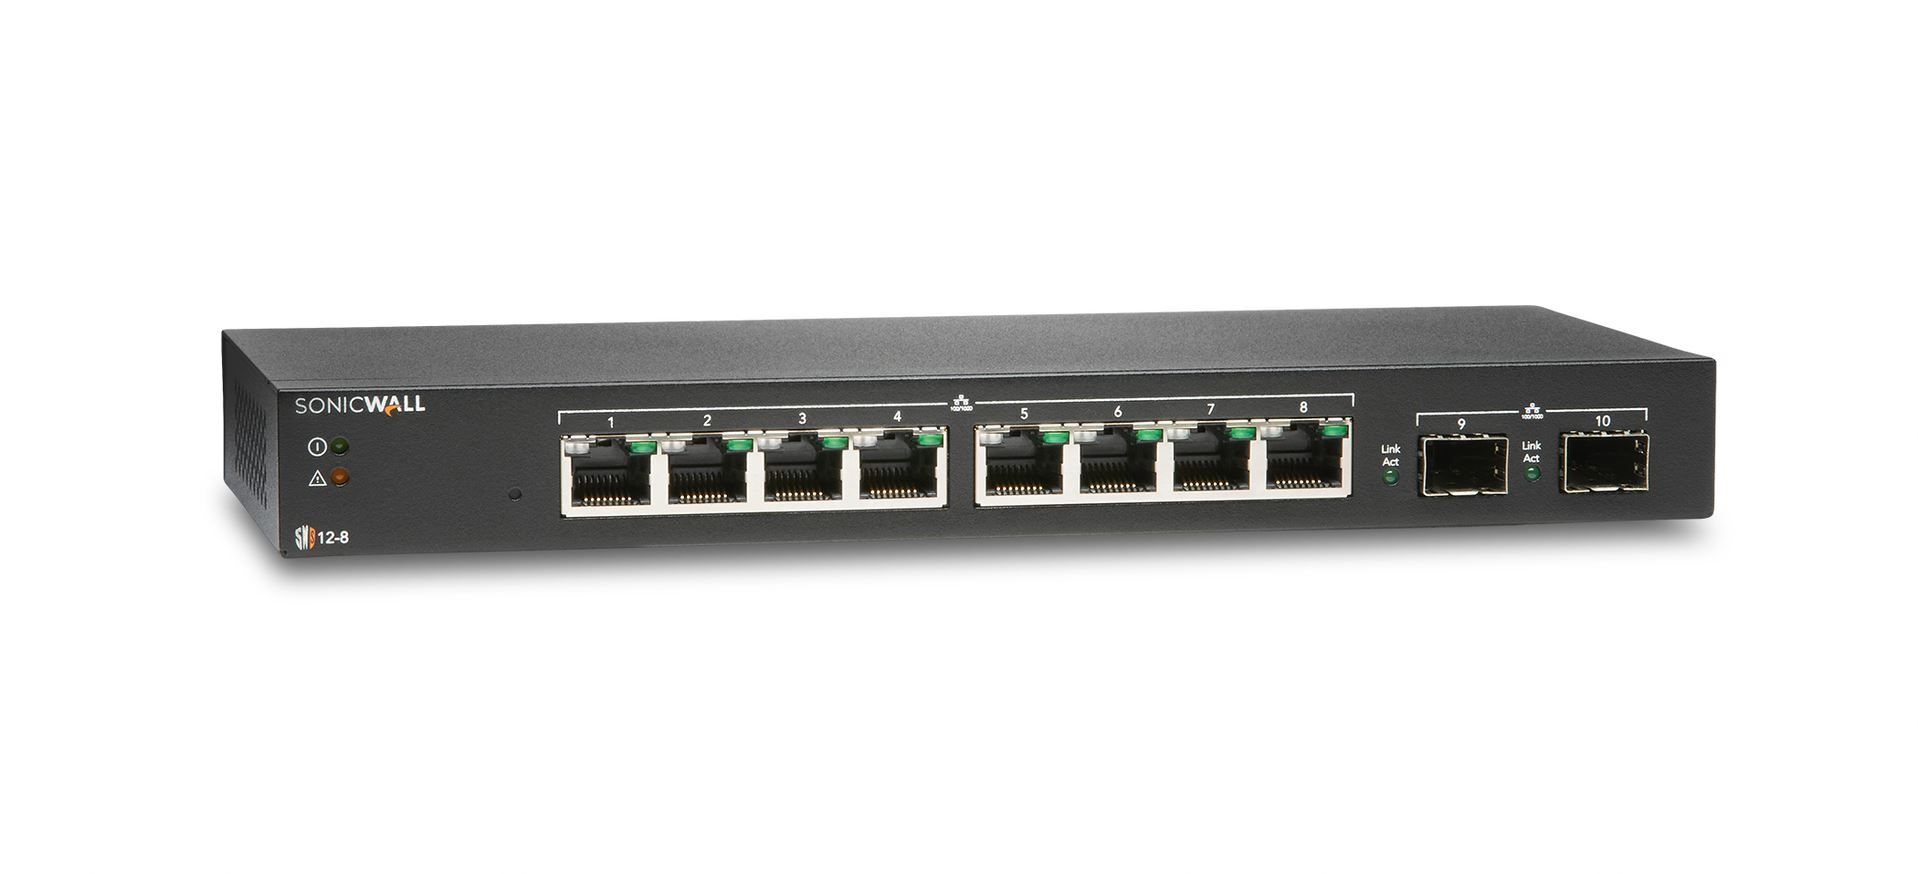
Compact, fanless Gigabit switch for connecting eight wired devices, with two SFP uplinks and no PoE power supply.
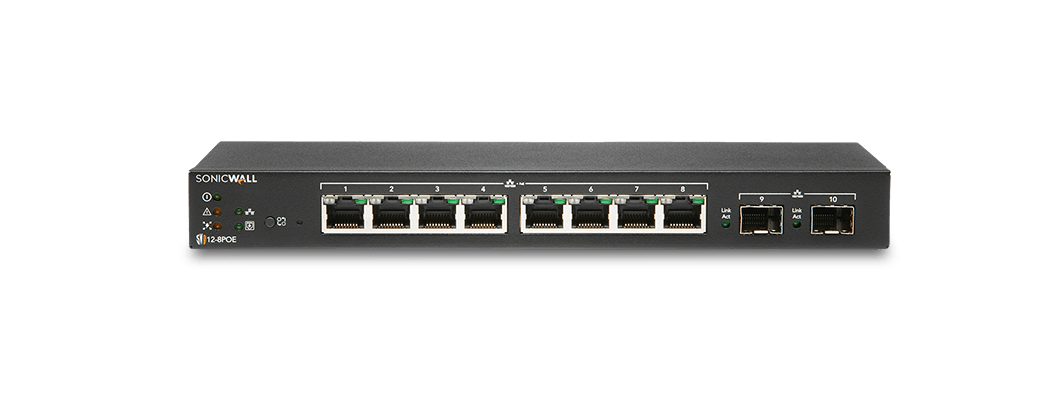
Compact eight-port Gigabit switch with 802.3af PoE, suited to low-power devices within the 55 W budget.
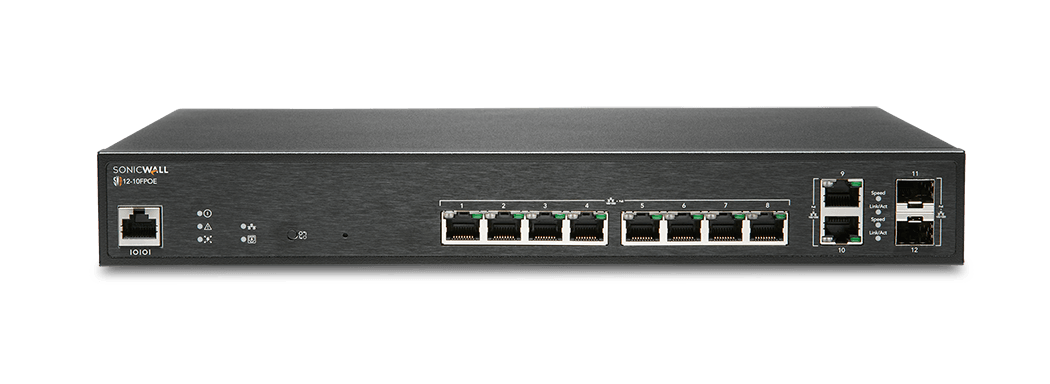
Switch with ten Gigabit ports, eight with PoE+, two SFP uplinks and a 130 W power budget.
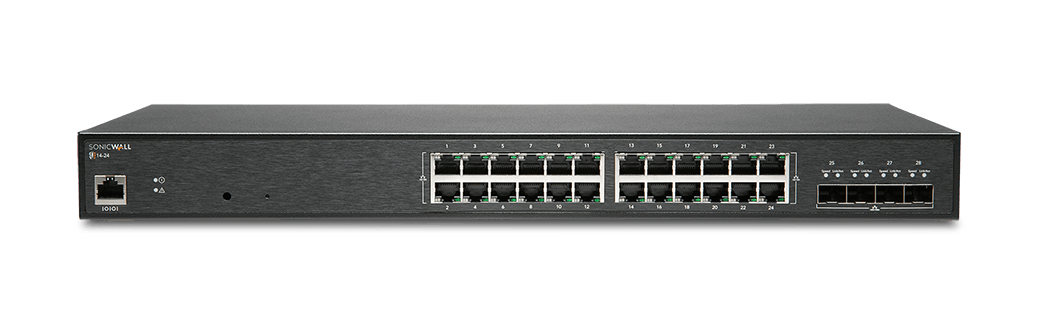
1U rack-mount switch for 24 Gigabit connections, with four 10 GbE uplinks and passive cooling.
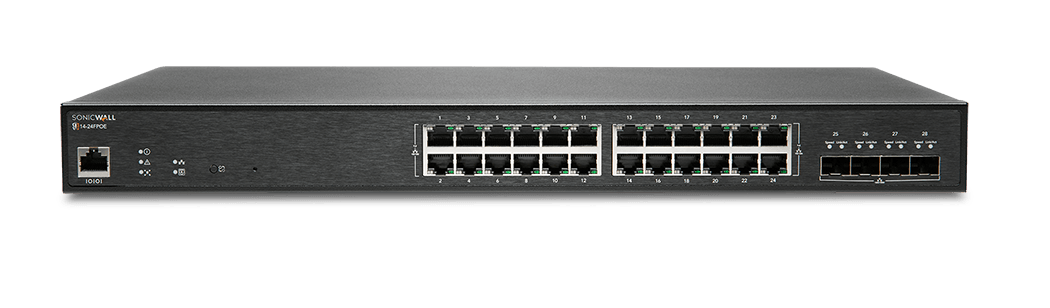
Rack-mount switch with 24 Gigabit PoE+ ports and a 410 W aggregate power budget for compatible APs, telephony devices and cameras.
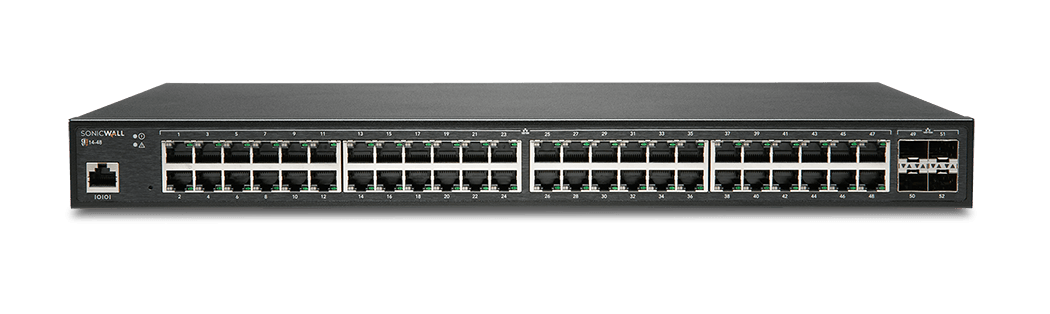
High-density access switch with 48 Gigabit ports and four 10 GbE uplinks, in a 1U rack-mount form factor.
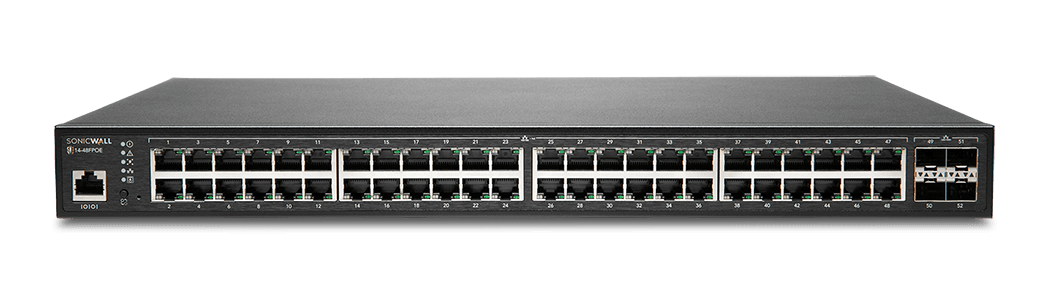
Rack-mount switch with 48 Gigabit PoE+ ports and four 10 GbE uplinks to aggregate powered network devices.
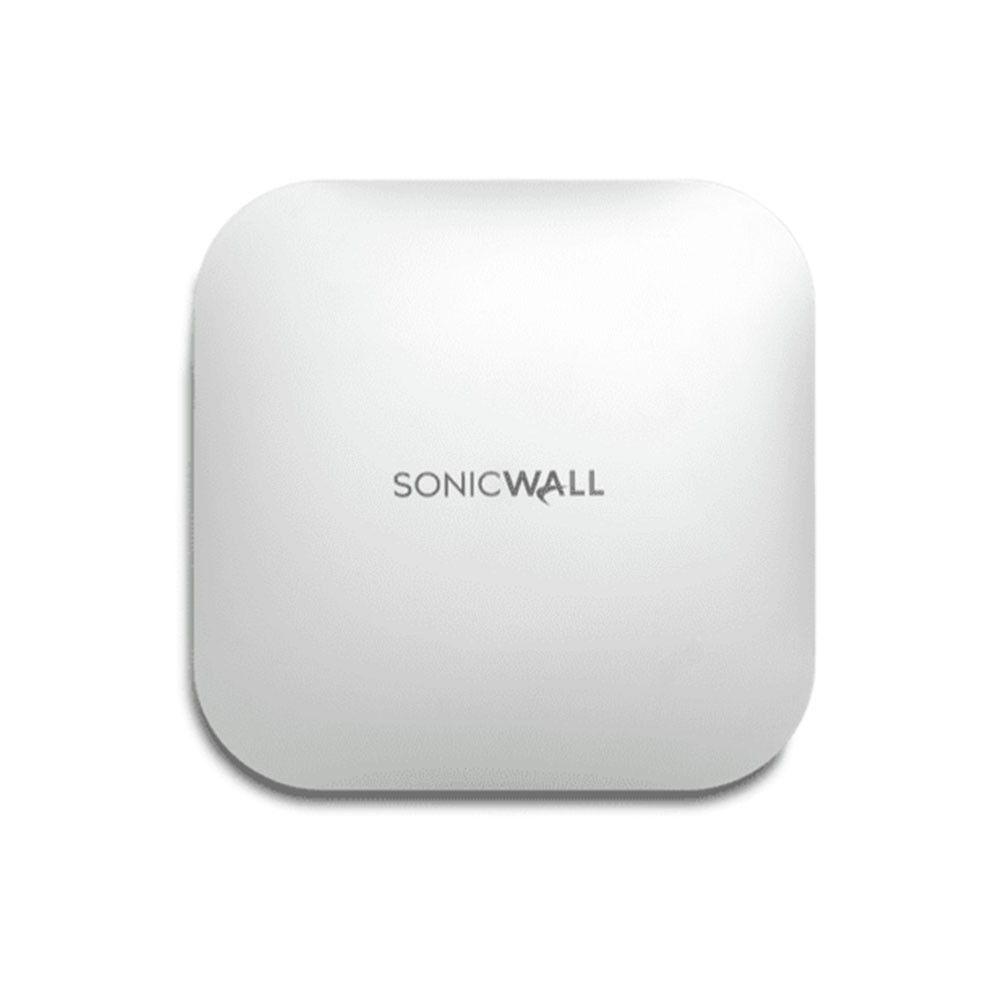
Indoor Wi-Fi 6 2×2 access point with a 2.5 GbE uplink, suited to designs that need to separate wireless access from radio monitoring.
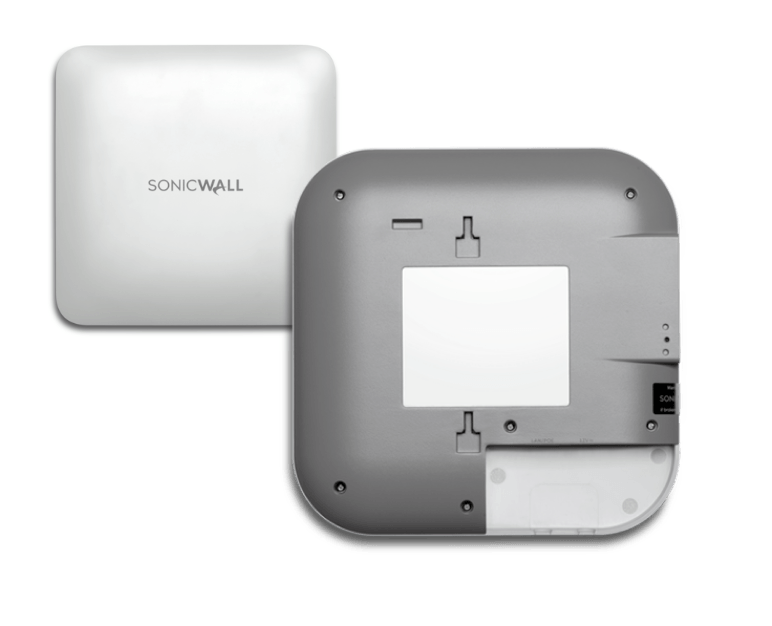
Indoor Wi-Fi 6 AP with four streams per band, a 2.5 GbE uplink and PoE+, for increased radio capacity in corporate networks.
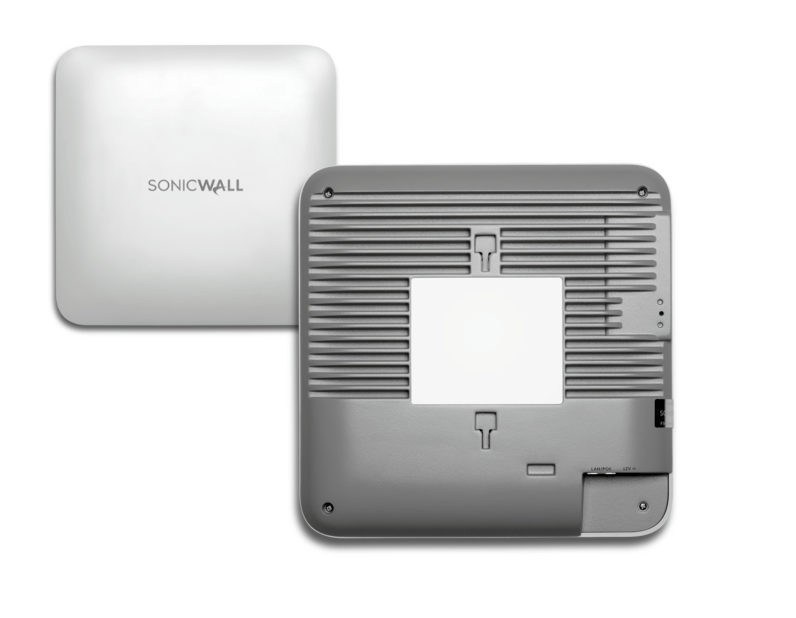
Indoor Wi-Fi 6 AP with eight streams at 5 GHz, four at 2.4 GHz and a 5 GbE uplink for higher-density projects.
Uma especificação isolada não dimensiona um projeto. Topologia, tráfego real, inspeção criptografada, serviços, VPN, redundância e expansão precisam ser avaliados em conjunto.