FortiGate 30G integrates network security and connectivity through FortiOS. Model selection should consider actual traffic, SSL inspection, FortiGuard services, VPN, high availability and environment growth.
Key features
Published performanceMaximum figures from the official Fortinet matrix for July 2026.
Engineering-based sizingFinal sizing accounts for active services, topology, redundancy and expansion.
Security FabricIntegration with the Fortinet ecosystem according to the defined architecture.
Technical specifications
Performance
Firewall IPv4 — UDP 1518/512/64 bytes
4 / 4 / 3.9 GbpsMaximum “up to” values; actual performance varies with configuration and network conditions. Internal manufacturer laboratory tests.
Firewall IPv6 — UDP 1518/512/86 bytes
4 / 4 / 3.9 GbpsMaximum “up to” values; actual performance varies with configuration and network conditions. Internal manufacturer laboratory tests. The third IPv6 packet size is published as 86 bytes.
Packet forwarding
5.85 MppsMaximum “up to” values; actual performance varies with configuration and network conditions. Internal manufacturer laboratory tests.
Firewall latency
2.87 μs64-byte UDP packets. Laboratory results; actual performance varies with configuration and network conditions.
IPS
800 MbpsEnterprise Traffic Mix; logging enabled. Maximum “up to” values; actual performance varies with configuration and network conditions. Internal manufacturer laboratory tests.
NGFW
570 MbpsFirewall, IPS and Application Control enabled; logging enabled; Enterprise Traffic Mix. Maximum “up to” values; actual performance varies with configuration and network conditions. Internal manufacturer laboratory tests.
Threat Protection
500 MbpsFirewall, IPS, Application Control and Malware Protection enabled; logging enabled; Enterprise Traffic Mix. Maximum “up to” values; actual performance varies with configuration and network conditions. Internal manufacturer laboratory tests.
Application control
830 MbpsHTTP 64 KB, logging enabled. Maximum “up to” values; actual performance varies with configuration and network conditions. Internal manufacturer laboratory tests.
SSL inspection — throughput
400 MbpsIPS; average across HTTPS sessions with different cipher suites. Maximum “up to” values; actual performance varies with configuration and network conditions. Internal manufacturer laboratory tests.
SSL inspection — new connections
260 CPSIPS; average across HTTPS sessions with different cipher suites. Maximum “up to” values; actual performance varies with configuration and network conditions. Internal manufacturer laboratory tests.
SSL inspection — concurrent sessions
55,000IPS; average across HTTPS sessions with different cipher suites. Maximum “up to” values; actual performance varies with configuration and network conditions. Internal manufacturer laboratory tests.
IPsec VPN — throughput
3,5 Gbps512-byte packets; AES256-SHA256. Maximum “up to” values; actual performance varies with configuration and network conditions. Internal manufacturer laboratory tests.
CAPWAP — throughput
Not published (TBA)HTTP 64 KB; the datasheet retains the value as TBA.
Capacity and VPN
Concurrent TCP sessions
600,000
New TCP sessions per second
30,000
Firewall policies
2.000
Site-to-site IPsec tunnels
200
Client-to-gateway IPsec tunnels
250
SSL-VPN — throughput and users
Not specified: the datasheet uses a dash; do not interpret this as zero capacity
VDOMs
Not supported
Managed FortiSwitches — maximum
8
Managed FortiAPs — total/tunnel
16 / 8
FortiTokens — maximum
500
High availability
Active-passive and active-active
Interfaces and hardware
Data Ethernet ports
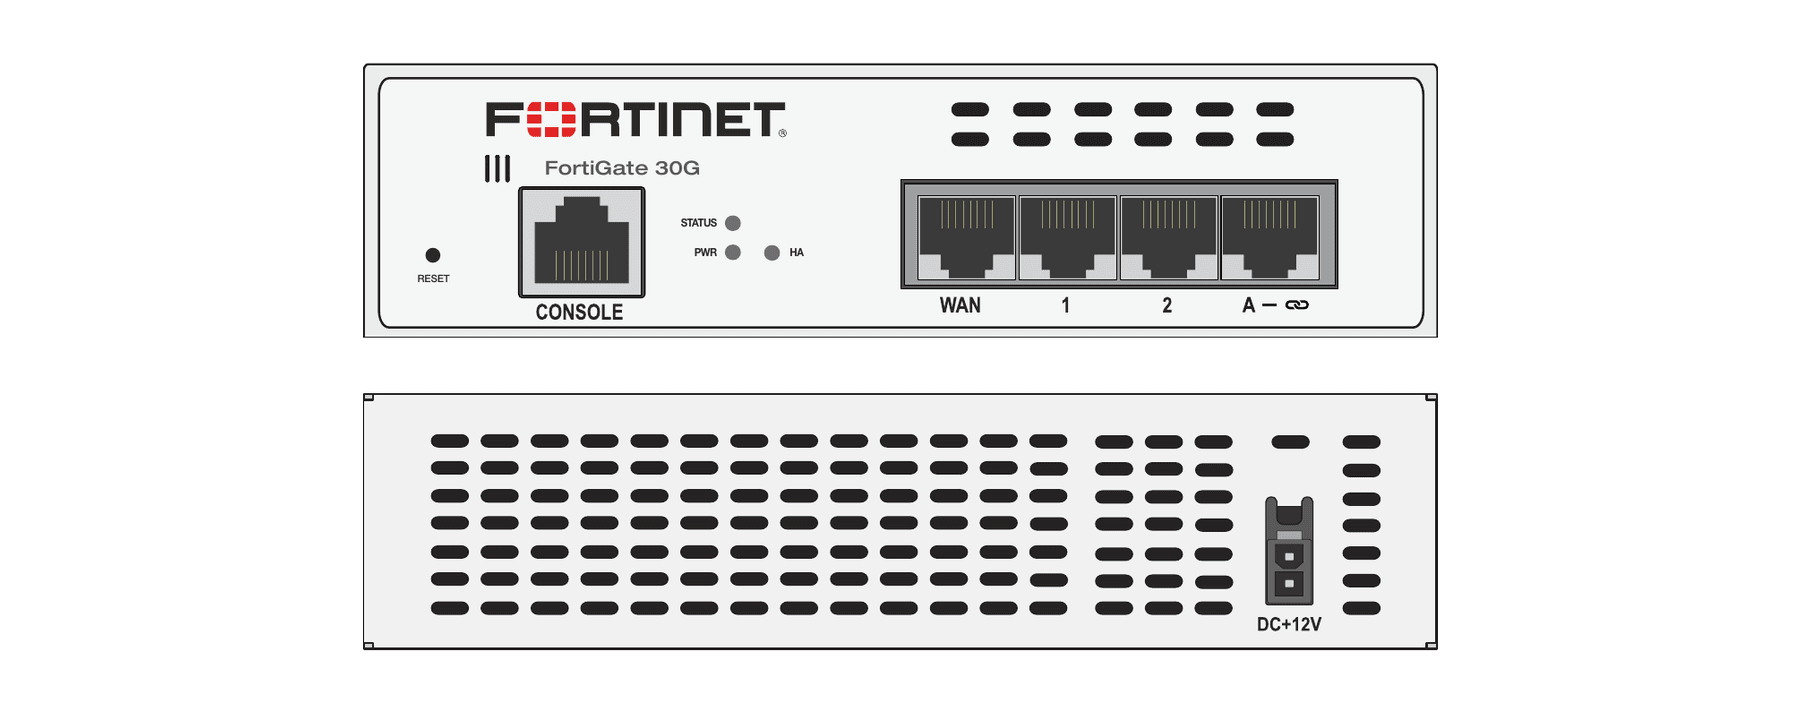
4 × GE RJ45 (1 Gbps): 1 WAN, 2 LAN and 1 FortiLink
Console
1 × RJ45
USB
Not equipped; marked with a dash for the FG-30G
SFP/SFP+/QSFP and DAC
Not listed; FG-30G data interfaces are RJ45 GE
Dedicated management
No dedicated Ethernet management port listed
Local storage
FG-30G: no data SSD listed; FG-31G: 30 GB SSD
Hardware acceleration and security
SoC4/SP4 e TPM
Integrated Wi-Fi
Not on the FG-30G; FortiWiFi FWF-30G/FWF-31G variants offer Wi-Fi 6 (802.11ax)
PoE e modem celular 5G
Not listed for the FG-30G
Installation and power
Dimensions (H × W × D)
40.5 × 142 × 160 mm
Weight
0.6 kg
Form factor and mounting
Desktop; optional wall mounting; rack: N/A
Power supply
12 V DC, 2 A; external 100–240 V AC adapter, 50/60 Hz
Redundant power supplies
Not specified for the FG-30G; the datasheet describes an external DC adapter
Average / maximum power consumption
6.8 / 8.2 W
Maximum current
100 V / 0.11 A; 240 V / 0.055 A (values published for the FG-30G)
SD-WAN and a network controller are included in the appliance; FortiGuard subscriptions and FortiCare support depend on the purchased package. Application Control is listed as included with a FortiCare subscription.
Feature restrictions by model
CDR, Video Filtering and Inline CASB are listed as unavailable on the 30G series in any FortiOS build.
Lifecycle
The datasheet does not state End of Order / End of Support; confirm SKU milestones on the official portal before purchasing.
SSL-VPN and FortiOS version
SSL-VPN tunnel mode was removed from all models as of FortiOS 7.6.3 and replaced by IPsec VPN. SSL inspection is a separate function.
Figures published by the manufacturer. Final sizing depends on the environment, enabled services and traffic profile.