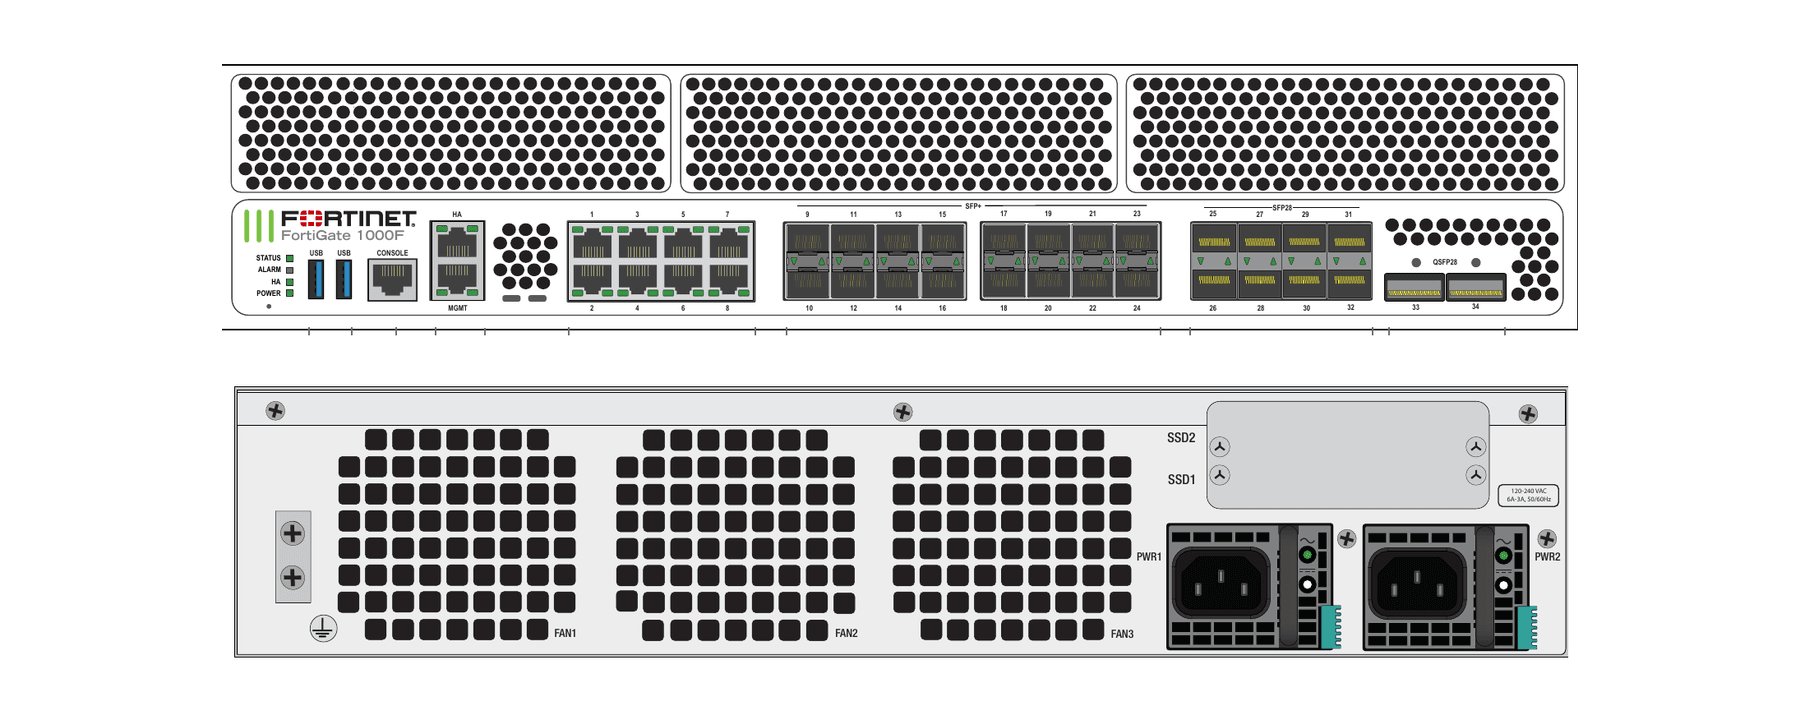
FortiGate 1000F integrates network security and connectivity through FortiOS. Model selection should consider actual traffic, SSL inspection, FortiGuard services, VPN, high availability and environment growth.
Key features
Published performanceMaximum figures from the official Fortinet matrix for July 2026.
Engineering-based sizingFinal sizing accounts for active services, topology, redundancy and expansion.
Security FabricIntegration with the Fortinet ecosystem according to the defined architecture.
Technical specifications
Interfaces and hardware
Accelerated ports — 100 GE QSFP28 / 40 GE QSFP+ slots
2
Accelerated ports — 25 GE SFP28 / 10 GE SFP+ / GE SFP slots
8
Accelerated ports — 10 GE SFP+ / GE SFP slots
16
Accelerated ports — 10 GE / 5 GE / 2.5 GE / GE / 100M RJ45 slots
8
2.5 GE / GE HA port
1
GE RJ45 management ports
1
USB (client / server)
2 / 2
Console
1
Local storage
FG-1000F: no local data SSD is listed. Variant FG-1001F: 2 × 480 GB.
Dedicated TPM
Yes
Bluetooth Low Energy (BLE)
Yes
Physical signed-firmware switch
Dash in the datasheet: feature not listed for this SKU
Included transceivers
2x SFP SX
Hardware acceleration
NP7 / CP9
Documented optional DAC cables
25 GE SFP28 passive DAC cable (FN-CABLE-SFP28-1); 25 GE SFP28 passive DAC cable (FN-CABLE-SFP28-3); 25 GE SFP28 passive DAC cable (FN-CABLE-SFP28-5); 100 GE QSFP28 passive DAC cable, 1m (FN-CABLE-QSFP28-1); 100 GE QSFP28 passive DAC cable, 2m (FN-CABLE-QSFP28-2); 100 GE QSFP28 passive DAC cable, 3m (FN-CABLE-QSFP28-3); 100 GE QSFP28 Breakout to 4x 25 GE SFP28 Passive (FN-CABLE-QSFP28-4SFP28-1); 100 GE QSFP28 Breakout to 4x 25 GE SFP28 Passive (FN-CABLE-QSFP28-4SFP28-3); 100 GE QSFP28 Breakout to 4x 25 GE SFP28 Passive (FN-CABLE-QSFP28-4SFP28-5)
PoE, Wi-Fi and cellular connectivity
PoE output, a Wi-Fi radio and a 5G cellular modem are not listed for this SKU in the datasheet consulted.
Performance
IPS
19 GbpsEnterprise Traffic Mix; logging enabled. Manufacturer laboratory results; actual performance varies with configuration and traffic. Throughput is advertised as a maximum (up to).
NGFW
15 GbpsEnterprise Traffic Mix; firewall, IPS and Application Control enabled; logging enabled. Manufacturer laboratory results; actual performance varies with configuration and traffic. Throughput is advertised as a maximum (up to).
Threat Protection
13 GbpsEnterprise Traffic Mix; firewall, IPS, Application Control and Malware Protection enabled; logging enabled. Manufacturer laboratory results; actual performance varies with configuration and traffic. Throughput is advertised as a maximum (up to).
Firewall IPv4 — UDP 1518/512/64 bytes
198 / 196 / 134 GbpsLaboratory results; actual performance varies with configuration and traffic. UDP packets of the sizes specified in the metric.
Firewall IPv6 — UDP 1518/512/86 bytes
198 / 196 / 134 GbpsLaboratory results; actual performance varies with configuration and traffic. UDP packets of the sizes specified in the metric.
Firewall latency — UDP 64 bytes
3.45 μsLaboratory results; actual performance varies with configuration and traffic. UDP packets of the sizes specified in the metric.
Packet forwarding
201 MppsLaboratory results; actual performance varies with configuration and traffic.
IPsec VPN — throughput (512 bytes)
55 Gbps512-byte packets; AES256-SHA256 encryption. Manufacturer laboratory results; actual performance varies with configuration and traffic. Throughput is advertised as a maximum (up to).
SSL-VPN — historical throughput
5,3 GbpsPublished historical capacity; SSL-VPN tunnel mode was removed from all models as of FortiOS 7.6.3 and replaced by IPsec VPN. SSL inspection is a separate function.
SSL inspection — throughput
10 GbpsIPS; average across HTTPS sessions with different cipher suites. Manufacturer laboratory results; actual performance varies with configuration and traffic. Throughput is advertised as a maximum (up to).
SSL inspection — new connections/s
11 000IPS; average across HTTPS sessions with different cipher suites. Manufacturer laboratory results; actual performance varies with configuration and traffic. Throughput is advertised as a maximum (up to).
SSL inspection — concurrent sessions
600 000IPS; average across HTTPS sessions with different cipher suites. Manufacturer laboratory results; actual performance varies with configuration and traffic. Throughput is advertised as a maximum (up to).
Application control — HTTP 64 KB
44 GbpsHTTP 64 KB; logging enabled. Manufacturer laboratory results; actual performance varies with configuration and traffic. Throughput is advertised as a maximum (up to).
CAPWAP — throughput (HTTP 64 KB)
65 GbpsHTTP 64 KB. Manufacturer laboratory results; actual performance varies with configuration and traffic. Throughput is advertised as a maximum (up to).
10 000Published historical capacity; SSL-VPN tunnel mode was removed from all models as of FortiOS 7.6.3 and replaced by IPsec VPN. SSL inspection is a separate function.
VDOMs — default / maximum
10 / 250
Managed FortiSwitches — maximum
196
Managed FortiAPs — total / tunnel
4096 / 2048
FortiTokens — maximum
20 000
High availability
Active-Active, Active-Passive, Clustering
Installation and power
Dimensions (H × W × D), inches
3.5 x 17.44 x 17.63
Dimensions (H × W × D), mm
88.9 x 443 x 447.4
Weight
21.94 lbs (9.95 kg)
Form factor and mounting
Rack, 2RU
AC power supply
100–240VAC, 50/60 Hz
Maximum AC current
6A@120VAC, 3A@240VAC
Power consumption — average / maximum
210 W / 408 W
Heat dissipation
1211 BTU/h
Power supply efficiency
80Plus-compatible
Redundant power supplies (hot-swap)
Yes (2 power supplies included from the factory)
Operating temperature
32°F to 104°F (0°C to 40°C)
Storage temperature
-31°F to 158°F (-35°C to 70°C)
Humidity
10% to 90%, non-condensing
Noise
66.7 dBA
Airflow
Front-to-rear airflow
Operating altitude
Up to 10 000 ft (3048 m)
Compliance
FCC Part 15 Class A, RCM, VCCI, CE, UL/cUL, CB
Certifications
USGv6/IPv6
Licensing and lifecycle
FortiGuard licensing and support
FortiGuard services and FortiCare support depend on the purchased bundle or subscription; hardware alone does not imply that all services are included.
SSL-VPN and FortiOS version
Published historical capacity; SSL-VPN tunnel mode was removed from all models as of FortiOS 7.6.3 and replaced by IPsec VPN. SSL inspection is a separate function.
Lifecycle and document review
End of Order / End of Support are not stated in this datasheet; confirm the official milestones for each SKU before purchasing.
Figures published by the manufacturer. Final sizing depends on the environment, enabled services and traffic profile.